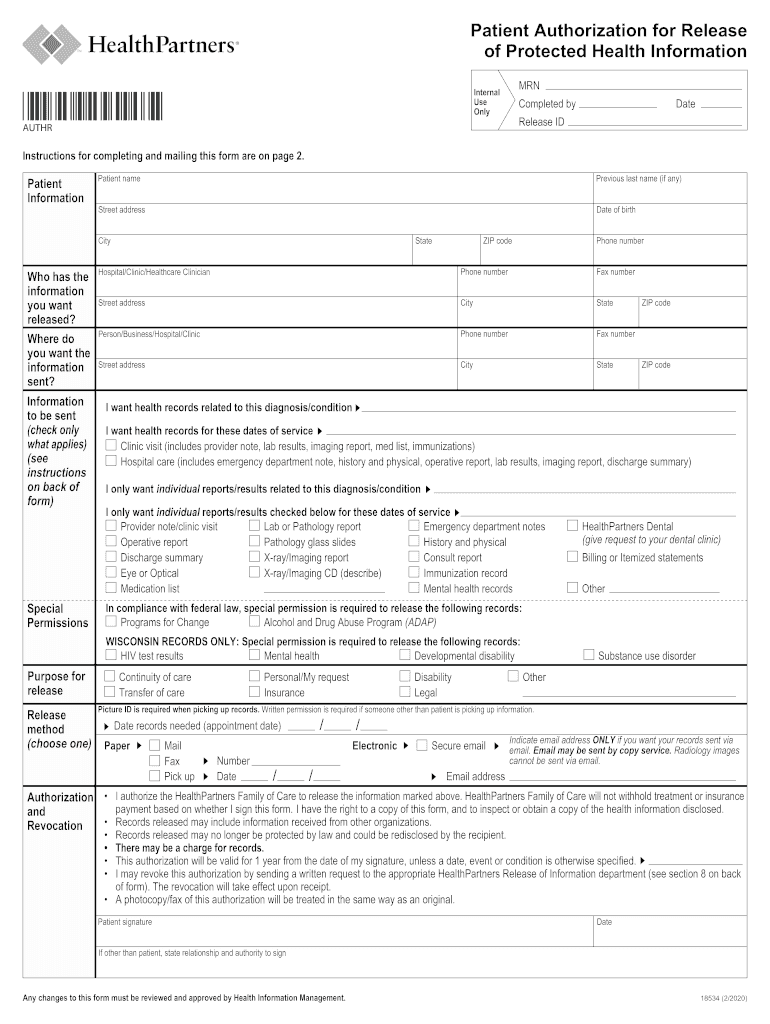
Patient Authorization For Release Of Protected Health Information Healthpartners
Use a Patient Authorization For Release Of Protected Health Information HealthPartners 2020 template to make your document workflow more streamlined.
What the HealthPartners authorization does
The Patient Authorization For Release Of Protected Health Information Healthpartners form gives a patient a documented way to permit HealthPartners to disclose specified protected health information to a named person or organization. The patient identifies the information, recipient, purpose, and authorization terms, then signs and dates the form. HealthPartners uses the completed authorization to evaluate whether the requested disclosure is permitted under HIPAA. signNow can route the form for electronic signature, capture completion evidence, and preserve the signed record, but the organization must still verify the form’s scope and any applicable state requirements before releasing information.
Who uses this HealthPartners authorization
Patients
HealthPartners patients use this authorization to identify the person or organization allowed to receive specified protected health information, including the purpose and expiration terms.
HealthPartners teams
HealthPartners privacy and medical-records teams review the signed authorization before disclosing the information, preserving the form and supporting audit evidence.
Complete the HealthPartners authorization in signNow
Use the original HealthPartners form, verify every disclosure field, then collect the patient’s informed signature before releasing protected health information.
Upload form:
Upload the current HealthPartners authorization PDF. Check fields:
Review detected fields and add missing patient, recipient, and signature fields. Send securely:
Enter the authorized recipient’s email address and send the document. Patient signs:
Have the patient review the scope, sign, and date the authorization. Store record:
Download the completed authorization and retain its audit trail.
Privacy and disclosure pitfalls to avoid
A missing patient name, date range, or recipient can make the authorization too narrow for HealthPartners to disclose the intended protected health information. Listing broad categories such as all medical records may expose more protected health information than the patient intended to release. An unsigned authorization or missing patient signature date leaves HealthPartners without clear evidence of consent for the requested disclosure. Sending the completed form through an unapproved channel can expose protected health information despite a properly completed authorization.
 Best ROI. Our customers achieve an average 7x ROI within the first six months.
 Scales with your use cases. From SMBs to mid-market, airSlate SignNow delivers results for businesses of all sizes.
 Intuitive UI and API. Sign and send documents from your apps in minutes.
Recommended setup for HealthPartners authorizations
Configure the HealthPartners authorization workflow around patient identity, limited disclosure, auditability, and HIPAA documentation requirements.
| Setting | Recommendation |
|---|---|
| Authentication method | Email verification with SMS OTP |
| Signature type | Typed or drawn electronic signature |
| Audit trail | Export with completed authorization |
| Document retention | 6 years under HIPAA 45 CFR 164.530(j) |
| Encryption | TLS 1.2/1.3 and AES-256 at rest |
Security controls for protected health information
HIPAA compliance:
Security report:
Information security:
Stored data:
Data in transit:
Signer verification:
Find and fill out the correct patient authorization for release of protected health information healthpartners
airSlate SignNow helps you fill in and sign documents in minutes, error-free. Choose the correct version of the editable PDF form from the list and get started filling it out.
| Versions | Form popularity | Fillable & printable |
|---|---|---|
| HealthPartners Form 18534 2020 | 4.8 Satisfied (4838 Votes) |
What the HealthPartners audit trail records
The audit trail documents the technical events behind this authorization without replacing review of the patient’s disclosure scope.
Authenticate signer:
Capture timestamps:
Record document history:
Seal completion:
Export evidence:
Archive securely:
Use the HealthPartners authorization on mobile
Complete the HealthPartners authorization in a supported browser or signNow mobile app on iOS or Android, using TLS-protected access and camera capture when digitizing paper pages.
Mobile apps iOS and Android apps Offline mode Offline signing available Camera capture Camera document capture
For regulated healthcare workflows, use managed iOS or Android devices, restrict downloaded copies, and confirm that the selected signNow plan and business associate agreement meet your organization’s HIPAA requirements. Offline work should be synchronized and reviewed before disclosure.



Best practices for signed HealthPartners authorizations
Use the completed authorization, audit trail, and disclosure record as one controlled file, while applying HIPAA’s six-year documentation rule where it governs the record.
Retain the authorization under HIPAA’s six-year rule
Export the audit trail with every completed form
Restrict access to protected health information
Verify every disclosure field before release
Retention schedule for HealthPartners records
HIPAA sets a six-year documentation period for covered-entity policies and procedures; state law and organizational policy may require longer retention for this authorization and its disclosure record.
6 years for HIPAA records
6 years for disclosure documentation
Longer period under state law
Through authorization expiration
With related disclosure records
Troubleshooting HealthPartners authorization workflows
Resolve field, identity, delivery, and disclosure issues before HealthPartners releases protected health information.
Upload the current HealthPartners PDF again and confirm that required patient, recipient, purpose, and signature fields were detected. On signNow Business, manually place any missing fields before sending; do not assume OCR created legally sufficient authorization language.
A signNow Business workflow can use email verification, while stronger patient identity controls may require SMS OTP or an Enterprise configuration. HIPAA compliance also requires a business associate agreement where signNow handles protected health information for the covered entity.
Check whether the signer’s email is correct, resend the invitation, or use a controlled signing link. The patient must review the HealthPartners disclosure scope and intentionally sign; staff should not sign on the patient’s behalf.
Use signNow’s audit trail and completed-document download to preserve timestamps, delivery events, and signer activity. Store both files with the HealthPartners disclosure record and restrict access to authorized personnel.
Business Premium includes bulk send, but a single patient authorization normally requires an individual review of recipient, purpose, and information scope. Do not use bulk distribution when each HealthPartners disclosure requires patient-specific details.
A signed authorization does not automatically permit every disclosure. HealthPartners should compare the requested release with the authorization’s named recipient, information categories, purpose, expiration, and applicable HIPAA and state-law requirements before sending records.
Key performance indicators that demonstrate SignNow's proven track record.
BE READY TO GET MORE
Get this form now!

If you believe that this page should be taken down, please follow our DMCA take-down process.