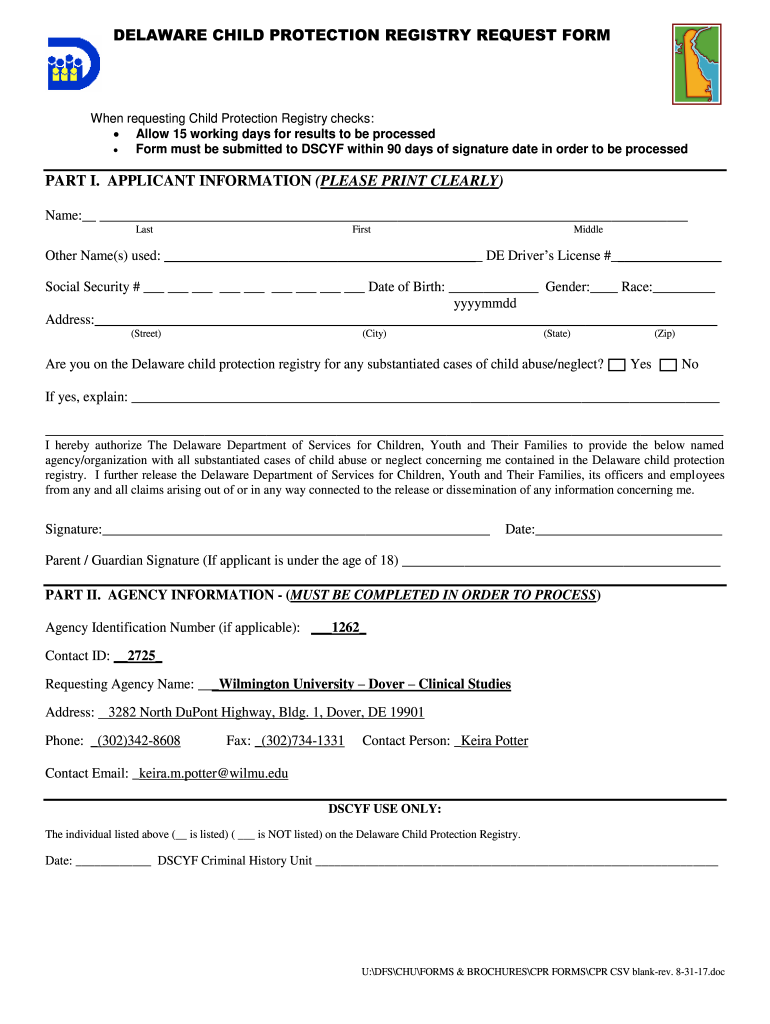
Background Checks In The University Admissions Process
Use a Background Checks In The University Admissions Process 2019 template to make your document workflow more streamlined.
Background checks in admissions explained
Background checks in the university admissions process are institution-specific authorization and disclosure records used before an admissions office or program reviews permitted screening information. They commonly identify the applicant, explain the screening purpose, disclose required rights or notices, and capture consent, acknowledgment, and signatures. This is not a single federally standardized U.S. form with one issuing agency or universal deadline. An institution can upload its approved document to signNow, review detected fields, send it to the applicant, collect an eSignature, and retain the signed record with an audit trail. FERPA, state privacy law, and program rules determine handling requirements.
Roles managing admissions background checks
University admissions compliance officers coordinate applicant consent, identity checks, and reviewer access. They use reusable signNow templates to route background-check authorizations, capture required signatures, and preserve an auditable record without exposing applicant information to every department. Graduate program administrators and clinical-placement coordinators manage applicants whose records require additional review. They send institution-specific authorization packets through signNow, use signer authentication when appropriate, and store completed documents with controlled access for admissions and placement decisions.
Who uses these admissions documents
Admissions offices
Admissions offices can use signNow for applicant background-check authorization forms, disclosure acknowledgments, consent records, and reviewer attestations. Each workflow should identify the applicant, limit access to authorized personnel, and preserve the completed record and audit trail under the institution’s FERPA policy and applicable state privacy requirements.
Program administrators
Graduate programs, clinical-placement teams, and campus employment offices can route consent forms, disclosure notices, and authorization acknowledgments through signNow. Their workflows should separate applicant-facing documents from internal decisions, restrict access by role, and retain records according to institutional policy rather than assuming one federal schedule applies.
Features for admissions background checks
signNow connects document preparation, applicant authentication, eSignature, and audit evidence in one workflow for institution-specific background-check authorizations.
Field detection
Upload the institution’s existing authorization packet, then review signNow’s detected fields before adding applicant-specific signature, initials, date, and consent fields.
Audit trail
Send each applicant a controlled signing request and record delivery, viewing, signing, and completion events in the document history for later review.
Signer authentication
Use SMS-based authentication or other available signer controls when the institution’s risk assessment requires stronger evidence that the applicant accessed the authorization.
Reusable templates
Create reusable templates for recurring admissions programs while keeping applicant names, disclosures, and background-check details separated for each signing request.
Secure storage
Keep completed authorizations in signNow and export records for the institution’s approved archive, supporting controlled access and consistent record handling.
Mobile signing
Use signNow mobile apps when applicants or authorized staff need to complete the authorization away from a desktop, subject to institutional device policies.
How the admissions workflow works
The process moves from document preparation to controlled applicant signing, then preserves the completed authorization and its audit evidence.
Upload document: Upload the institution’s background-check authorization PDF to signNow. Place fields: Review detected fields and add applicant-specific signature fields. Send securely: Send the authorization to the applicant through signNow. Archive record: Store the signed record and audit trail with restricted access.
 Best ROI. Our customers achieve an average 7x ROI within the first six months.
 Scales with your use cases. From SMBs to mid-market, airSlate SignNow delivers results for businesses of all sizes.
 Intuitive UI and API. Sign and send documents from your apps in minutes.
Recommended admissions workflow setup
Configure the authorization workflow around applicant identity, limited admissions access, documented consent, and the institution’s approved retention policy.
| Setting | Recommendation |
|---|---|
| Authentication method | Email invitation with SMS verification |
| Signature type | Electronic signature with applicant intent |
| Audit trail | Enabled for every authorization |
| Document retention | Institutional FERPA policy and state law |
| User provisioning | Role-based access for admissions staff |
What the audit trail records
A signNow audit trail documents the technical history of an applicant’s authorization separately from the institution’s admissions decision.
Authenticate signer:
Capture timestamps:
Hash document:
Seal document:
Track actions:
Export trail:
Find and fill out the correct background checks in the university admissions process
airSlate SignNow helps you fill in and sign documents in minutes, error-free. Choose the correct version of the editable PDF form from the list and get started filling it out.
| Versions | Form popularity | Fillable & printable |
|---|---|---|
| Wilmington University College of Education Clinical Procedures Manual 2020 | 4.8 Satisfied (1865 Votes) | |
| Wilmington University College of Education Clinical Procedures Manual 2019 | 4.8 Satisfied (241 Votes) |
Security for applicant authorizations
Transport encryption:
Stored encryption:
Security certification:
Information security:
Education records:
Health information:
Platform requirements for signing
Applicants can complete this admissions authorization in Chrome, Firefox, Safari, or Edge on Windows 10, Windows 11, or macOS. signNow also provides mobile apps for iOS 15 or later and Android 10 or later, with encrypted connections using TLS 1.2/1.3.
Supported browsers Chrome, Firefox, Safari, and Edge on Windows 10, Windows 11, and macOS. Mobile apps signNow mobile apps for iOS 15 or later and Android 10 or later. Camera capture Camera capture supports photographing applicant identification documents.
Institutions should manage mobile permissions, camera access, and device security through their own policies. Enterprise deployments may also require API access, SSO provisioning, managed-device controls, and configured audit or long-term validation settings. Confirm the selected plan and institutional security requirements before routing applicant identification or other sensitive information.
Record-keeping practices for admissions checks
A defensible record combines the signed authorization, access history, retention decision, and audit trail without assuming every admissions record follows the same federal schedule.
Set a documented retention schedule
Export the audit trail
Limit access to applicant records
Apply conditional HIPAA retention
Risks of mishandling applicant checks
Unclear consent
Excessive access
Missing audit trail
Incomplete notice
Legal standing of admissions authorizations
An electronic authorization can be admissible when the applicant intends to sign, consents to the electronic transaction, can be identified, and the institution retains a reproducible record under ESIGN and applicable UETA rules. This does not replace FERPA duties or authorize electronic execution of excluded documents such as wills, codicils, or court orders.

Troubleshooting admissions background-check workflows
Resolve invitation, authentication, privacy, and plan questions before releasing an applicant’s completed background-check authorization.
The Business plan includes templates, audit trails, mobile apps, and legally binding eSignatures at $8/user/month when billed annually. Business Premium adds bulk send at $15/user/month, which can help institutions distribute the same authorization packet to many applicants.
Use signNow’s audit trail and signer authentication features to document intent, attribution, timestamps, and actions. ESIGN and UETA recognize qualifying electronic signatures, while FERPA obligations still require the institution to limit education-record access appropriately.
If applicants do not receive an invitation, confirm the email address, resend the request, or create a signing link when appropriate. Business Premium includes quick invite links; the sender should still verify the applicant’s identity before collecting sensitive information.
Business Premium includes bulk send, while the Business plan does not list that feature. For individualized background-check authorizations, use a reusable template and send each packet separately unless the institution has confirmed its bulk workflow and privacy controls.
signNow supports two-factor authentication and audit trails, and its HIPAA compliance requires a BAA when protected health information is involved. FERPA-covered student records remain subject to institutional privacy policies and applicable education-record requirements.
The Business plan is listed at $8/user/month with annual billing and includes 100 signature invites per user per year. Subscription plans can incur per-invite overage fees, so review expected applicant volume before selecting a plan.
Key performance indicators that demonstrate SignNow's proven track record.
BE READY TO GET MORE
Get this form now!

If you believe that this page should be taken down, please follow our DMCA take-down process.