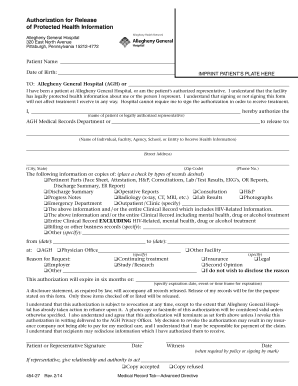
Authorization For Release Of Protected Health Information Ahn Org Ahn
Use a Authorization For Release Of Protected Health Information AHN org Ahn 2014 template to make your document workflow more streamlined.
What this health information authorization does
Authorization For Release Of Protected Health Information Ahn Org Ahn is a patient consent document that identifies the information a healthcare provider may disclose, the recipient, the purpose, and any expiration or revocation terms. The patient or legally authorized representative reviews those details and signs. A healthcare organization should confirm that the authorization meets applicable HIPAA requirements before releasing records. With signNow, the sender uploads the document, maps fields, sends it for signature, and preserves the completed file with its audit trail. HIPAA requires certain records to be retained for six years under 45 CFR 164.530(j).
Who uses this health information release form
Healthcare providers
Healthcare providers use the authorization to document a patient’s permission before sending specified medical records to another provider, insurer, attorney, family member, or agency. The signer should review the recipient, purpose, record categories, and expiration before completing the release.
Patients and representatives
Patients and authorized representatives use the form to control disclosure of protected health information. A representative should confirm legal authority, review every requested field, and retain a copy of the signed authorization and completion evidence.
Why teams look for DocuSign alternatives
Organizations seek alternatives when they need different pricing models, stronger native automation, simpler bulk affidavit workflows, or more flexible identity-verification options than those available in a legacy envelope-based vendor.

Complete and sign the authorization online
Use this sequence to prepare the protected health information release authorization, collect consent, and preserve evidence of completion.
Upload the form:
Upload the authorization PDF and review detected fillable fields before adding patient and representative information. Complete each field:
Complete the patient, recipient, purpose, record scope, expiration, and representative sections exactly as required. Send for signature:
Send the authorization to the patient or authorized representative through signNow for identity verification and signature. Archive the record:
Download the completed authorization and audit trail, then store both according to HIPAA retention requirements.
Recommended setup for protected health information
Configure this authorization around patient identity, documented consent, secure transmission, and HIPAA record retention.
| Setting | Recommendation |
|---|---|
| Authentication method | Two-factor authentication for patient identity |
| Signature type | Intent-based electronic signature with completion certificate |
| Audit trail | Capture timestamps, IP addresses, and signer actions |
| Document retention | Keep six years under HIPAA 45 CFR 164.530(j) |
| Encryption | TLS 1.2 or 1.3 and AES-256 |
 Best ROI. Our customers achieve an average 7x ROI within the first six months.
 Scales with your use cases. From SMBs to mid-market, airSlate SignNow delivers results for businesses of all sizes.
 Intuitive UI and API. Sign and send documents from your apps in minutes.
Security controls for protected health information
HIPAA protection:
Transport encryption:
Stored data:
Service controls:
Security management:
Consent evidence:
Mobile options for completing the authorization
The signNow mobile apps support Authorization For Release Of Protected Health Information Ahn Org Ahn on iOS and Android, including camera-based document capture and offline signing workflows. Use a managed device when patient information is present.
Mobile apps iOS and Android apps Offline signing Offline signing available Document capture Camera-based document capture
Healthcare teams should apply device encryption, screen locks, remote-wipe controls, and organization-approved authentication before handling completed authorizations. Confirm that offline copies synchronize securely, restrict access to authorized personnel, and preserve the final document and audit trail under the organization’s HIPAA retention policy.
Privacy pitfalls when releasing protected health information
Sending the authorization to an unintended recipient can expose patient identifiers and protected health information before consent is properly documented. A vague release description may not tell the recipient which records, dates, providers, or purposes the patient authorized. Missing patient signatures, dates, or representative authority can prevent a healthcare organization from relying on the authorization. Unrestricted access to completed authorizations can expose sensitive records to staff without a documented treatment, payment, or operations need.
Find and fill out the correct authorization for release of protected health information ahnorg ahn
airSlate SignNow helps you fill in and sign documents in minutes, error-free. Choose the correct version of the editable PDF form from the list and get started filling it out.
| Versions | Form popularity | Fillable & printable |
|---|---|---|
| Allegheny Health Network HIM-1000-001 2018 | 4.8 Satisfied (3798 Votes) | |
| Allegheny Health Network HIM-1000-001 2014 | 4.8 Satisfied (189 Votes) |
Rollout and retention for this authorization
A controlled rollout connects form preparation, patient consent, audit evidence, and the six-year HIPAA retention requirement.
Prepare the document:
Send the authorization:
Collect patient consent:
Verify completion:
Export audit evidence:
Secure the record:
HIPAA retention period:
Trial access:
Best practices for this release authorization
Accurate scope, documented consent, controlled access, and complete audit evidence reduce disclosure errors when this authorization is processed electronically.
Define the release scope precisely
Confirm signer identity and consent
Review and export completion evidence
Apply the HIPAA retention rule
What the audit trail records
The audit trail preserves technical evidence showing who interacted with the authorization, when events occurred, and how the completed record was finalized.
Authenticate signer:
Record timestamp:
Track actions:
Seal record:
Create certificate:
Retrieve evidence:
Check state rules before relying on electronic signatures
State rule
Wills and codicils
Court orders
Real-estate deeds
Features that support this authorization workflow
signNow combines form preparation, patient signing, authentication, audit evidence, mobile access, and connected storage for this protected health information authorization.
Field detection
Upload the authorization PDF and let signNow detect fields before you review placement and required entries.
Remote signing
Send the release to a patient or representative by email, then collect the required signature and date remotely.
Signer controls
Use controlled signer authentication and consent evidence appropriate for protected health information workflows.
Audit trail
Preserve timestamps, signer actions, and completion evidence with the authorization for later review.
Mobile access
Use signNow mobile apps to prepare or sign the authorization on iOS and Android devices.
System connections
Connect completed authorizations to approved storage or business systems through named signNow integrations.



Troubleshooting this health information authorization
These answers address field placement, HIPAA configuration, recipient security, plan selection, electronic validity, and record retention for this authorization.
Upload the original PDF again and review whether fields were detected as editable. If automatic detection misses a patient, recipient, purpose, or signature field, add it manually before sending. Business includes templates and audit trails; document-specific field placement remains the sender’s responsibility.
A healthcare workflow can use signNow’s HIPAA-compliant service when the required Business Associate Agreement is in place. HIPAA compliance does not validate the authorization’s wording, scope, or state-law requirements, so the covered entity must review those elements separately.
Use a fresh signing invitation or controlled link, verify the recipient address, and require appropriate authentication before the patient signs. If protected health information was sent to the wrong recipient, follow the organization’s incident-response and breach-assessment procedures.
The Business plan is listed at $8 per user per month with annual billing and includes audit trails, templates, and mobile apps. Business Premium is $15 per user per month annually and adds bulk send and kiosk mode; confirm plan suitability for the workflow.
signNow provides ESIGN and UETA compliance, but electronic validity still depends on intent, consent, attribution, and record retention. For consumer-facing electronic records, review the ESIGN consumer-disclosure requirements under 15 U.S.C. §7001(c).
Retain the authorization for six years from creation or the last effective date under 45 CFR 164.530(j). Export the signed document and audit trail, restrict access, and apply a longer period when state law or another applicable rule requires it.
Key performance indicators that demonstrate SignNow's proven track record.
BE READY TO GET MORE
Get this form now!

If you believe that this page should be taken down, please follow our DMCA take-down process.