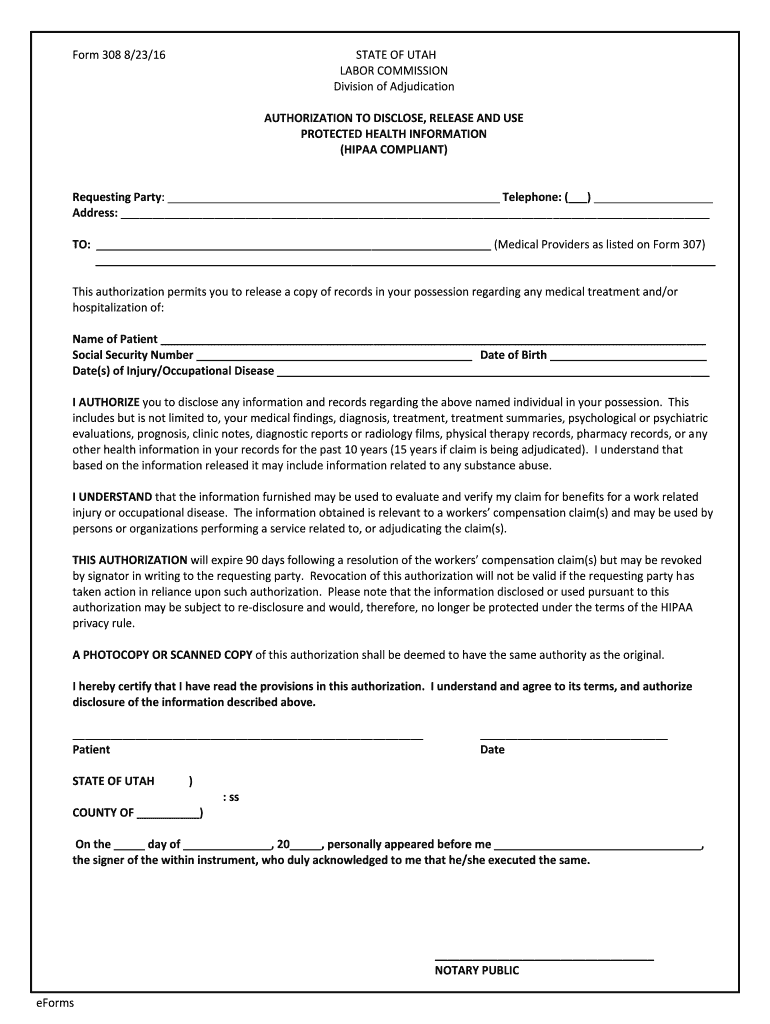
Authorization To Disclose Release And Use Protected Health
Use a Authorization To Disclose Release And Use Protected Health 2016 template to make your document workflow more streamlined.
What this health authorization does
Authorization To Disclose Release And Use Protected Health is a patient permission form for identifying what protected health information may be disclosed or used, who may receive it, why it may be shared, and when permission ends. The signer reviews those limits and executes the authorization, while the healthcare organization verifies that the requested disclosure matches the documented scope. signNow can upload the form, detect fillable fields, route it for signature, and preserve the signed record with an audit trail. HIPAA and applicable state law still govern the disclosure.
Organizations that use this form
The form is most useful where protected health information must be disclosed for a defined purpose and the signer’s permission must be documented.
Solo healthcare practices can collect patient permissions for defined disclosures without routing paper between offices. A reusable signNow template can preserve required fields while staff review each recipient, purpose, information category, and expiration before sending it for signature. Regional clinics can standardize authorization intake across locations, use role-based access, and retain signed records with audit trails. HIPAA-covered operations should pair the workflow with a BAA and six-year documentation retention under 45 CFR §164.530(j). Enterprise health systems can connect authorization workflows to systems such as Microsoft 365, Salesforce, or NetSuite while controlling delegated sending. Administrators can manage templates and permissions, but compliance teams must validate each disclosure purpose and state-law requirement.
These tasks are executed by both individual contributors and centralized administrators depending on organizational policy and required controls.
Who uses this health authorization
Healthcare providers
Healthcare providers use this authorization to document a patient’s permission for specified protected health information to be disclosed or used. The form should identify the information, recipient, purpose, expiration or event, and required signatures before release.
Patients and recipients
Patients, personal representatives, and authorized recipients review the scope before signing. Legal, insurance, and care-coordination teams can use the completed record when the disclosure is permitted and state privacy rules are satisfied.
How this health authorization works
The process connects the patient’s informed permission with a defined disclosure, then preserves evidence that the authorization was reviewed, signed, and retained.
Review scope: The patient reviews the information, recipient, purpose, and expiration stated in the authorization. Give consent: The patient provides electronic consent and signs through the configured signNow workflow. Verify permission: The healthcare organization verifies completion before releasing the permitted information. Retain evidence: Staff retain the signed authorization and audit evidence for later review.
How to complete this authorization
Use this sequence to prepare the health-information authorization, verify its scope, obtain the signer’s consent, and preserve the completed record.
Upload form:
Upload the Authorization To Disclose Release And Use Protected Health document. Check fields:
Review auto-detected fields and add missing signature or date fields. Add signer:
Enter the intended signer and verify the disclosure recipient details. Send form:
Send the authorization through signNow for review and signature. Store records:
Store the signed document with its completed audit trail.
How the authorization audit trail works
A signNow audit trail records technical evidence around this health-information authorization, separate from preparing fields or sending the document.
Signer authentication:
Timestamp capture:
Document hashing:
Tamper-evident sealing:
Event logging:
Audit export:
 Best ROI. Our customers achieve an average 7x ROI within the first six months.
 Scales with your use cases. From SMBs to mid-market, airSlate SignNow delivers results for businesses of all sizes.
 Intuitive UI and API. Sign and send documents from your apps in minutes.
Security for protected health information
HIPAA protection:
Transport encryption:
Stored encryption:
Control assurance:
Security certification:
Signing evidence:
Platform requirements for signing
Authorization To Disclose Release And Use Protected Health can be prepared through supported desktop browsers including Chrome, Firefox, Safari, and Edge on Windows or macOS. signNow also provides mobile apps for iOS and Android, allowing recipients to review and sign from supported mobile devices. Use a secure TLS connection and an organization-approved device when handling protected health information.
Browsers Chrome, Firefox, Safari, and Edge Desktop systems Windows and macOS desktops Mobile options iOS and Android mobile apps
Healthcare organizations should manage access through approved Windows, macOS, iOS, or Android devices and restrict downloaded copies to authorized personnel. Teams using API or SSO provisioning should confirm the selected signNow plan and integration configuration before deployment. HIPAA-covered organizations should also confirm the required business associate agreement and retention controls.
Find and fill out the correct authorization to disclose release and use protected health
airSlate SignNow helps you fill in and sign documents in minutes, error-free. Choose the correct version of the editable PDF form from the list and get started filling it out.
| Versions | Form popularity | Fillable & printable |
|---|---|---|
| *2016 UT Form 308 [2016-08-23] 2016 | 4.7 Satisfied (176 Votes) |



Best practices for this authorization
Accurate scope, controlled access, and preserved evidence help healthcare teams handle this authorization without expanding the permitted disclosure.
Identify every disclosure element
Review detected fields manually
Preserve the audit trail
Minimize exposed health information
Legal standing of the authorization
A completed electronic authorization can provide evidence when the signer intended to sign, consented to electronic records, can be identified, and the record remains reproducible under ESIGN and UETA. Those laws do not replace HIPAA or state disclosure rules, and electronic records do not cover excluded documents such as wills or certain court orders.

Risks of incomplete authorization
Invalid authorization
Scope ambiguity
Evidence gap
Privacy violation
Privacy pitfalls to avoid
Listing a broad recipient or purpose can make the requested disclosure unclear and may fail to document the patient’s intended permission. Sending the authorization to the wrong email address can expose protected health information before the recipient’s identity is confirmed. Omitting an expiration date or event can create uncertainty about whether the authorization remains effective for a later disclosure. Using a shared template without checking patient-specific fields can attach the wrong information scope, recipient, or purpose to the authorization.
Processing stages for this authorization
Processing depends on document review, signer access, and organizational records procedures rather than a fixed statutory turnaround period.
Prepare the document
Deliver to signer
Signer completes review
Complete and archive
Healthcare authorization use cases
Healthcare organizations use this form when a patient’s documented permission must accompany a defined disclosure of protected health information.
Fertility healthcare
Fertility Centers of Illinois selected airSlate SignNow for healthcare-related document workflows and API flexibility, according to its customer story.
- Healthcare document workflow
- API flexibility
- Signer access controls
The organization’s stated experience highlights responsive support, useful API capabilities, and a comfortable fit for its company. This example does not establish that every Authorization To Disclose Release And Use Protected Health workflow has identical requirements; each provider must confirm HIPAA, state-law, and internal policy controls before deployment.
Regional clinic
A regional clinic can use a signNow template to collect patient permission for a clearly defined records disclosure.
- Patient authorization template
- Defined recipient and purpose
- Signed audit trail
The clinic can route the authorization to the patient, preserve the completed document with its audit trail, and restrict access to disclosure staff. The scenario remains subject to the authorization’s required elements, the HIPAA Privacy Rule, any applicable state law, and the organization’s records policy.
Troubleshooting authorization workflows
Resolve access, authentication, plan, and retention questions before releasing protected health information through this authorization.
Business includes legally binding eSignatures, templates, and audit trails at $8 per user monthly with annual billing. Business Premium costs $15 per user monthly annually and adds bulk send. Either plan can support this authorization workflow, subject to your organization’s HIPAA requirements.
signNow states that HIPAA compliance requires a business associate agreement. Confirm that the applicable signNow arrangement includes a BAA before placing protected health information in the workflow, and configure access controls appropriate to your covered-entity or business-associate responsibilities.
A typed, drawn, or click-to-sign mark can be an electronic signature when intent, consent, attribution, and record retention are established. ESIGN and UETA provide the legal framework; the authorization’s healthcare requirements still depend on applicable HIPAA and state law.
If a signer cannot open the authorization, check the email address, signing link, browser session, and requested authentication method. signNow supports mobile apps and SMS-based authentication options; resend only after confirming the recipient and document version.
Business Premium includes bulk send, but this authorization should not be distributed in bulk unless every recipient, disclosure purpose, recipient class, and requested information scope is intentionally identical. Review individualized health-information permissions before using bulk delivery.
HIPAA requires covered entities to retain required documentation for six years from creation or the last effective date under 45 CFR §164.530(j). Preserve the signed authorization and its audit trail in a retrievable, access-controlled record system.
Key performance indicators that demonstrate SignNow's proven track record.
BE READY TO GET MORE
Get this form now!

If you believe that this page should be taken down, please follow our DMCA take-down process.