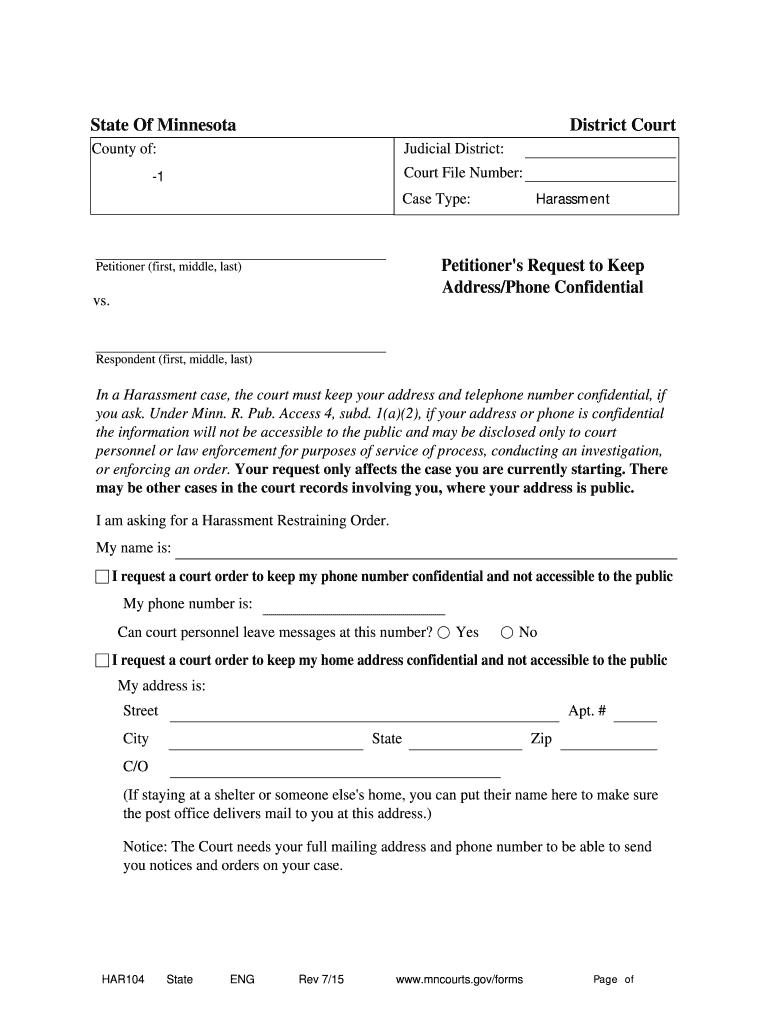
Petitioner's Request To Keep
Use a Petitioner's Request To Keep 2015 template to make your document workflow more streamlined.
What Petitioner's Request To Keep does
Petitioner's Request To Keep is a document used to record a petitioner’s request and supporting decision in a signed business record. In signNow, upload the form, map its fillable fields, identify the requester and signer, and send it electronically. The signer reviews the populated fields, provides consent and a signature, and receives a completed copy. signNow records authentication events, timestamps, document activity, and completion evidence in an audit trail. Under ESIGN and UETA, electronic records can generally support transactions when intent, consent, attribution, and reproducible retention are established.
Business types using this request
Petitioner's Request To Keep can support individual, regulated, and enterprise workflows when the document’s legal scope is confirmed.
Solo legal practitioners can prepare a petitioner’s request, collect a client signature, and preserve the audit trail without coordinating paper exchanges across offices. Healthcare practices can route requests containing protected health information when a HIPAA-compliant workflow and required Business Associate Agreement are in place. Enterprise operations teams can connect request routing to Salesforce, Microsoft 365, or NetSuite while administrators control templates, permissions, and audit access.
These tasks are executed by both individual contributors and centralized administrators depending on organizational policy and required controls.
Complete Petitioner's Request To Keep online
Use this sequence to prepare, route, sign, and preserve the completed request.
Upload form:
Upload the Petitioner's Request To Keep file. Map fields:
Let signNow detect and map fillable fields. Add recipients:
Add the requester and signer details. Send request:
Send the request for electronic signature. Store evidence:
Store the completed form with its audit trail.
 Best ROI. Our customers achieve an average 7x ROI within the first six months.
 Scales with your use cases. From SMBs to mid-market, airSlate SignNow delivers results for businesses of all sizes.
 Intuitive UI and API. Sign and send documents from your apps in minutes.
How the Petitioner's Request To Keep audit trail works
The audit trail preserves signer identity, event timing, document integrity, and an exportable history for Petitioner's Request To Keep.
Authenticate signer:
Capture timestamp:
Hash document:
Seal record:
Log activity:
Export evidence:
Recommended setup for this request
Configure authentication, signature capture, audit evidence, retention, and encryption around the Petitioner's Request To Keep transaction.
| Setting | Recommendation |
|---|---|
| Authentication method | SMS OTP for external signers |
| Signature type | Typed or drawn electronic signature |
| Audit trail | Enable completion certificate and event history |
| Document retention | Three years from filing under IRC §6501(a) |
| Encryption | TLS 1.2/1.3 in transit and AES-256 at rest |
Find and fill out the correct petitioners request to keep
airSlate SignNow helps you fill in and sign documents in minutes, error-free. Choose the correct version of the editable PDF form from the list and get started filling it out.
| Versions | Form popularity | Fillable & printable |
|---|---|---|
| *2015 MN HAR104 [2015-07] 2015 | 4.7 Satisfied (242 Votes) |
Security controls for this request
Transport encryption:
Stored encryption:
SOC 2 Type II:
ISO 27001:
ESIGN and UETA:
HIPAA protection:
Record-keeping practices for this request
Preserve the signed form, completion certificate, and audit evidence according to the transaction’s governing retention rule.
Export the signed record and audit trail
Match retention to the governing authority
Archive records with controlled access
Review state and transaction requirements
Privacy and disclosure pitfalls
Including unnecessary personal information in Petitioner's Request To Keep increases disclosure exposure when the completed document is shared or archived. Skipping the ESIGN consumer disclosure can undermine consent when a consumer-facing transaction requires paper-record access and withdrawal procedures. Sending the request from an unapproved account can weaken access control and make signer attribution harder to demonstrate during review. Exporting the signed form without its audit trail separates the document from evidence of timestamps, authentication, and completed actions.
Troubleshooting Petitioner's Request To Keep
Resolve field mapping, signer authentication, plan, legal-scope, and security questions before treating the completed request as final evidence.
Upload the original Petitioner's Request To Keep again and confirm that each field is mapped to the intended signer. signNow templates can preserve corrected field placement for later sends under the Business plan.
A signed record can still be evidence if intent, consent, attribution, and reproducible retention are documented. Under ESIGN and UETA, confirm the signer consented and preserve the complete signNow audit trail.
Business includes audit trails and templates, while Business Premium adds bulk send. Choose Business Premium when identical Petitioner's Request To Keep copies must reach multiple recipients.
Enable SMS OTP or another available authentication control before sending the request. Stronger authentication supports attribution, but the organization must still retain consent and transaction records.
Do not use an electronic workflow for a will, codicil, testamentary trust, court order, or official court filing. ESIGN expressly excludes those categories from its general electronic-record rule.
signNow encrypts data in transit with TLS 1.2/1.3 and at rest with AES-256. For HIPAA-covered information, a Business Associate Agreement is required under the signNow compliance terms.
Key performance indicators that demonstrate SignNow's proven track record.
BE READY TO GET MORE
Get this form now!

If you believe that this page should be taken down, please follow our DMCA take-down process.