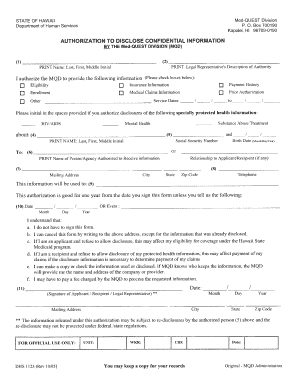
Authorizat Ion T0 Disclose Confjdential Information Med Quest
Use a AUTHORiZAT ION T0 DISCLOSE CONFJDENTIAL INFORMATION Med quest 2005 template to make your document workflow more streamlined.
What this authorization does
The Authorizat Ion T0 Disclose Confjdential Information Med Quest form gives a named person or organization permission to disclose specified confidential information to an identified recipient. The signer should define the information covered, disclosure purpose, recipient, expiration or revocation terms, and any required acknowledgments. In a signNow workflow, upload the form, review or add fillable fields, assign each signer, and send it for completion. The signed PDF and audit trail can then be stored together. Legal sufficiency depends on the information involved and applicable federal and state law.
Who uses the authorization form
Healthcare records
Healthcare practices use it for patient-authorized release of specified medical records, subject to HIPAA and any applicable state privacy law.
Other confidential records
Schools, employers, attorneys, and financial teams use it for controlled disclosure of identified confidential information to named recipients.
Organizations that use this form
The form is most useful when a person or organization must document permission before sharing confidential information with a specified recipient.
A healthcare practice can use the authorization to collect a patient’s permission before releasing specified records, while preserving the signed form and audit trail for its HIPAA-governed workflow. A school or employer can route a narrowly written authorization to the individual, recipient, and reviewing administrator when education or employment records require documented consent. A legal or financial services team can use the form to document a client’s release instructions, verify the recipient, and retain evidence showing the approved disclosure scope.
These tasks are executed by both individual contributors and centralized administrators depending on organizational policy and required controls.
How to complete this authorization
Follow the document-specific workflow from upload through signed-record storage, checking every disclosure field before delivery.
Upload the form: Upload the authorization PDF to signNow. Prepare fields: Review detected fields and add missing signer fields. Send for signature: Assign the authorization to the required signer. Preserve the record: Store the signed form with its audit trail.
 Best ROI. Our customers achieve an average 7x ROI within the first six months.
 Scales with your use cases. From SMBs to mid-market, airSlate SignNow delivers results for businesses of all sizes.
 Intuitive UI and API. Sign and send documents from your apps in minutes.
What the audit trail records
The audit trail documents how this confidentiality authorization moved from preparation through signing and final record retrieval.
Signer authentication:
Timestamp capture:
Document integrity:
Activity logging:
Completion record:
Audit export:
Recommended authorization workflow setup
Use a controlled signing configuration that connects the authorization, signer identity, disclosure scope, and audit evidence.
| Setting | Recommendation |
|---|---|
| Authentication method | Email verification with SMS OTP |
| Signature type | Electronic signature with signer intent |
| Audit trail | Retain the completed audit history |
| Document retention | Apply the underlying record rule |
| Encryption | TLS 1.2 or 1.3 and AES-256 |
Find and fill out the correct authorizat ion t0 disclose confjdential information med quest
airSlate SignNow helps you fill in and sign documents in minutes, error-free. Choose the correct version of the editable PDF form from the list and get started filling it out.
| Versions | Form popularity | Fillable & printable |
|---|---|---|
| HI DHS 1123 2013 | 4.8 Satisfied (3619 Votes) | |
| HI DHS 1123 2006 | 4.7 Satisfied (251 Votes) | |
| HI DHS 1123 2005 | 4.8 Satisfied (224 Votes) |
Security controls for confidential records
Transport encryption:
Stored data:
Security reporting:
Security management:
Healthcare privacy:
Electronic signatures:



Best practices for disclosure records
Accurate scope, recipient details, consent evidence, and controlled retention reduce disputes about this authorization.
Limit the information scope
Identify the authorized recipient
Preserve the signing evidence
Track expiration and revocation
Challenges when completing the authorization
The authorization should identify exactly which confidential information may be disclosed, to whom, for what purpose, and for how long. Missing signer consent language can make the recipient’s authority unclear when a clinic, school, employer, or agency receives the authorization. Unrestricted disclosure wording may expose more medical, educational, employment, or financial information than the person intended to release. A paper copy without reliable delivery and storage records can make it difficult to prove who signed, when, and what version was approved.
Risks of an incomplete authorization
Recipient rejection
Privacy overreach
Consent defect
Unauthorized disclosure
Questions about completing the authorization
These answers address field preparation, electronic signing, privacy controls, plan capabilities, and record handling for this confidentiality authorization.
Upload the original PDF again and check whether fields are embedded, flattened, or image-based. signNow can support templates and fillable workflows, but a flattened scan may require manually placing text, date, and signature fields before sending.
A Business plan includes legally binding eSignatures, templates, audit trails, and mobile apps. Business Premium adds bulk send. Choose the plan based on the number of signers and documents, not on the authorization’s legal validity.
For healthcare disclosures, signNow states that HIPAA compliance requires a BAA. The authorization must still satisfy the applicable HIPAA and state-law requirements, including scope, recipient, purpose, and any required expiration terms.
The authorization may be electronically signed when the transaction satisfies ESIGN and applicable state law. ESIGN requires intent, consent, attribution, and a record that can be retained and reproduced; exceptions include wills, court orders, and certain family-law documents.
Review the recipient email, assigned fields, disclosure scope, and signer order before resending. Keep the original invitation and audit history when possible, because duplicate requests can create uncertainty about which completed version controls.
Export or retrieve the completed PDF and audit trail through authorized account access, then place them in the record system governed by the underlying information category. HIPAA records, for example, have a six-year federal retention rule under 45 CFR §164.530(j).
Key performance indicators that demonstrate SignNow's proven track record.
BE READY TO GET MORE
Get this form now!

If you believe that this page should be taken down, please follow our DMCA take-down process.