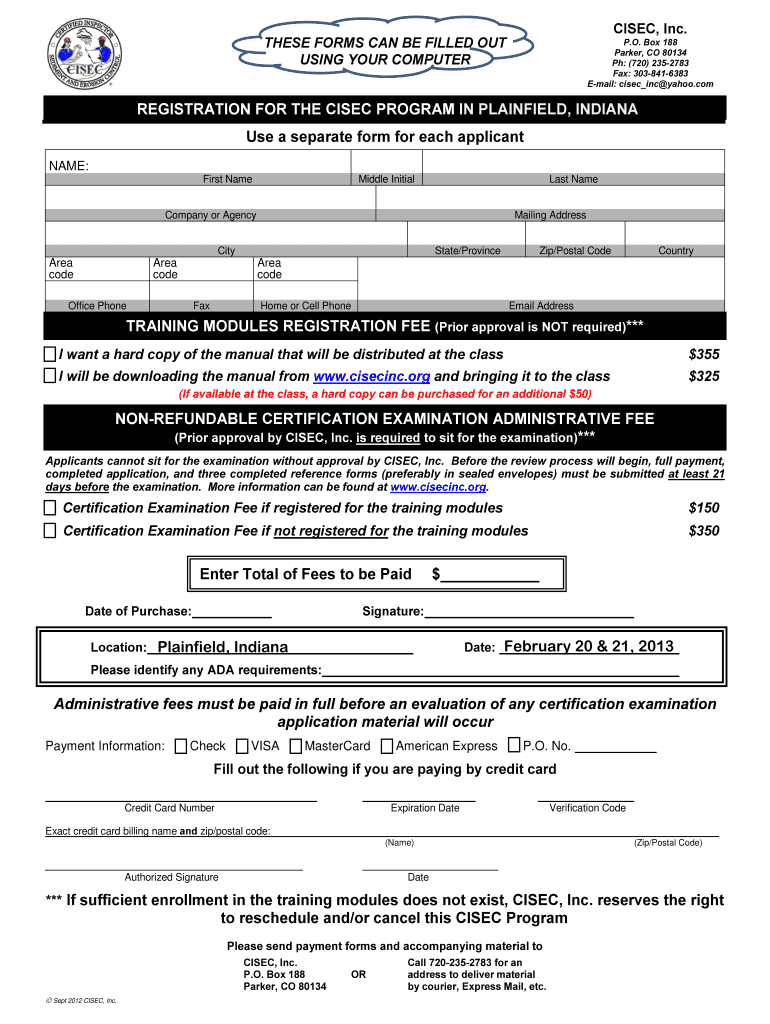
Cisec Registration And Application Checklist Inafsm
Use a CISEC Registration And Application Checklist INAFSM 2012 template to make your document workflow more streamlined.
What this checklist does
The Cisec Registration And Application Checklist Inafsm is a structured document for organizing registration and application information before submission or approval. Because the name does not identify a federal agency, statute, filing deadline, or issuing authority, confirm the checklist’s source and instructions before relying on it. In signNow, upload the document, inspect detected fields, assign each response and signature to the responsible participant, send the workflow, and retain the completed PDF with its audit trail. Apply any governing state or industry rule separately.
Key features for completing this checklist
signNow organizes the Cisec Registration And Application Checklist Inafsm into a controlled completion, signing, evidence, and storage workflow.
Field placement
Upload the Cisec Registration And Application Checklist Inafsm as a PDF, then place signature, date, initials, and required-response fields where the document requires completion. This reduces overlooked blanks while preserving the checklist’s original structure for review.
Signer routing
Send the checklist to the correct participants in a defined order. Role-based routing helps each person complete only the fields assigned to them before the record moves to the next signer or reviewer.
Audit trail
Capture signer actions, timestamps, authentication events, and document history alongside the completed checklist. The resulting audit evidence helps explain how the record was executed if its validity is later questioned.
Mobile access
Use signNow from a desktop browser or mobile app to complete the checklist without retyping its contents. Mobile access supports field completion when the responsible participant is away from the office.
Secure storage
Save the finished checklist and its completion evidence in a controlled location. A consistent archive makes it easier to retrieve the exact signed version during an internal review or legal inquiry.
Workflow integration
Connect the checklist workflow with approved business systems when records must move into a customer, finance, or document repository. Integration reduces duplicate entry and keeps the completed record associated with its underlying matter.
Who uses this registration checklist
Administrative teams
Administrative teams can use the Cisec Registration And Application Checklist Inafsm to collect registration details, internal approvals, and signature evidence before sending an application onward. Assigning fields to named participants helps separate preparer, reviewer, and signer responsibilities while preserving one completed record for the matter.
Review teams
Legal, compliance, or operations staff can review the completed checklist before submission and compare responses against the source instructions. They can require corrections, preserve the audit trail, and restrict access when the document contains confidential business or personal information.
Recommended workflow setup
Configure the checklist around verified signer identity, clear field ownership, audit evidence, and the retention rule governing the underlying application.
| Setting | Recommendation |
|---|---|
| Authentication method | Email verification with SMS OTP |
| Signature type | Typed or drawn electronic signature |
| Audit trail | Export with the completed PDF |
| Document retention | Apply the underlying matter’s rule |
| Encryption | TLS 1.2/1.3 and AES-256 |
How to complete this checklist
Use this signNow workflow to prepare the Cisec Registration And Application Checklist Inafsm and preserve evidence of its completion.
Upload document:
Upload the checklist PDF. Check fields:
Review detected fields and add missing response, date, or signature fields. Assign roles:
Assign each field to its responsible participant. Send workflow:
Send the checklist for completion and signature. Verify record:
Review the completed PDF and audit trail.
 Best ROI. Our customers achieve an average 7x ROI within the first six months.
 Scales with your use cases. From SMBs to mid-market, airSlate SignNow delivers results for businesses of all sizes.
 Intuitive UI and API. Sign and send documents from your apps in minutes.
How the checklist audit trail works
The audit trail records execution evidence separately from the checklist’s substantive responses, creating a traceable history for later review.
Authenticate signer:
Capture timestamps:
Hash document:
Seal record:
Preserve history:
Export evidence:
Platform requirements for this checklist
Complete the Cisec Registration And Application Checklist Inafsm through signNow using Chrome, Firefox, Safari, or Edge on Windows or macOS. signNow also provides mobile apps for iOS and Android, allowing assigned participants to review and complete fields on supported phones and tablets.
Browsers Chrome, Firefox, Safari, and Edge Desktop systems Windows and macOS desktops Mobile access iOS and Android mobile apps
Organizations should use managed Windows, macOS, iOS, or Android devices when the checklist contains confidential registration or application information. Confirm TLS access, identity controls, SSO provisioning, API requirements, and retention configuration with the responsible administrator before deployment.
Find and fill out the correct cisec registration and application checklist inafsm
airSlate SignNow helps you fill in and sign documents in minutes, error-free. Choose the correct version of the editable PDF form from the list and get started filling it out.
| Versions | Form popularity | Fillable & printable |
|---|---|---|
| *2012 IN Registration for the CISEC Program in Plainfield [2012-09] 2012 | 4.8 Satisfied (6829 Votes) |
Security controls for this checklist
Data in transit:
Stored data:
Security certification:
Information security:
Electronic signatures:
Health information:
Record-keeping practices for this checklist
Preserve the completed Cisec Registration And Application Checklist Inafsm with evidence showing who signed, when, and how the record was protected.
Apply the governing retention rule
Export the audit trail promptly
Archive records in a controlled repository
Retain HIPAA records six years
Retention periods for related records
The checklist itself has no identified statutory retention period. Match the completed record to the underlying registration, tax, employment, health, or safety matter before applying one of these documented schedules.
Three years for tax records
Six years for major understatement
Six years for HIPAA records
Later of three or one years
Five years for injury records
Privacy pitfalls for this checklist
Redact unnecessary personal identifiers before sending the Cisec Registration And Application Checklist Inafsm to participants who do not need full visibility. Use an electronic-record disclosure when consumer-facing completion requires consent, access to the electronic format, and a way to withdraw consent under 15 U.S.C. §7001(c). Limit template and completed-record access to assigned administrators, preparers, reviewers, and signers rather than sharing an unrestricted document link. Check that every required response and signature belongs to the correct participant before exporting the final checklist and audit trail.
Risks of incomplete execution
Submission delay
Record challenge
Attribution dispute
ESIGN exception



Troubleshooting this checklist workflow
Resolve these named checklist, plan, compliance, and archival issues before treating the Cisec Registration And Application Checklist Inafsm as complete.
Upload the Cisec Registration And Application Checklist Inafsm as a PDF, then review every detected field manually. Auto-detection can identify likely fillable areas, but it cannot determine which participant or authority owns an ambiguous checklist response. Add, remove, or reassign fields before sending.
Business includes legally binding eSignatures, templates, mobile apps, and audit trails at $8 per user per month with annual billing. It includes 100 signature invites per user per year; additional invite charges may apply, so review volume before choosing the plan.
Business Premium adds bulk send at $15 per user per month with annual billing. Use it when the same Cisec Registration And Application Checklist Inafsm must be distributed to many separate recipients; otherwise, Business may provide the listed core signing and audit features.
For a checklist containing protected health information, signNow states HIPAA compliance requires a business associate agreement. Confirm the BAA and your organization’s safeguards before sending PHI, and apply the six-year documentation rule in 45 CFR §164.530(j).
ESIGN and applicable UETA rules generally recognize electronic signatures when intent, consent, attribution, and record retention are established. Consumer-facing records may require the disclosure and access procedures in 15 U.S.C. §7001(c); confirm the underlying application’s exclusions first.
Export the completed PDF and audit trail together, then store them under the retention schedule for the underlying matter. signNow provides document history and audit-trail evidence, but the responsible organization must set access, deletion, and legal-hold controls.
Key performance indicators that demonstrate SignNow's proven track record.
BE READY TO GET MORE
Get this form now!

If you believe that this page should be taken down, please follow our DMCA take-down process.