Corrective Action Root Cause Analysis
Use a Corrective Action Root Cause Analysis 2009 template to make your document workflow more streamlined.
What corrective action root cause analysis does
Corrective Action Root Cause Analysis documents why a problem occurred, what evidence supports that conclusion, and which corrective actions must be completed. A reviewer records the issue, contributing factors, root cause, assigned owner, due date, corrective measure, verification method, and approval. The signed record helps HR, quality, safety, and compliance teams show how the decision was made and acknowledged. signNow lets a sender upload the analysis, place fields, route it to designated reviewers, collect signatures, and retain the completed document with its audit trail.
Who benefits from corrective action analysis
The form is useful wherever teams must connect an incident to a documented cause, assigned remedy, verification evidence, and accountable acknowledgment.
Small manufacturers use the analysis to document production deviations, identify process causes, assign corrective owners, and obtain supervisor acknowledgment before closing quality records. Healthcare operations teams use it for documented incidents, linking contributing factors, corrective measures, verification evidence, and authorized signatures while applying HIPAA controls when protected health information is involved. Enterprise HR and compliance departments use controlled templates to standardize employee-related investigations, route approvals by role, and preserve signed analyses for internal reviews, audits, or disputes.
These tasks are executed by both individual contributors and centralized administrators depending on organizational policy and required controls.
Features for corrective action analysis
signNow connects the analysis form’s fields, approvals, signatures, and completion evidence into one documented workflow for HR and operational teams.
Fillable fields
Upload a completed corrective action template and place signature, date, acknowledgment, and approval fields without rebuilding the document manually.
Role-based routing
Route the analysis to the employee, manager, investigator, or compliance reviewer in a defined signing order for accountable approval.
Audit trail
Capture signing timestamps, signer actions, and access details so the completed analysis has a traceable execution history.
Mobile signing
Collect signatures from desktop or mobile devices when corrective action discussions involve remote employees or field personnel.
Reusable templates
Reuse a controlled corrective action template while preserving consistent field placement and required acknowledgment language across cases.
Secure records
Store the signed document and completion evidence together for later HR, quality, safety, or compliance review.
How the corrective action analysis works
The form moves from documented facts to root-cause findings, assigned remediation, verification, and signed acknowledgment.
Describe issue: Record the event and supporting facts Find cause: Analyze contributing conditions and identify the root cause Set action: Assign an owner, remedy, due date, and verification method Collect signatures: Route the completed analysis for acknowledgment and approval
 Best ROI. Our customers achieve an average 7x ROI within the first six months.
 Scales with your use cases. From SMBs to mid-market, airSlate SignNow delivers results for businesses of all sizes.
 Intuitive UI and API. Sign and send documents from your apps in minutes.
How signNow records the audit trail
The audit trail records the technical events surrounding this corrective action analysis, separate from the form’s substantive root-cause findings.
Authenticate signer:
Capture timestamp:
Record document hash:
Seal completion:
Log actions:
Export evidence:
Recommended corrective action workflow setup
Configure the document around accountable reviewers, traceable approvals, and secure storage for each completed corrective action analysis.
| Setting | Recommendation |
|---|---|
| Authentication method | Email verification with SMS OTP |
| Signature type | Typed or drawn electronic signature |
| Audit trail | Capture timestamps, IP addresses, and actions |
| Document retention | Follow the organization’s approved retention schedule |
| Encryption | TLS 1.2/1.3 and AES-256 protection |
Find and fill out the correct corrective action root cause analysis
airSlate SignNow helps you fill in and sign documents in minutes, error-free. Choose the correct version of the editable PDF form from the list and get started filling it out.
| Versions | Form popularity | Fillable & printable |
|---|---|---|
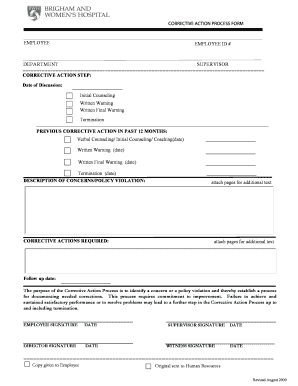
| *2009 BWH Corrective Action Process Form [2009-08] 2009 | 4.8 Satisfied (2289 Votes) |
Platform requirements for corrective action analysis
Complete Corrective Action Root Cause Analysis in Chrome, Firefox, Safari, or Edge on Windows and macOS, with signNow apps available for iOS and Android. TLS 1.2 or newer protects connections.
Browser support Chrome, Firefox, Safari, and Edge on Windows or macOS Mobile access iOS and Android devices with signNow mobile apps Connection security TLS 1.2 or newer for secure connections
Organizations can use managed Windows, macOS, iOS, or Android devices with signNow access controls and audit trails. Enterprise deployments may connect API workflows, configure SSO provisioning, and apply retention or certificate policies required by internal governance, HIPAA, or other applicable standards.



Privacy pitfalls in corrective action records
Unnecessary employee names, medical details, or customer information can expose personal data beyond the corrective action team. Missing consent or acknowledgment fields can weaken evidence that the affected employee reviewed the proposed corrective action. Sending the analysis to the wrong recipient can disclose root-cause findings, disciplinary details, or protected operational information. Uncontrolled copies outside the approved repository can separate the signed analysis from its audit trail and retention controls.
Best practices for corrective action records
A defensible corrective action record connects the completed analysis, signatures, audit trail, access controls, and retention decision in one controlled workflow.
Export the audit trail with every completed analysis
Apply a documented retention rule
Limit access to authorized reviewers
Archive the signed record securely
Security controls for corrective action records
Data in transit:
Stored documents:
Service controls:
Security management:
Protected health data:
Electronic signatures:
Key performance indicators that demonstrate SignNow's proven track record.
Corrective action analysis troubleshooting
Resolve field, routing, authentication, retention, and compliance questions before sending a corrective action analysis for signature.
Upload the original PDF again and confirm the document opens correctly before placing signNow fields. If auto-detection does not identify fields, add signature, date, text, and acknowledgment fields manually, then preview the recipient experience before sending.
A signNow Business plan includes templates, audit trails, and legally binding eSignatures at $8 per user per month when billed annually. Business Premium adds bulk send at $15 per user per month annually; choose it only when repeated distribution is required.
ESIGN and UETA generally recognize electronic signatures when intent, consent, attribution, and record retention requirements are satisfied. For consumer-facing records, review the ESIGN consumer disclosure requirements in 15 U.S.C. §7001(c) before sending the analysis electronically.
Use signNow’s configured authentication options, such as email verification or SMS OTP, and confirm the recipient’s address before resending. Do not forward a private signing link when the analysis contains employee, patient, or incident information.
Export the completed PDF and audit trail after every final signature, then place both in the approved repository. The audit trail supplies execution evidence, while the form itself supplies the documented issue, root cause, corrective action, and verification details.
If protected health information appears in the analysis, confirm that the organization has the required signNow Business Associate Agreement and applies HIPAA safeguards. HIPAA’s six-year rule in 45 CFR §164.530(j) concerns specified records and does not replace a broader organizational schedule.
BE READY TO GET MORE
Get this form now!

If you believe that this page should be taken down, please follow our DMCA take-down process.