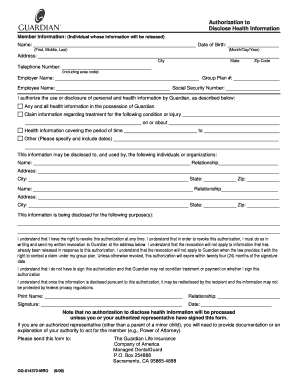
Authorization To Disclose Health Information Guardian Life Insurance
Use a Authorization To Disclose Health Information Guardian Life Insurance 2009 template to make your document workflow more streamlined.
What this Guardian authorization does
The Authorization To Disclose Health Information Guardian Life Insurance form gives a patient or member a documented way to permit specified health information to be shared with identified recipients for a stated purpose. Its practical core is narrow: identify the person, describe the information, name the recipient, state the purpose and expiration, and capture consent. Guardian Life Insurance or its authorized administrators should verify the completed form against applicable HIPAA requirements and state law before releasing protected health information. signNow can route signatures and preserve an auditable completed copy.
Features for Guardian Life Insurance authorizations
signNow combines field preparation, signer routing, authentication records, and Audit Trail evidence for this health-information authorization workflow.
Defined scope
Keep the authorization’s patient or member information, recipient, purpose, scope, and expiration together in one completed record for review before disclosure.
Assigned fields
Assign signature and date fields to the appropriate signer, reducing ambiguity about who approved the Guardian Life Insurance disclosure.
Audit trail
Capture delivery, viewing, signing, and completion events in a signNow Audit Trail connected to the final authorization.
Signer controls
Use signer authentication options appropriate to the sensitivity of the health information and the organization’s approved workflow.
Secure record
Retain a reproducible PDF and associated signing evidence so authorized reviewers can inspect the disclosure history later.
Connected workflow
Route completed authorizations into approved storage or connected systems without relying on scattered email attachments or personal downloads.
Complete the Guardian authorization online
Use signNow to prepare the Guardian Life Insurance authorization, route it to the required signer, and preserve the completed record.
Upload form:
Upload the Guardian authorization PDF to signNow. Check fields:
Review detected fields and add missing recipient, purpose, and signature fields. Assign signers:
Assign each field to the correct signer or representative. Send securely:
Send the authorization and monitor its signing status. Store evidence:
Download the signed form and Audit Trail for records.
How this Guardian authorization works
The workflow moves from document preparation to signer routing and documented storage without changing the authorization’s stated disclosure scope.
Upload: Upload the Guardian Life Insurance authorization and review its fields. Assign: Add recipients and assign each disclosure authorization field. Send: Send the prepared form through signNow for signature. Archive: Store the signed authorization with its Audit Trail.
Processing the Guardian authorization
Processing time depends on field review and signer response; no fixed Guardian Life Insurance turnaround figure is provided here.
Prepare the authorization
Deliver to signers
Collect required signatures
Complete and archive
 Best ROI. Our customers achieve an average 7x ROI within the first six months.
 Scales with your use cases. From SMBs to mid-market, airSlate SignNow delivers results for businesses of all sizes.
 Intuitive UI and API. Sign and send documents from your apps in minutes.
What the signNow Audit Trail records
The Audit Trail documents signer activity and record integrity for the Guardian Life Insurance authorization, separate from preparing and sending the form.
Authenticate signer:
Capture timestamps:
Hash document:
Seal history:
Record activity:
Export evidence:
Privacy pitfalls to check
Listing a recipient or disclosure purpose too broadly can make the Guardian authorization difficult to review and may exceed the intended consent scope. Sending protected health information through an unapproved email attachment can expose personal data outside the organization’s access controls. Omitting the signer’s identity, signature date, expiration, or revocation details can weaken the record supporting a later disclosure. Allowing unrestricted access to completed authorizations can expose health information to personnel without a Guardian Life Insurance business need.
Find and fill out the correct authorization to disclose health information guardian life insurance
airSlate SignNow helps you fill in and sign documents in minutes, error-free. Choose the correct version of the editable PDF form from the list and get started filling it out.
| Versions | Form popularity | Fillable & printable |
|---|---|---|
| Guardian GG-014372-MRO 2009 | 4.8 Satisfied (3604 Votes) | |
| Guardian GG-014372-MRO 2003 | 4.8 Satisfied (151 Votes) |
Recommended authorization workflow setup
Use a controlled signNow configuration that matches the sensitivity of Guardian Life Insurance health-information authorizations and preserves reviewable evidence.
| Setting | Recommendation |
|---|---|
| Authentication method | Email link with SMS OTP |
| Signature type | Electronic signature with intent |
| Audit trail and retention | Export Audit Trail; retain six years under HIPAA |
| Encryption | TLS 1.2/1.3 and AES-256 |
| User provisioning | Role-based access with approved administrators |
Security for health-information authorizations
HIPAA protection:
Transport encryption:
Stored encryption:
SOC 2 certification:
ISO certification:
Signature compliance:



Retention schedule for authorization records
Retention depends on the record’s role, applicable HIPAA obligations, Guardian Life Insurance policy, and state requirements; the six-year federal HIPAA period is the stated baseline for required documentation.
Six years for HIPAA documentation
Longer period where required
Signed authorization evidence
Authorization revocation history
Post-retention secure disposal
Retention and record-keeping practices
Keep each Guardian Life Insurance authorization complete, traceable, and protected from unnecessary disclosure.
Apply the six-year HIPAA retention rule
Export the audit trail with each authorization
Archive signed forms in controlled storage
Verify every disclosure field before release
Legal standing of the authorization
A signed electronic authorization can support a U.S. disclosure workflow when the signer demonstrates intent, consents to electronic records, can be identified, and the record remains reproducible under ESIGN, 15 U.S.C. ch. 96, and applicable UETA law. HIPAA requirements still govern protected health information. Wills, court orders, family-law decrees, and certain insurance-cancellation notices are excluded from ESIGN’s electronic-record framework.

Key performance indicators that demonstrate SignNow's proven track record.
Guardian authorization troubleshooting
Resolve field, signing, security, plan, and retention questions before disclosing health information through a completed Guardian Life Insurance authorization.
Upload the Guardian authorization PDF into signNow, then inspect every detected field. Auto-detection does not determine whether the disclosure scope, recipient, purpose, expiration, or signer assignments satisfy Guardian Life Insurance policy or HIPAA requirements.
Use signNow’s assigned fields to identify the person signing the authorization and the representative receiving it. If the document concerns protected health information, confirm the signer’s identity and use the organization’s approved authentication policy before sending.
A signNow Business plan includes legally binding eSignatures and Audit Trails at $8/user/month with annual billing. A HIPAA workflow requires signNow’s HIPAA terms and a BAA where applicable; pricing does not replace the organization’s HIPAA obligations.
signNow encrypts data in transit with TLS 1.2/1.3 and at rest with AES-256. Configure access controls, use an applicable BAA, and verify that the final authorization and Audit Trail enter approved storage rather than personal downloads.
The signNow Business Premium plan costs $15/user/month with annual billing and includes bulk send. Bulk send is useful only when each Guardian authorization is independently reviewed for recipient, purpose, scope, and signer accuracy before release.
Download the completed PDF and signNow Audit Trail after signing, then preserve both under the applicable policy. HIPAA 45 CFR §164.530(j) establishes a six-year documentation period; state law, legal holds, or Guardian policy may require longer retention.
BE READY TO GET MORE
Get this form now!

If you believe that this page should be taken down, please follow our DMCA take-down process.