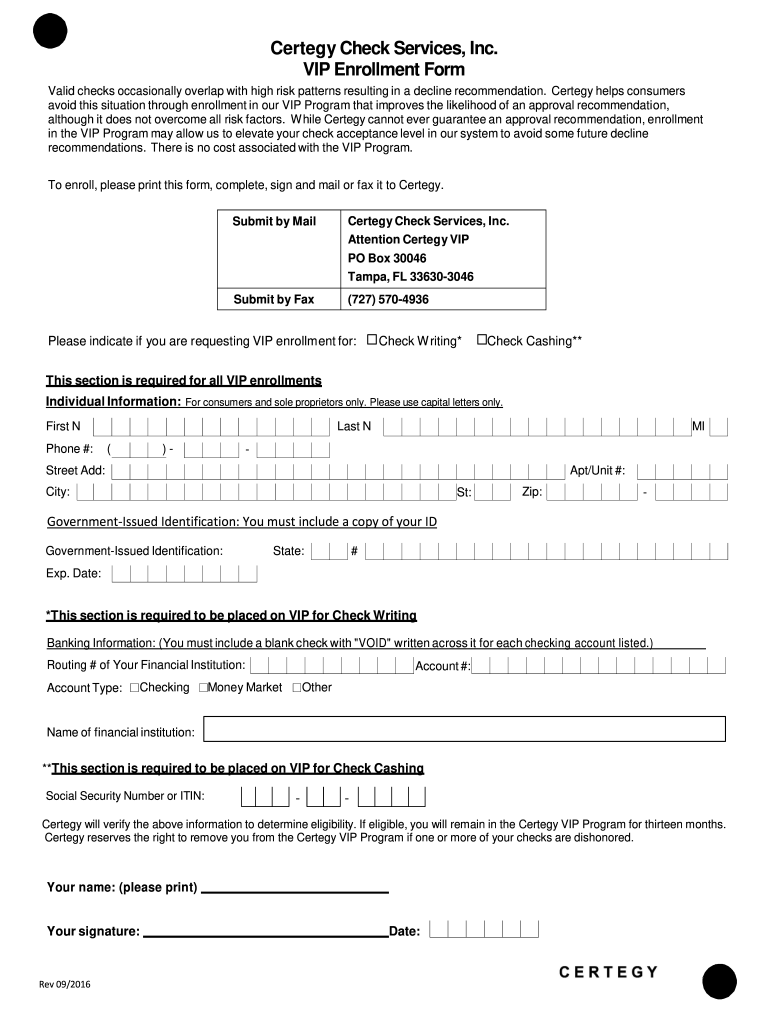
How To Get Around Certegy
Use a How To Get Around Certegy 2016 template to make your document workflow more streamlined.
What this Certegy guidance covers
How To Get Around Certegy is not an official Certegy form or a lawful method for bypassing check-screening decisions. It refers to guidance for responding to a declined or held transaction through legitimate options, such as confirming account information, contacting the merchant, using an accepted payment method, or requesting Certegy review. A signNow workflow can document communications, consent, approvals, and alternative-payment agreements. It cannot change Certegy’s decision, remove a consumer report, or authorize a transaction that the merchant has not approved.
Who benefits from compliant Certegy workflows
Legitimate businesses use this workflow to document payment decisions, offer lawful alternatives, and maintain clear records rather than evade screening.
Independent retail operators use the document to record legitimate payment-screening decisions and preserve customer consent without attempting to bypass Certegy controls. Property-management companies document approved payment alternatives, signer authorization, and tenant communications when a Certegy check decision requires follow-up. Multi-location service businesses standardize escalation records, access permissions, and signed acknowledgments so finance teams can review Certegy-related transactions consistently.
These tasks are executed by both individual contributors and centralized administrators depending on organizational policy and required controls.
How the documented workflow works
The workflow records an approved response to a Certegy decision without attempting to alter screening results or bypass merchant controls.
Upload the record: Upload the Certegy-related record to signNow and review the detected fillable fields. Add required fields: Add the approved payment alternative, consent language, and required signer fields. Send for signing: Send the record to authorized signers through email or a controlled signing link. Store the record: Store the completed document with its audit trail and access restrictions.
Quick steps for a lawful response
Use these steps to document an approved payment alternative rather than circumventing Certegy’s screening decision.
Upload:
Upload the Certegy-related document. Review:
Review detected fields and data. Send:
Send only to approved signers. Store:
Save the signed record and audit trail.
 Best ROI. Our customers achieve an average 7x ROI within the first six months.
 Scales with your use cases. From SMBs to mid-market, airSlate SignNow delivers results for businesses of all sizes.
 Intuitive UI and API. Sign and send documents from your apps in minutes.
Recommended Certegy record setup
Use a controlled configuration that records the approved response, signer identity, consent, and retention decision without storing unnecessary payment information.
| Setting | Recommendation |
|---|---|
| Authentication method | Email link with SMS OTP |
| Signature type | Typed or drawn electronic signature |
| Audit trail | Enable completion certificate and history |
| Document retention | Follow the applicable record rule |
| Encryption | AES-256 at rest and TLS in transit |
Key features for Certegy records
signNow helps document an approved response to a Certegy decision through field detection, controlled signing, audit history, and secure record handling.
Field detection
Upload a Certegy-related document, then review automatically detected fields before adding approved payment terms and signer information.
Controlled sending
Send an authorization or alternative-payment record to specified recipients without circulating sensitive details through ordinary email attachments.
Audit trail
Capture signer actions, timestamps, and completion history so the record shows how the approved response was executed.
Reusable templates
Use templates for recurring merchant-approved alternatives while keeping required consent and disclosure language consistent across transactions.
Protected records
Apply role-based access and encrypted storage to reduce unnecessary exposure of payment and identity information.
Business integrations
Connect completed records with business systems such as Salesforce, NetSuite, Google Drive, Box, or Procore when appropriate.
Find and fill out the correct how to get around certegy
airSlate SignNow helps you fill in and sign documents in minutes, error-free. Choose the correct version of the editable PDF form from the list and get started filling it out.
| Versions | Form popularity | Fillable & printable |
|---|---|---|
| Certegy Check Services VIP Enrollment Form 2016 | 4.8 Satisfied (12228 Votes) | |
| Certegy Check Services VIP Enrollment Form 2013 | 4.8 Satisfied (2382 Votes) |
Security for Certegy records
AES-256 and TLS:
ESIGN and UETA:
SOC 2 Type II:
ISO 27001:
HIPAA with BAA:
GDPR compliant:
Mobile options for Certegy records
The signNow mobile apps support documenting Certegy-related approvals and payment alternatives from iOS and Android devices. Upload the relevant record, capture supporting pages with the device camera, and use offline signing when connectivity is unavailable.
iOS 15 or later iOS app Android 9 or later Android app Camera capture and offline signing Offline capture
Review device management before handling payment or identity information. Organizations can require managed iOS or Android devices, stronger signer authentication, and controlled access to completed records. API, SSO, and certificate configuration should follow the organization’s security policy and the sensitivity of the Certegy-related documentation.
Record-keeping practices for Certegy workflows
Clear retention, access, and export practices help distinguish an approved payment arrangement from an attempt to bypass screening controls.
Apply the correct retention period
Export the audit trail
Minimize sensitive payment information
Document lawful alternatives clearly
Legal standing of documented alternatives
A signNow record may support evidence of intent, consent, attribution, and transaction history under the ESIGN Act and applicable UETA rules. It cannot validate an unauthorized payment workaround, change Certegy information, or replace legally excluded records such as wills, codicils, and certain court filings.

Troubleshooting Certegy-related records
Use signNow to document an approved response to a Certegy decision, not to bypass screening, alter a report, or guarantee payment acceptance.
A Certegy decline is not an error that signNow can reverse. Confirm the transaction details with the merchant, ask which payment methods are accepted, and use signNow only to document an approved alternative or acknowledgment. The merchant and Certegy control the decision process.
Do not enter a full bank account number into an unnecessary free-text field. Ask the merchant which information is required, restrict access through signNow permissions, and retain only the minimum data needed for the documented payment arrangement. Apply the organization’s privacy policy.
A signed record can show intent, consent, signer attribution, and transaction history, but it does not guarantee payment approval. ESIGN and UETA support electronic records when their requirements are met; they do not override Certegy or merchant underwriting decisions.
For consumer-facing electronic records, review the ESIGN Act’s consumer-disclosure requirements under 15 U.S.C. §7001(c), including access to electronic records and the right to paper records. Capture consent before requesting a signature and provide a reproducible completed copy.
Business plans include audit trails and templates; Business Premium adds bulk send and kiosk mode. If an account reaches its plan’s annual signature-invite allowance, check current plan terms before sending additional Certegy-related records. Pricing and limits must be confirmed with signNow.
If a Certegy-related record includes protected health information, use a HIPAA-compliant configuration with a business associate agreement. HIPAA’s six-year documentation rule appears at 45 CFR §164.530(j), while other records may follow different requirements.
Key performance indicators that demonstrate SignNow's proven track record.
BE READY TO GET MORE
Get this form now!

If you believe that this page should be taken down, please follow our DMCA take-down process.