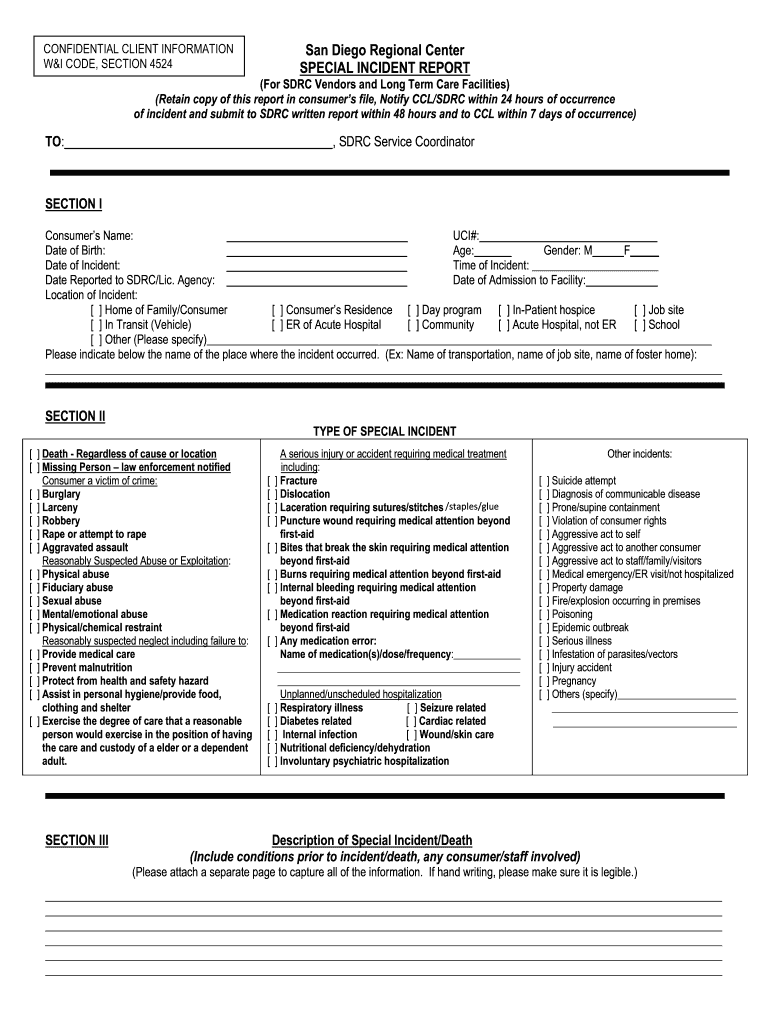
San Diego Regional Center Special Incident Report
Use a San Diego Regional Center Special Incident Report 2016 template to make your document workflow more streamlined.
What the incident report records
The San Diego Regional Center Special Incident Report records a significant event involving a regional-center consumer so responsible personnel can document facts, actions, notifications, and follow-up. It is completed from the incident information available to the reporting organization, reviewed for accuracy, and signed by designated participants. With signNow, an administrator can upload the report, place or detect fillable fields, assign recipients, send the document, and preserve the completed version with its audit trail. Reporting deadlines and required recipients depend on the applicable San Diego Regional Center policy and California law, so the organization must confirm those requirements before submission.
Who uses this incident report
Regional-center providers
Direct-care providers and supervisors use the San Diego Regional Center Special Incident Report to document an event, identify involved consumers, record immediate safeguards, and route the completed report for review. Access should be limited to personnel with a defined reporting or oversight responsibility.
Compliance teams
Compliance and quality teams use the report to verify required facts, approvals, notifications, and follow-up actions. They can send a controlled signNow template, review the audit trail, and store the final report with related records without granting every employee editing access.
Organizations that use the report
The report is most useful where direct-care staff, supervisors, and compliance personnel share responsibility for documenting and reviewing a sensitive incident.
A small supported-living provider can use one approved template to collect incident details, supervisor review, and signatures without circulating editable attachments by email. A regional-center service organization can give compliance staff controlled access to completed reports while delegated coordinators send individual records to designated recipients. A larger healthcare network can connect signNow workflows with approved storage and operational systems, preserving audit trails and limiting sensitive report access by role.
These tasks are executed by both individual contributors and centralized administrators depending on organizational policy and required controls.
Features for this incident report
signNow provides a controlled way to prepare, route, authenticate, sign, and preserve the San Diego Regional Center Special Incident Report.
Field preparation
Upload the San Diego Regional Center Special Incident Report, then place or detect fields for incident facts, dates, review notes, and signatures without rebuilding the document.
Role-based routing
Assign the report to designated reviewers and signers in sequence, helping the organization document who examined and approved the completed incident record.
Signer verification
Use SMS authentication or another configured verification method when stronger signer attribution is required for sensitive regional-center records.
Audit trail
Preserve timestamps, recipient actions, and completion history in a signNow audit trail associated with the signed report.
Controlled storage
Store the signed report and audit evidence in an approved repository with access limited to authorized care, quality, and compliance personnel.
Reusable template
Reuse an approved report template while keeping incident-specific facts entered for each event and preventing unauthorized design changes.
How the report workflow works
The signNow workflow keeps the San Diego Regional Center Special Incident Report moving from preparation through controlled review and signed storage.
Upload report: Upload the approved report file to signNow. Prepare fields: Auto-detect fields or add text, date, and signature fields. Assign recipients: Assign the responsible reviewer and signer. Complete record: Send, complete, and store the report with its audit trail.
 Best ROI. Our customers achieve an average 7x ROI within the first six months.
 Scales with your use cases. From SMBs to mid-market, airSlate SignNow delivers results for businesses of all sizes.
 Intuitive UI and API. Sign and send documents from your apps in minutes.
Steps to complete the report
Use this signNow sequence to prepare the San Diego Regional Center Special Incident Report without changing its incident facts or approval responsibilities.
Upload file:
Upload the approved report PDF. Add fields:
Add or detect required fields. Set recipients:
Enter authorized recipients and roles. Send report:
Send the report for review and signature. Store evidence:
Download the signed report and audit trail.
What the audit trail captures
A signNow audit trail documents the technical history behind a completed San Diego Regional Center Special Incident Report, rather than replacing the report’s factual narrative.
Authenticate signer:
Capture timestamps:
Hash document:
Seal record:
Log activity:
Export evidence:
Find and fill out the correct san diego regional center special incident report
airSlate SignNow helps you fill in and sign documents in minutes, error-free. Choose the correct version of the editable PDF form from the list and get started filling it out.
| Versions | Form popularity | Fillable & printable |
|---|---|---|
| Special Incident Report - San Diego Regional Center 2016 | 4.8 Satisfied (9392 Votes) |
Platform requirements for the incident report
Complete and sign the San Diego Regional Center Special Incident Report through current Chrome, Firefox, Safari, or Edge browsers on Windows or macOS. signNow also provides mobile apps for iOS and Android, with encrypted connections using TLS 1.2 or TLS 1.3.
Browsers Chrome, Firefox, Safari, and Edge Desktop systems Windows and macOS computers Mobile apps iOS and Android mobile apps
Use an organization-managed device when the report contains sensitive information. Confirm browser updates, screen-lock controls, and authorized account access before uploading the report. Mobile signing can support field staff, while administrators should preserve the completed record and audit trail in the approved repository.
Security for sensitive report data
Digital certificates:
X.509 certificates:
Two-factor authentication:
SMS OTP:
ID verification:
Audit trail:
Privacy pitfalls in incident reporting
Including unnecessary medical details can expose protected information to recipients who only need the incident report’s required facts. Leaving the responsible reviewer or signer undefined weakens attribution and makes follow-up responsibility harder to establish. Sending a report through an unrestricted link can disclose consumer information beyond the authorized provider, supervisor, or compliance team. Failing to preserve the signed report and audit trail can make it difficult to demonstrate review, consent, timing, and document integrity.
Record-keeping practices for reports
Accurate retention and controlled access help preserve the San Diego Regional Center Special Incident Report as a reliable compliance record.
Confirm retention before deletion
Export the audit trail
Restrict access to recipients
Archive the final record



Risks of incomplete reporting
Incomplete narrative
Weak attribution
Privacy exposure
Disputed completion
San Diego Regional Center report troubleshooting
Resolve upload, privacy, authentication, and record-handling questions before sending a San Diego Regional Center Special Incident Report for signature.
How do I fix an unreadable uploaded report?
Replace the source file with a clear PDF or DOCX, then upload it again in signNow. The Business plan supports document uploads, templates, fields, legally binding eSignatures, and audit trails. Confirm that the replacement preserves every incident detail before sending it for signature.
What if the report contains protected health information?
Use signNow’s HIPAA-compliant configuration only with a required business associate agreement. Limit access through role controls, use signer authentication, and retain the completed report and audit trail according to your organization’s California reporting policy and 45 CFR 164.530(j).
Why did a signer fail the SMS authentication step?
Check the signer’s phone number, resend the invitation, and use a fresh SMS code. Business Premium includes advanced workflow options, while Enterprise adds advanced signer authentication. Authentication records should remain associated with the completed incident report and its audit trail.
Key performance indicators that demonstrate SignNow's proven track record.
BE READY TO GET MORE
Get this form now!

If you believe that this page should be taken down, please follow our DMCA take-down process.