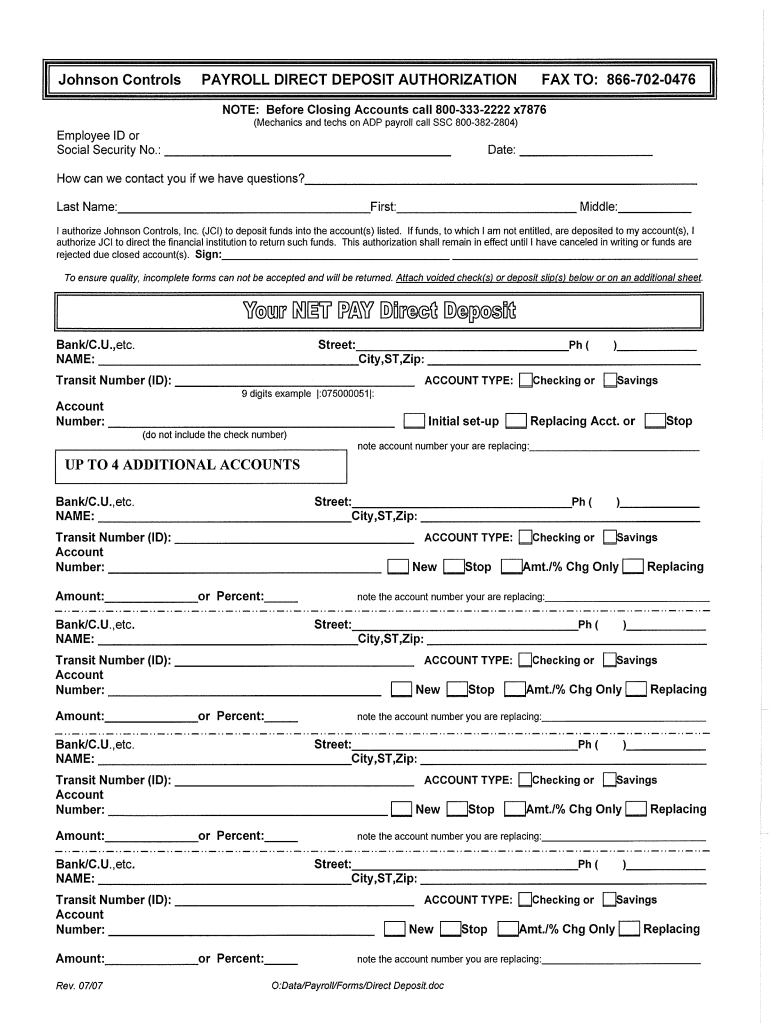
Jci Application
Use a Jci Application 2007 template to make your document workflow more streamlined.
Jci Application overview
Jci Application is a business document completed by an applicant and returned to the requesting organization. Because the available source material does not identify its issuing agency, field list, filing deadline, or required signature method, those details should be confirmed with the organization that supplied the form. In signNow, a sender uploads Jci Application, reviews detected fillable fields, assigns signer fields, and sends it electronically. The signer completes the requested information, reviews the record, signs when permitted, and receives a completed document supported by an audit trail.
Who uses Jci Application
Applicants
People completing Jci Application can enter information in a prepared signNow document, review the completed fields, and sign electronically when the receiving organization accepts electronic records.
Requesting organizations
Organizations requesting Jci Application can assign signers, track completion, and retain the signed document with its audit trail for internal records and later review.
How Jci Application works
Jci Application moves from preparation to signing through a controlled signNow workflow that keeps the completed document and signing evidence connected.
Upload form: Upload Jci Application to signNow. Prepare fields: Review detected fields and add missing fields. Send document: Send the application to its designated signer. Archive record: Store the signed file with its audit trail.
How the Jci Application audit trail works
The audit trail connects Jci Application to signer authentication, event timestamps, document integrity evidence, and a retrievable completion record.
Authenticate signer:
Capture timestamp:
Hash document:
Seal record:
Log actions:
Export evidence:
 Best ROI. Our customers achieve an average 7x ROI within the first six months.
 Scales with your use cases. From SMBs to mid-market, airSlate SignNow delivers results for businesses of all sizes.
 Intuitive UI and API. Sign and send documents from your apps in minutes.
Recommended Jci Application setup
Configure Jci Application around signer identity, electronic consent, audit evidence, encryption, and the receiving organization’s documented retention requirements.
| Setting | Recommendation |
|---|---|
| Authentication method | Email verification with SMS OTP |
| Signature type | Electronic signature with signer intent |
| Audit trail | Preserve completion history and timestamps |
| Document retention | Apply the receiving organization’s records policy |
| Encryption | AES-256 at rest with TLS 1.2 or 1.3 |
Why teams look for DocuSign alternatives
Organizations seek alternatives when they need different pricing models, stronger native automation, simpler bulk affidavit workflows, or more flexible identity-verification options than those available in a legacy envelope-based vendor.

Find and fill out the correct jci application
airSlate SignNow helps you fill in and sign documents in minutes, error-free. Choose the correct version of the editable PDF form from the list and get started filling it out.
| Versions | Form popularity | Fillable & printable |
|---|---|---|
| *2007 Johnson Controls Payroll Direct Deposit Authorization [2007-07] 2007 | 4.8 Satisfied (6968 Votes) |
Security for Jci Application
Data encryption:
Transport security:
Security certification:
Information security:
Electronic signatures:
Health data protection:
Platform requirements for Jci Application
Jci Application can be prepared through signNow in Chrome, Firefox, Safari, or Edge on Windows and macOS. signNow mobile apps support document review and signing on iOS and Android, while TLS 1.2 or TLS 1.3 protects data in transit.
Supported browsers Chrome, Firefox, Safari, and Edge Operating systems Windows, macOS, iOS, and Android Secure connection TLS 1.2 or TLS 1.3 connection
Organizations handling Jci Application records should use managed Windows, macOS, iOS, or Android devices, current browser releases, and controlled user access. Enterprise deployments may also require API access, SSO provisioning, and retention or certificate settings aligned with the organization’s records policy.
Privacy challenges with Jci Application
Personal identifiers may be exposed when unnecessary information is copied into Jci Application or shared with recipients outside the approved workflow. A signer may complete Jci Application without a recorded electronic-consent step, weakening evidence that the person intended to sign electronically. Incorrect recipient permissions can let an unintended user view, edit, or forward Jci Application before the requested signature is completed. A missing audit-trail export can separate the signed Jci Application from the event history needed to explain who signed and when.
Best practices for Jci Application
Accurate field review, preserved audit evidence, controlled storage, and documented retention decisions help keep Jci Application records usable after signing.
Verify fields before sending
Retain the audit trail
Use controlled archival
Check regulated information
Key performance indicators that demonstrate SignNow's proven track record.
Jci Application troubleshooting
These answers address field detection, signer assignment, plan selection, compliance, legal acceptance, and preservation of the completed Jci Application record.
Upload Jci Application as a PDF or supported document file, then review signNow’s detected fields. Auto-detection does not replace human review: confirm every field, signer assignment, required date, and instruction before sending the application.
Use signNow’s field assignment tools to designate the correct signer. If the application requires an authorized representative, confirm that person’s authority with the receiving organization before sending; signNow cannot decide who legally may sign Jci Application.
Business includes legally binding eSignatures, templates, audit trails, and mobile apps at $8 per user per month when billed annually. The available source material does not identify a Jci Application-specific plan requirement, so select a plan based on workflow volume and controls.
signNow lists HIPAA compliance with a business associate agreement, but HIPAA applies only when the workflow involves protected health information and a covered relationship. Confirm whether Jci Application contains PHI and obtain the required BAA before processing it.
signNow supports ESIGN and UETA compliance, but enforceability still depends on consent, intent, signer attribution, and record retention. Confirm that the receiving organization accepts electronic Jci Application signatures and check any state-specific or document-specific exclusion.
Export the completed Jci Application together with its audit trail. The audit trail preserves signing events and timestamps; store both in an access-controlled repository under the receiving organization’s documented retention policy rather than relying on the signed PDF alone.
BE READY TO GET MORE
Get this form now!

If you believe that this page should be taken down, please follow our DMCA take-down process.