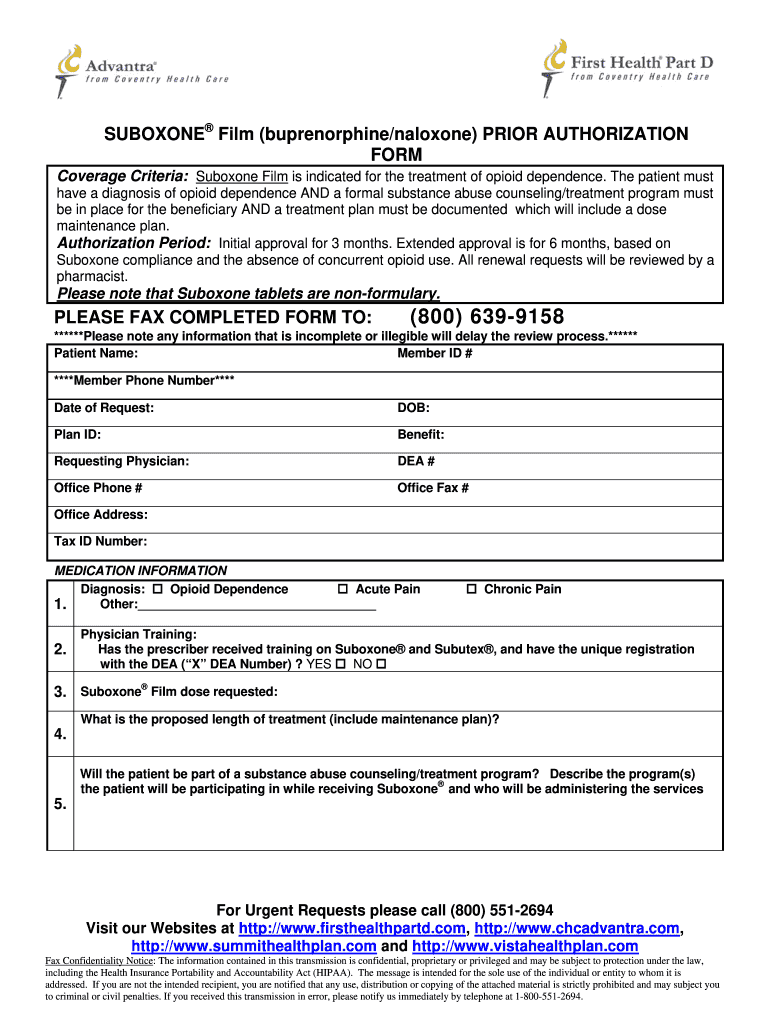
Coventry Prior Authorization Form (2012 2026)
Use a Coventry Prior Authorization Form 2012 template to make your document workflow more streamlined.
What the Coventry authorization form does
The Coventry Prior Authorization Form (2012 2026) is a healthcare request used to document payer approval before a specified service, treatment, medication, or procedure proceeds. The submitting provider supplies patient, diagnosis, service, and coverage information; the payer reviews the request under its authorization rules and returns a determination. The form does not itself guarantee payment or establish medical necessity. Organizations should confirm the current Coventry requirements, required attachments, submission channel, and response instructions before sending. signNow can prepare, route, sign, and retain the completed document when electronic signatures are permitted.
Business types using Coventry authorization forms
Coventry authorization workflows suit healthcare organizations that must collect accurate approvals before covered services proceed.
A solo behavioral-health practice uses the Coventry Prior Authorization Form to request insurer approval before treatment, then routes the completed authorization for patient and provider signatures through a controlled signNow workflow. A regional outpatient clinic coordinates provider, patient, and payer documentation for Coventry authorization requests, using reusable templates, delegated sending, and audit trails to reduce missing fields before submission. An enterprise health system standardizes Coventry authorization packets across departments, connects signNow with existing systems, and applies role-based access so sensitive patient information reaches only assigned participants.
These tasks are executed by both individual contributors and centralized administrators depending on organizational policy and required controls.
Who completes Coventry forms
Healthcare providers
Healthcare providers and utilization-review teams use Coventry authorization forms to document requested services, clinical justification, payer details, and required signatures before care proceeds.
Patients and representatives
Patients, caregivers, and authorized representatives review and sign the patient-facing portions when consent or acknowledgment is required for the Coventry request.
Complete the Coventry form online
Use this sequence to prepare the Coventry authorization request, collect signatures, and retain evidence of completion.
Upload form:
Upload the current Coventry form to signNow. Detect fields:
Let signNow detect fillable fields automatically. Check details:
Review patient, provider, payer, and service details. Send for signature:
Send the authorization to required signers. Store records:
Download the completed form and audit trail.
Audit trail for Coventry authorizations
The signNow audit trail records the technical events that connect each Coventry authorization signature to its document, signer, and completion history.
Authenticate signer:
Capture timestamp:
Hash document:
Seal record:
Log activity:
Export trail:
 Best ROI. Our customers achieve an average 7x ROI within the first six months.
 Scales with your use cases. From SMBs to mid-market, airSlate SignNow delivers results for businesses of all sizes.
 Intuitive UI and API. Sign and send documents from your apps in minutes.
Recommended Coventry workflow setup
Configure the Coventry authorization workflow around signer identity, protected health information, auditability, retention, and controlled access.
| Setting | Recommendation |
|---|---|
| Authentication method | Email link with SMS OTP |
| Signature type | Legally binding electronic signature |
| Audit trail | Enabled for every authorization packet |
| Document retention | Six years for HIPAA records |
| Encryption | TLS 1.2/1.3 and AES-256 at rest |
Signer authentication for Coventry forms
Digital certificates:
X.509 certificates:
Two-factor authentication:
SMS OTP:
ID verification:
Signing timestamps:
Find and fill out the correct coventry prior authorization form
airSlate SignNow helps you fill in and sign documents in minutes, error-free. Choose the correct version of the editable PDF form from the list and get started filling it out.
| Versions | Form popularity | Fillable & printable |
|---|---|---|
| *2012 Advantra CHCH 9098-3 [2012-09] 2012 | 4.8 Satisfied (3116 Votes) |
Platform requirements for Coventry forms
Use an up-to-date Chrome, Firefox, Safari, or Edge browser on Windows or macOS. signNow mobile apps support Coventry authorization review and signing on iOS and Android devices over TLS-secured connections.
Browsers Chrome, Firefox, Safari, Edge Desktop systems Windows and macOS desktops Mobile apps iOS and Android mobile apps
Healthcare organizations should use managed devices, role-based signNow access, and approved storage locations when Coventry forms contain protected health information. For HIPAA workflows, confirm that the required business associate agreement is in place and configure retention, authentication, and audit-trail export policies before production use.



Key signNow features for Coventry forms
signNow supports the document preparation, signature collection, evidence preservation, and controlled record handling needed for Coventry prior authorization workflows.
Field detection
Upload the Coventry PDF and use detected fields as a starting point, while staff verify every patient, provider, payer, and service entry before sending.
Signer routing
Route the authorization packet to providers, patients, or representatives in the required sequence, reducing manual forwarding and preserving the intended approval path.
Audit trail
Capture timestamps, signer activity, and completion evidence with the authorization record so staff can explain when and how each signature was obtained.
Mobile signing
Review and sign the Coventry packet from a desktop or supported mobile app when the payer and organization permit electronic execution.
Integrations
Connect authorization records with approved systems such as Salesforce, NetSuite, Google Drive, Box, or Microsoft 365 for controlled operational handling.
Protected records
Apply access controls, encryption, and retention policies appropriate for authorization packets that contain patient information or other regulated healthcare data.
Privacy issues in Coventry workflows
Patient identifiers or diagnosis details may appear in the signed PDF; send only required Coventry information and restrict access to assigned healthcare personnel. Missing patient consent or electronic-record disclosure can weaken the evidence supporting a signed authorization; document consent where consumer-facing requirements apply. Incorrect signer permissions can expose protected health information or route the request to an unauthorized recipient; use role-based access and verify every address. Uploading an outdated Coventry form can cause payer rejection or rework; confirm the current form version and required supporting documentation before routing.
Legal standing of electronic authorization
For a Coventry authorization, an electronic signature can carry the same legal effect as a handwritten signature when intent, consent, attribution, and record retention requirements are satisfied under ESIGN, 15 U.S.C. ch. 96, and applicable state law such as UETA. Confirm payer-specific acceptance before relying on electronic submission.

Best practices for Coventry records
Accurate retention, audit-trail export, and controlled archival help preserve the evidence surrounding each Coventry authorization decision.
Keep the authorization packet together
Export the audit trail promptly
Archive records securely
Record the governing retention rule
Coventry form troubleshooting questions
These answers address preparation, electronic-signature evidence, HIPAA safeguards, plan selection, and signer problems specific to Coventry authorization packets.
Upload the current Coventry PDF and use signNow’s field detection, then compare every detected field with the source form. Auto-detection can accelerate preparation, but staff must verify patient identifiers, provider details, requested services, and payer information before sending.
Use signNow’s audit trail, timestamps, and completion certificate to document intent, attribution, and the signing sequence. ESIGN and applicable state electronic-transactions law support electronic records when statutory requirements are met, but payer rules may impose additional submission requirements.
For Coventry packets containing protected health information, signNow identifies HIPAA compliance as available with a business associate agreement. Confirm the BAA and organizational configuration before transmitting PHI; platform compliance does not replace the provider’s privacy and security obligations.
The Business plan includes templates, audit trails, and mobile apps at $8 per user per month when billed annually. Business Premium is $15 and adds bulk send, while Enterprise is $30 and adds advanced signer authentication and integrations.
If multiple patients receive the same authorization packet structure, Business Premium includes bulk send. Review every recipient and patient-specific field before release; bulk sending does not remove the need for individual clinical accuracy or access controls.
If a signer cannot complete the request, review the recipient address, signing order, authentication method, and required fields. Resend or reassign only under documented authorization procedures, then retain the updated activity history with the final Coventry record.
Key performance indicators that demonstrate SignNow's proven track record.
BE READY TO GET MORE
Get this form now!

If you believe that this page should be taken down, please follow our DMCA take-down process.