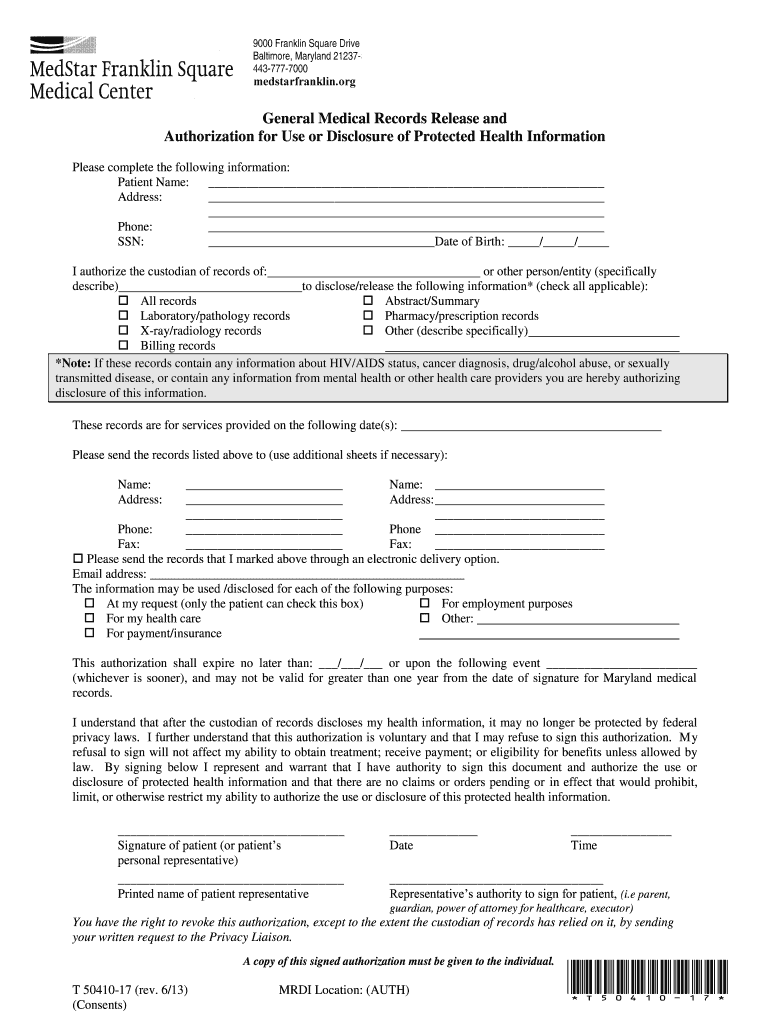
Authorization For Use Or Disclosure Medstar Health
Use a Authorization For Use Or Disclosure MedStar Health 2013 template to make your document workflow more streamlined.
What this MedStar Health authorization does
Authorization For Use Or Disclosure Medstar Health is a patient permission form that identifies what health information may be disclosed, who may receive it, and the purpose or limits of the disclosure. The patient reviews those terms, provides a signature and date, and returns the completed authorization to the responsible healthcare organization. A signNow workflow can upload the MedStar Health document, detect fillable fields, route it to the patient, capture the electronic signing event, and store the completed form with its audit trail. HIPAA documentation generally requires six-year retention under 45 CFR 164.530(j).
Business types that use this authorization
Medical practices, hospital departments, and health systems use this form when a patient’s written permission is needed before specified information is disclosed.
Independent medical practices use the authorization to document a patient’s permission for defined disclosures, reducing repeated paper handling while preserving a signed record for release-management workflows. Hospital departments use it to route patient-authorized disclosures to insurers, attorneys, or caregivers, with clear scope and recipient details that help staff apply minimum-necessary procedures. Enterprise health systems use standardized templates and delegated sending to manage authorization requests across locations, while administrators retain consistent controls, audit evidence, and HIPAA-aligned records.
These tasks are executed by both individual contributors and centralized administrators depending on organizational policy and required controls.
How to complete this authorization online
Use this sequence to prepare, sign, and preserve the specific MedStar Health authorization without changing its disclosure terms.
Upload form: Upload the MedStar Health authorization to signNow. Check fields: Review detected fields and add missing patient fields. Send securely: Send the authorization to the designated signer. Retain evidence: Store the signed form with its audit trail.
Features for MedStar Health authorizations
The workflow combines field preparation, signer routing, authentication evidence, and retention controls for this healthcare disclosure authorization.
Remote completion
Patients can complete the authorization remotely, reducing the need to return a paper copy while preserving the form’s stated recipient, purpose, and disclosure scope.
Field detection
Automatic field detection helps identify signature, date, and text areas after the MedStar Health document is uploaded, while staff can review and correct placement before sending.
Controlled routing
The workflow routes the authorization to the intended signer and records completion details, helping staff connect the patient’s consent with the correct disclosure request.
Audit trail
A signed copy and audit trail preserve evidence of the patient’s electronic signing event, including recorded actions associated with the completed authorization.
HIPAA workflow
HIPAA-compliant signNow use requires a business associate agreement where applicable and supports controlled handling of protected health information throughout the signing workflow.
Record retrieval
Completed authorizations can be organized with related disclosure records so staff can retrieve the patient’s permission when processing an authorized request.
 Best ROI. Our customers achieve an average 7x ROI within the first six months.
 Scales with your use cases. From SMBs to mid-market, airSlate SignNow delivers results for businesses of all sizes.
 Intuitive UI and API. Sign and send documents from your apps in minutes.
How the audit trail records signing
The audit trail connects the patient’s signing event with the completed MedStar Health authorization and its retained evidence.
Verify signer:
Capture timestamp:
Hash document:
Seal record:
Record events:
Export evidence:
Security for patient authorizations
HIPAA safeguards:
Data at rest:
Data in transit:
Control assurance:
Security certification:
Signing evidence:
Find and fill out the correct authorization for use or disclosure medstar health
airSlate SignNow helps you fill in and sign documents in minutes, error-free. Choose the correct version of the editable PDF form from the list and get started filling it out.
| Versions | Form popularity | Fillable & printable |
|---|---|---|
| *2013 Medstar Franklin Square T 50410-17 [2013-06] 2013 | 4.8 Satisfied (5875 Votes) |



Challenges when completing this authorization
The authorization may identify the wrong recipient or omit the permitted information, leaving staff unable to determine whether a requested disclosure falls within the patient’s consent. Patient identifiers and medical details can be exposed when completed forms are emailed broadly, stored without access controls, or downloaded to unmanaged devices. A missing signer identity, date, or electronic consent record can weaken the evidence that the patient authorized the specified disclosure. Using one broad authorization for unrelated purposes can conflict with minimum-necessary handling and the form’s stated disclosure scope.
Retention periods for authorization records
Retain records connected with this healthcare authorization according to the applicable HIPAA documentation rule and any longer MedStar Health policy or state requirement.
Six years for authorizations
Six years for privacy policies
Six years for complaints
Six years for training records
Six years for sanctions
Record-keeping practices for this form
A controlled record process helps preserve the patient’s authorization, disclosure scope, and evidence of signing throughout the required retention period.
Export the signed record and audit trail
Review every disclosure field before sending
Restrict access to protected health information
Align retention with legal holds and policy
Key performance indicators that demonstrate SignNow's proven track record.
Troubleshooting this authorization workflow
Resolve field, identity, privacy, and retention issues by checking the authorization terms, signNow configuration, and applicable HIPAA and ESIGN requirements.
Upload the original MedStar Health authorization again and inspect detected fields before sending. If a signature or date field is missing, add it manually and confirm that the patient, recipient, and disclosure terms remain unchanged. Business includes templates and audit trails; plan capabilities should be checked before deployment.
HIPAA-compliant signNow use requires a business associate agreement where applicable. Confirm the organization’s agreement and configuration before routing protected health information. HIPAA compliance does not replace the obligation to limit disclosure scope, verify recipients, and follow MedStar Health procedures.
Use an authentication method appropriate to the disclosure risk, such as SMS verification or stronger identity verification when configured. Preserve the resulting audit trail with the authorization. ESIGN and UETA focus on intent, consent, attribution, and record reproducibility; they do not decide whether disclosure is permitted.
Check that the signer received the correct request and that the email address or signing link belongs to the intended patient. Re-send only after confirming the authorization’s recipient, purpose, information scope, and expiration language. Keep one controlled completed record to prevent duplicate disclosure requests.
Download the signed authorization and audit trail from signNow, then store both under the organization’s access and retention controls. HIPAA 45 CFR 164.530(j) generally requires six-year retention for covered documentation, unless a longer state or organizational requirement applies.
A signNow electronic signature can support a healthcare authorization when the signer demonstrates intent, consents to electronic records, can be attributed, and the record remains reproducible. Consumer-facing records may also require the ESIGN disclosure and access procedures under 15 U.S.C. §7001(c).
BE READY TO GET MORE
Get this form now!

If you believe that this page should be taken down, please follow our DMCA take-down process.