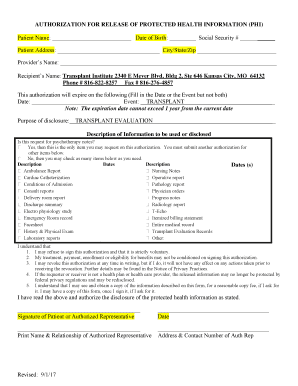
Authorization For Protected Health Information Phi
Use a Authorization For Protected Health Information PHI 2017 template to make your document workflow more streamlined.
What Authorization For Protected Health Information Phi does
Authorization For Protected Health Information Phi is a written permission for a covered entity to disclose specified protected health information to a named person or organization. It identifies the information, purpose, recipient, expiration, and individual’s signature. With signNow, a healthcare organization uploads the authorization, reviews detected fillable fields, assigns patient or representative fields, sends it for signature, and stores the completed document with an audit trail. HIPAA’s documentation rule generally requires six-year retention under 45 CFR 164.530(j).
Who uses this authorization
Healthcare providers
Healthcare providers use the authorization to obtain a patient’s permission before disclosing specified medical information to a named person, payer, attorney, or organization. Staff must match the recipient, purpose, information scope, expiration, and signature to the requested disclosure, then retain the completed record under HIPAA documentation procedures.
Patients and representatives
Patients and authorized representatives review what information may be disclosed, who may receive it, and why. They complete the signature and date fields, while representatives should provide any required authority documentation. signNow records the completed transaction and audit activity for the healthcare organization’s controlled archive.
Features for protected health information authorizations
Authorization For Protected Health Information Phi requires precise scope, recipient, purpose, expiration, and signature handling; signNow features organize those requirements into a traceable electronic workflow.
Field detection
Upload the authorization PDF and review detected fields before assigning patient, representative, date, purpose, and signature fields for completion.
Signer routing
Send the authorization to the patient or representative through a defined signing workflow, with recipient order and reminders configured before delivery.
Audit trail
Use audit-trail records to review signer actions, timestamps, authentication events, and completion evidence associated with the authorization.
HIPAA workflow
Keep protected health information within a workflow supported by signNow’s HIPAA compliance program when the required BAA is established.
Mobile signing
Let authorized recipients complete the form from a desktop or mobile device without requiring an in-person exchange of paper.
Reusable template
Reuse a reviewed authorization template so staff apply consistent fields, recipients, purposes, and expiration details across patient requests.
Recommended authorization workflow settings
Configure the authorization around restricted disclosure, verified recipients, documented intent, and retention obligations for protected health information.
| Setting | Recommendation |
|---|---|
| Authentication method | Use email plus SMS OTP for sensitive disclosures |
| Signature type | Use an electronic signature with explicit signing intent |
| Audit trail | Retain completion evidence with signer activity history |
| Document retention | Keep six years under HIPAA 45 CFR 164.530(j) |
| Encryption and provisioning | Use encrypted storage with role-based administrator access |
 Best ROI. Our customers achieve an average 7x ROI within the first six months.
 Scales with your use cases. From SMBs to mid-market, airSlate SignNow delivers results for businesses of all sizes.
 Intuitive UI and API. Sign and send documents from your apps in minutes.
How the authorization audit trail works
A signNow audit trail connects signer identity, document activity, and completion evidence so a healthcare organization can review the authorization later.
Authenticate signer:
Capture timestamps:
Hash document:
Seal record:
Track actions:
Export trail:
Platform requirements for signing
Authorization For Protected Health Information Phi can be prepared and signed through supported desktop browsers, including Chrome, Firefox, Safari, and Edge, on Windows or macOS. signNow also provides mobile apps for iOS and Android, allowing recipients to review and sign the authorization from a mobile device.
Browser support Chrome, Firefox, Safari, and Edge Operating systems Windows, macOS, iOS, and Android Signing devices Desktop browsers and signNow mobile apps
Healthcare organizations should use managed devices when protected health information is involved and restrict access through administrative permissions. Enterprise deployments may also evaluate API access, SSO provisioning, and audit-trail export requirements. Confirm the organization’s signNow configuration, BAA status, and internal device policy before sending patient authorizations.
Find and fill out the correct authorization for protected health information phi
airSlate SignNow helps you fill in and sign documents in minutes, error-free. Choose the correct version of the editable PDF form from the list and get started filling it out.
| Versions | Form popularity | Fillable & printable |
|---|---|---|
| *2017 Research Medical Center Authorization for Release of Protected Health Information (PHI) [2017-09-01] 2017 | 4.8 Satisfied (4603 Votes) |
Security controls for PHI authorizations
Stored data:
Transport security:
Healthcare compliance:
Control assurance:
Security management:
Signer verification:
Record-keeping practices for signed authorizations
Accurate retention and controlled archival help healthcare organizations demonstrate what Authorization For Protected Health Information Phi permitted and when it was completed.
Apply the HIPAA six-year rule
Export completion evidence
Restrict archived access
Check authorization scope
Privacy and disclosure pitfalls
Including unnecessary diagnoses or treatment details can expose more protected health information than the recipient needs. A missing purpose, recipient, expiration date, or signature can weaken the authorization’s clarity and usability. Sending the completed authorization to an unintended email address can disclose protected health information without proper safeguards. Unrestricted template access may let unauthorized staff view, edit, or send patient authorization forms.
Risks of incomplete authorization handling
Excessive scope
Consent dispute
Privacy incident
Proof gap
Processing stages for this authorization
The workflow moves from field review to signer completion and controlled archival; no universal signer turnaround period is established for this form.
Prepare the document
Deliver to signer
Complete signer review
Archive completed record
Troubleshooting authorization workflows
Resolve field, authentication, retention, and compliance questions before sending Authorization For Protected Health Information Phi to a patient or representative.
For a HIPAA workflow, signNow states that HIPAA compliance requires a business associate agreement. Confirm that the required BAA is in place before sending authorizations containing protected health information. The authorization itself should still identify the recipient, purpose, information scope, and expiration clearly.
Business includes legally binding eSignatures, templates, audit trails, mobile apps, ISO 27001, and SOC 2. Business Premium adds bulk send, while Enterprise adds advanced signer authentication. Select the plan based on workflow controls and confirmed healthcare requirements, not the form name alone.
A missing signature field usually means the uploaded PDF was not configured for the intended signer. Review the detected fields, add the signer’s signature, date, and required text fields, then send a test copy before distributing the authorization.
An email-only workflow may not provide enough assurance for a sensitive authorization. signNow supports two-factor authentication, SMS OTP, and advanced signer authentication features depending on configuration and plan. Choose the authentication method required by organizational policy and risk assessment.
HIPAA requires covered entities to retain certain documentation for six years from creation or its last effective date under 45 CFR 164.530(j). Confirm whether the authorization belongs in that retention category, then preserve the signed document and audit trail under your records policy.
Electronic signatures generally receive legal recognition under ESIGN and applicable state electronic-transactions law when intent, consent, attribution, and record reproduction are established. Healthcare organizations must also address HIPAA safeguards and consumer electronic-record disclosures where applicable.
Key performance indicators that demonstrate SignNow's proven track record.
BE READY TO GET MORE
Get this form now!

If you believe that this page should be taken down, please follow our DMCA take-down process.