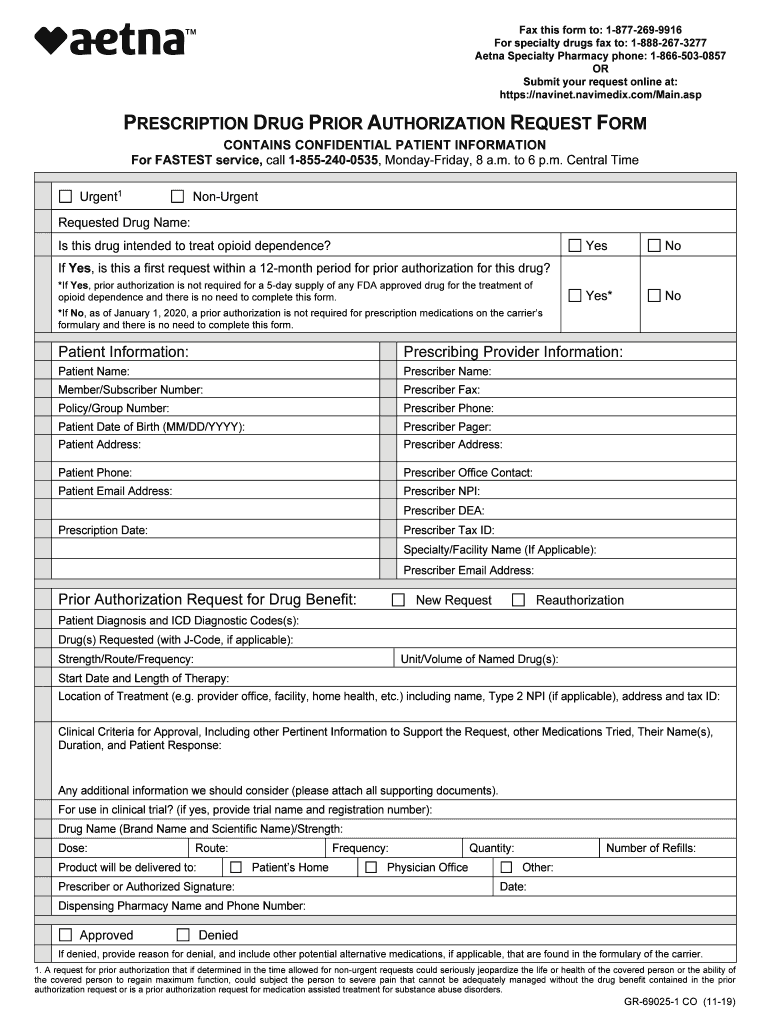
Co Prescription Drug Rior Authorization Request Form
Use a CO prescription drug rior authorization request form 2019 template to make your document workflow more streamlined.
What this prior authorization form does
The Co Prescription Drug Rior Authorization Request Form is a healthcare request used to obtain payer review before a prescribed medication is covered or supplied. A provider or authorized staff member enters the patient, prescriber, medication, coverage, and clinical-support information requested by the form, then routes it to the required parties. With signNow, the sender uploads the document, reviews detected fillable fields, assigns recipients, and sends it for signature. The completed form and audit trail document execution; the payer separately decides authorization under its policy.
Who uses this prior authorization form
Healthcare providers
Healthcare providers use the form to request payer authorization before dispensing or administering a prescribed medication. Staff verify patient, prescriber, medication, clinical rationale, insurance, and supporting-document fields before routing it for review and signature. A controlled electronic workflow reduces transcription and follow-up errors without replacing payer-specific submission rules.
Authorization teams
Pharmacy and medical-office teams use the form to coordinate authorization requests, attach supporting records, and document approvals. They can assign completion tasks, preserve the finalized request, and provide authorized personnel with an auditable record while following HIPAA privacy safeguards and the payer’s filing instructions.
Organizations that use this form
The form serves healthcare organizations that need documented payer authorization before a prescribed medication is dispensed, administered, or covered.
Solo prescribers can prepare and sign medication authorization requests remotely, reducing repeated printing while retaining the completed request and signing history for their office records. Independent pharmacies can coordinate provider signatures and supporting information through a defined recipient sequence, helping staff identify missing authorization details before payer submission. Enterprise health systems can standardize authorization templates, permissions, audit trails, and retention workflows across clinics while using HIPAA controls and a Business Associate Agreement where required.
These tasks are executed by both individual contributors and centralized administrators depending on organizational policy and required controls.
Complete the prior authorization request online
Use this sequence to prepare the request, validate its healthcare information, route it to the right parties, and retain the signed record.
Upload the form:
Upload the current Co Prescription Drug Rior Authorization Request Form PDF to signNow. Verify required fields:
Review detected fields and complete patient, prescriber, medication, and coverage information. Set recipients:
Add the payer, provider, or authorized reviewer as the correct recipient. Complete and store:
Send the request, collect signatures, and preserve the completed record with its audit trail.
Features for prior authorization workflows
signNow combines field review, recipient routing, audit evidence, and protected-document controls for teams preparing medication authorization requests.
Field review
Upload the request and inspect automatically detected fields before sending. Staff can correct missing or misplaced fields while preserving the original document structure for payer review.
Role routing
Route the authorization request to providers, patients, or payer representatives in a defined sequence. Recipient roles clarify who supplies information, signs, reviews, or receives the final record.
Audit trail
Capture signer identity, timestamps, actions, and document history in a signNow audit trail. The record helps teams demonstrate what occurred without treating an electronic signature as proof of medical necessity.
HIPAA workflow
Protect patient information through a configured HIPAA workflow and Business Associate Agreement when required. Access permissions and recipient selection remain organizational responsibilities for every authorization request.
Reusable templates
Use reusable templates for recurring authorization requests while reviewing patient-specific information each time. Business Premium adds bulk send for workflows involving multiple requests with consistent routing.
Record retention
Keep the finalized request and completion evidence together for authorized retrieval. Healthcare organizations should apply their own retention policy and the six-year HIPAA documentation rule when it governs the record.
 Best ROI. Our customers achieve an average 7x ROI within the first six months.
 Scales with your use cases. From SMBs to mid-market, airSlate SignNow delivers results for businesses of all sizes.
 Intuitive UI and API. Sign and send documents from your apps in minutes.
Recommended authorization workflow setup
Configure the request around verified recipients, protected health information, signature evidence, and the retention rule governing the healthcare record.
| Setting | Recommendation |
|---|---|
| Authentication method | Email verification with SMS OTP |
| Signature type | Typed or drawn electronic signature |
| Audit trail | Capture timestamps, actions, and recipients |
| Document retention | Six years when HIPAA 45 CFR §164.530(j) applies |
| Encryption | TLS 1.2/1.3 and AES-256 protection |
What the audit trail records
The signNow audit trail documents execution evidence separately from the payer’s clinical determination or authorization decision.
Authenticate signer:
Capture timestamp:
Record document hash:
Seal record:
Review history:
Export audit trail:
Find and fill out the correct co prescription drug rior authorization request form
airSlate SignNow helps you fill in and sign documents in minutes, error-free. Choose the correct version of the editable PDF form from the list and get started filling it out.
| Versions | Form popularity | Fillable & printable |
|---|---|---|
| Aetna GR-69025-1 CO 2019 | 4.8 Satisfied (2218 Votes) | |
| Aetna GR-69025-1 CO 2016 | 4.8 Satisfied (189 Votes) |



Security for healthcare authorization data
Data encryption:
Healthcare privacy:
Security assurance:
Information security:
Signer authentication:
Audit evidence:
Legal standing of the signed request
A properly executed electronic authorization request can carry electronic-record and signature evidence under ESIGN and applicable UETA rules when intent, consent, attribution, and record retention are established. Those laws do not guarantee payer approval, and exclusions such as wills, certain court filings, and family-law decrees do not describe this healthcare request.

Retention and record-keeping practices
Retain the request, supporting evidence, and audit history according to the applicable healthcare policy and the payer’s documentation requirements.
Apply the HIPAA six-year rule carefully
Export completion evidence together
Limit access to authorized personnel
Confirm payer submission requirements
Retention periods for authorization records
Retention depends on the record’s role, the covered entity’s policy, payer terms, and state law. The federal HIPAA documentation period is six years.
Six years: HIPAA documentation
Policy period: authorization records
Contract period: payer records
Longer period: state law
Approved period: audit evidence
Privacy pitfalls in authorization requests
Sending the request to an incorrect payer or recipient can expose patient information and delay review; verify addresses and authorization roles before delivery. Leaving clinical rationale, medication details, or insurance identifiers incomplete can cause payer rejection even when every required signature is present. Using a shared link without appropriate authentication can weaken access control for protected health information; apply the organization’s approved signer-verification policy. Treating the signed form as approval can create a coverage error because payer authorization remains a separate clinical and contractual decision.
Troubleshooting prior authorization requests
These answers address field detection, protected health information, signer access, plan limits, consent, and the difference between execution and payer approval.
On signNow’s Business plan, upload the completed Co Prescription Drug Rior Authorization Request Form, use automatic field detection, and manually verify every field before sending. The plan includes templates and audit trails, while Business Premium adds bulk send if multiple authorization requests require the same routing.
A prior authorization request can contain protected health information. signNow states that HIPAA compliance requires a Business Associate Agreement, so confirm the applicable account configuration and internal privacy controls before sending patient information to a payer or provider.
If the signer cannot open the request, confirm the recipient email address, resend the invitation, or use a controlled signing link. signNow’s Business plan supports signature invites and audit trails; use SMS or stronger authentication when organizational policy requires it.
Business includes 100 signature invites per user per year when billed annually, with overage fees after the included amount. Business Premium is $15 per user monthly annually billed and adds bulk send; confirm current account usage before sending large authorization batches.
For consumer-facing electronic records, ESIGN requires disclosure of the right to receive paper records, access to the electronic format, and withdrawal procedures under 15 U.S.C. §7001(c). Configure the workflow and notices accordingly; signNow’s audit trail records the signing events, not payer approval.
A completed electronic request does not guarantee coverage or payment. ESIGN and UETA address electronic-record and signature validity, while the payer’s policy controls authorization criteria, clinical documentation, submission channel, and response timing. Confirm those requirements separately before treating the request as approved.
Key performance indicators that demonstrate SignNow's proven track record.
BE READY TO GET MORE
Get this form now!

If you believe that this page should be taken down, please follow our DMCA take-down process.