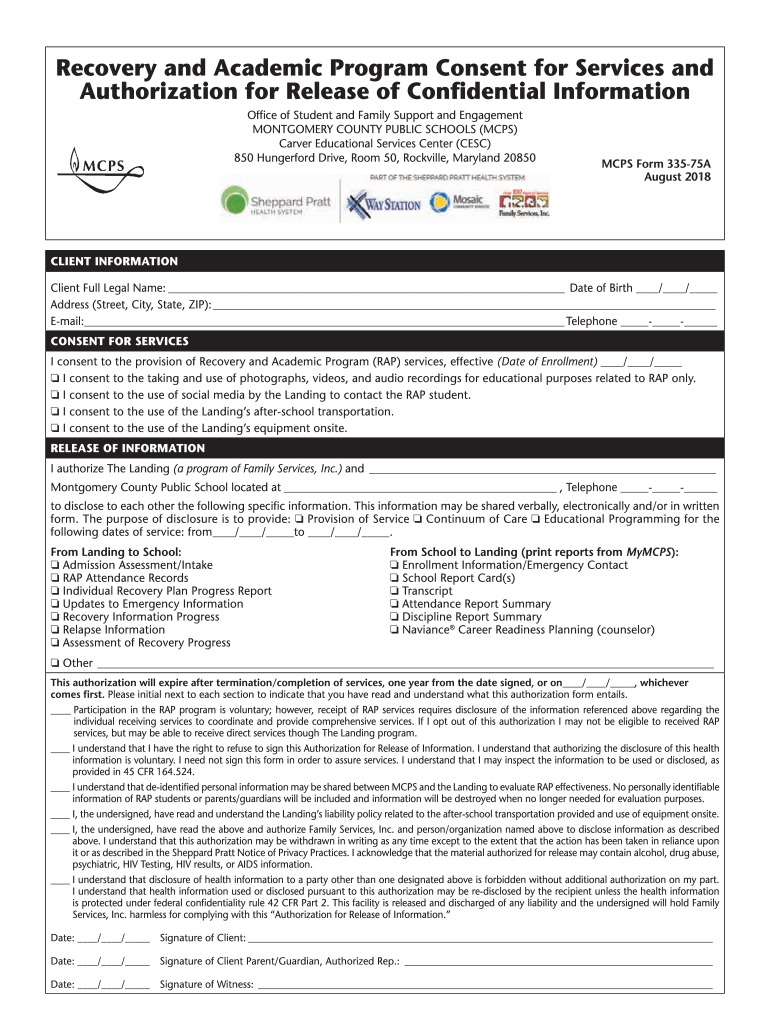
Authorization Form To Release Confidential Information
Use a Authorization Form To Release Confidential Information 2018 template to make your document workflow more streamlined.
What this authorization form does
An Authorization Form To Release Confidential Information gives a named person or organization permission to receive specifically identified private records. The signer usually states whose information may be disclosed, which records or dates are covered, the recipient, the purpose, the effective and expiration dates, and how consent can be revoked. The disclosing organization uses those limits to decide whether a request is authorized. In U.S. workflows, electronic execution may be recognized under ESIGN, UETA, or New York ESRA, subject to applicable exceptions and sector rules.
Legal standing for authorized disclosures
A completed authorization identifies consent, the intended disclosure, and the signer’s connection to the record. Electronic execution may support admissibility under ESIGN and applicable UETA or New York ESRA rules when intent, attribution, consent, and record retention are demonstrated. Wills, codicils, testamentary trusts, court orders, and family-law decrees remain outside these electronic-signature rules.

Business types that use this form
Authorization forms help organizations document consent before releasing confidential records to an identified recipient.
A solo healthcare practice can use the form to obtain a patient’s consent before sending specified records to another provider, attorney, insurer, or family representative, while preserving the signed authorization and disclosure purpose in one accessible file. A regional legal practice can standardize authorizations for client records, assign signing roles, and keep each completed release with its matter documentation, reducing uncertainty about the recipient, scope, expiration, and evidence of client consent. An enterprise healthcare network can use shared templates, administrator-controlled permissions, and audit trails to coordinate confidential-information releases across departments without giving every employee unrestricted access to patient authorizations.
These tasks are executed by both individual contributors and centralized administrators depending on organizational policy and required controls.
Who uses this authorization form
Healthcare providers
Healthcare providers use this authorization to document a patient’s permission before releasing specified medical information to a named person, insurer, attorney, or organization. The workflow should identify the records, purpose, expiration, and revocation process, while HIPAA-covered disclosures require safeguards appropriate to protected health information.
Records administrators
Schools, employers, legal practices, and financial service organizations use the form when a person authorizes a defined disclosure of confidential records. Teams can prepare a reusable template, collect the signer’s consent, and retain the completed authorization alongside the related request or case file.
 Best ROI. Our customers achieve an average 7x ROI within the first six months.
 Scales with your use cases. From SMBs to mid-market, airSlate SignNow delivers results for businesses of all sizes.
 Intuitive UI and API. Sign and send documents from your apps in minutes.
Features for confidential information releases
signNow combines field preparation, controlled signing, audit evidence, and secure storage for authorization workflows involving confidential records.
Field detection
Upload the authorization, place fields for the signer and recipient, and collect the required information without recreating the document. Auto-detected fields can speed preparation while still allowing the sender to review every field before delivery.
Signer routing
Route the form to the person authorizing release, the recipient, or an internal reviewer in the required order. Role-based routing helps prevent an unauthorized person from approving disclosure before the signer provides consent.
Electronic consent
Capture intent through a typed, drawn, or click-to-sign electronic signature connected to the authorization record. The completed document can demonstrate who signed, when the action occurred, and which version was executed.
Audit trail
Use an audit trail to preserve signing events, timestamps, signer activity, and document history. Store the trail with the authorization so staff can explain how consent was collected if a disclosure is later questioned.
Secure storage
Keep the authorization and signed copy in a controlled repository instead of scattered email attachments. Access restrictions and organized storage help staff locate the exact release record without exposing unrelated confidential information.
Reusable templates
Reuse an approved authorization template for recurring releases while keeping the recipient, purpose, information scope, and dates specific to each request. Templates reduce omissions without turning a limited consent into blanket permission.
Recommended authorization workflow setup
Configure each Authorization Form To Release Confidential Information around limited disclosure, verified consent, and defensible recordkeeping.
| Setting | Recommendation |
|---|---|
| Authentication method | Email delivery with SMS verification |
| Signature type | Typed or drawn electronic signature |
| Audit trail | Retain certificate and activity history |
| Document retention | Six years for HIPAA records |
| User provisioning | Admin-managed roles with encrypted access |
Find and fill out the correct authorization form to release confidential information
airSlate SignNow helps you fill in and sign documents in minutes, error-free. Choose the correct version of the editable PDF form from the list and get started filling it out.
| Versions | Form popularity | Fillable & printable |
|---|---|---|
| *2018 MD MCPS Form 335-75A [2018-08] 2018 | 4.8 Satisfied (1491 Votes) |
How to complete this authorization
Prepare the release scope first, then use signNow to collect consent and preserve evidence for the specific confidential-information request.
Upload form:
Upload the completed authorization document to signNow. Check fields:
Review detected fields and add missing signer, date, and consent fields. Route signing:
Send the form to the identified authorizing signer. Archive records:
Store the signed form, completion certificate, and audit trail together.
What the audit trail records
A signNow audit trail connects the authorization, signer activity, timestamps, and completion evidence needed to review a confidential-information release.
Authenticate signer:
Capture timestamp:
Hash document:
Seal record:
Log activity:
Export evidence:
Avoid scope and disclosure errors
Define the recipient and purpose
Limit the information scope
Set dates and revocation terms
Preserve proof of consent
Protect confidential release records
Data in transit:
Data at rest:
Security reporting:
Information security:
Health information:
Electronic signatures:
Troubleshoot authorization and signing issues
Resolve the issue by checking the form’s release scope, signer identity, electronic-consent requirements, and retained evidence before disclosing confidential information.
Upload the original authorization and review signNow’s detected fields before sending. Add or correct signer, date, recipient, and consent fields manually when detection misses them. The sender remains responsible for confirming that the final document reflects the intended release scope.
The Business plan includes legally binding eSignatures, templates, audit trails, mobile apps, ISO 27001, SOC 2, and GDPR support. HIPAA workflows require compliance configuration and a business associate agreement where protected health information is involved.
ESIGN and UETA can recognize electronic signatures when intent, consent, attribution, and record retention are established. Consumer-facing records also require the ESIGN consumer disclosure under 15 U.S.C. §7001(c), including paper access and withdrawal procedures.
Use signNow’s signer authentication options, including email delivery and SMS-based verification where configured, when the information requires stronger identity assurance. Match the authentication method to organizational policy, state requirements, and the sensitivity of the records being released.
Keep the signed authorization and certificate of completion with the audit trail, then apply the retention rule for the underlying record. HIPAA-covered documentation requires six years from creation or the last effective date under 45 CFR §164.530(j).
Business Premium adds bulk send and kiosk mode, while Enterprise adds advanced signer authentication, formula fields, and conditional fields. Choose the plan based on the release workflow; do not assume a plan changes the legal scope of consent.
Key performance indicators that demonstrate SignNow's proven track record.
BE READY TO GET MORE
Get this form now!

If you believe that this page should be taken down, please follow our DMCA take-down process.