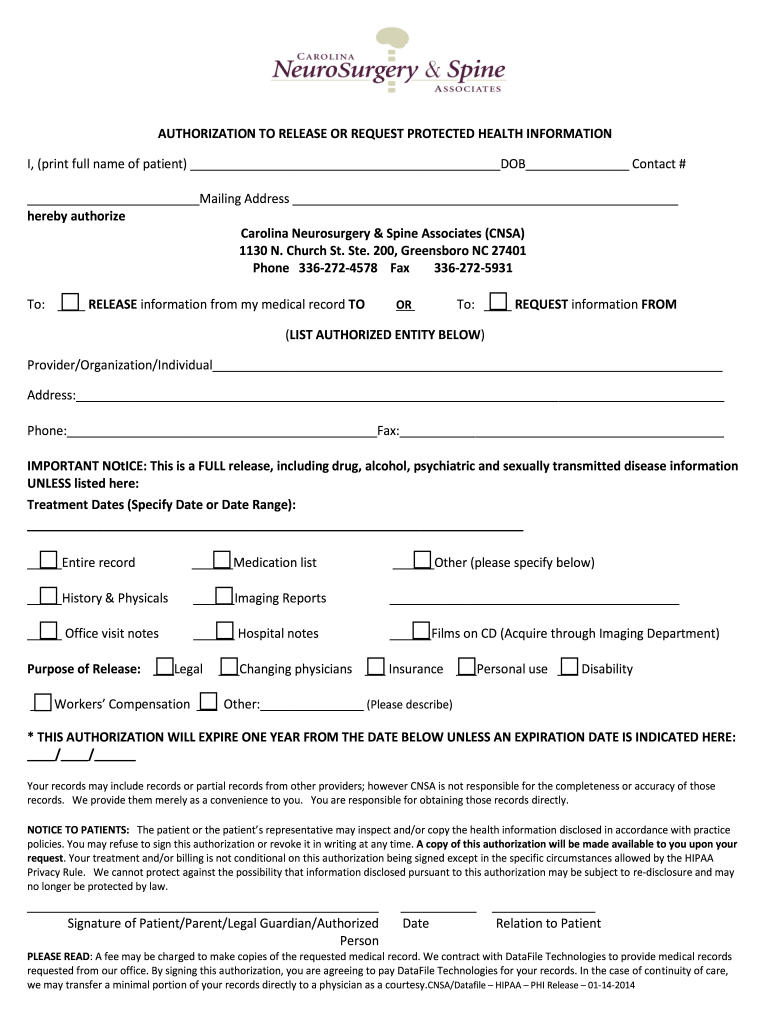
Authorization To Release Or Request Protected Health Information
Use a AUTHORIZATION TO RELEASE OR REQUEST PROTECTED HEALTH INFORMATION 2014 template to make your document workflow more streamlined.
What this health authorization does
An Authorization To Release Or Request Protected Health Information gives a patient a documented way to permit a named person or organization to obtain specified health information. The form identifies the patient, requested records, recipient, purpose, and signature or date details. A clinic can upload the authorization to signNow, add or confirm fillable fields, send it to the patient, and preserve the completed document with its audit trail. HIPAA’s documentation rule generally requires six-year retention from creation or last effective date under 45 CFR 164.530(j).
Who completes this health authorization
A medical-records coordinator at a multispecialty clinic uses the authorization to document a patient’s permission, identify the recipient, and route a protected health information request for signature through a HIPAA-compliant workflow. A fertility-care administrator, such as the team served by Fertility Centers of Illinois, uses reusable authorization templates to collect patient signatures, preserve consent details, and return completed records requests without relying on paper exchanges.
Complete the authorization in signNow
Prepare the health information authorization in four focused stages, checking every disclosure field before the patient signs.
Upload document:
Upload the authorization PDF. Add fields:
Confirm patient and recipient fields. Invite signer:
Send the authorization for signature. Archive record:
Review the signed copy and audit trail.
Choose a signing method for patients
- Use the signNow web app to upload the authorization, detect or add patient and recipient fields, and send the completed document by email when staff manage records from a desktop.
- Use the signNow mobile app when a patient or staff member must review and sign the authorization on an iOS or Android device during an appointment or outreach visit.
- Use kiosk mode for an in-clinic signing station where patients complete the authorization directly on a managed device; Business Premium includes kiosk mode according to the plan details.
- Generate a shareable signing link when a clinic needs to place the same authorization in a patient portal, message, or controlled intake page without emailing each invitation.
What the authorization audit trail records
The signed authorization and its audit trail connect the patient’s consent event to the protected health information request without replacing the clinic’s HIPAA recordkeeping policy.
Signer authentication:
Timestamp capture:
Document hashing:
Tamper-evident seal:
Audit event log:
Audit-trail export:
 Best ROI. Our customers achieve an average 7x ROI within the first six months.
 Scales with your use cases. From SMBs to mid-market, airSlate SignNow delivers results for businesses of all sizes.
 Intuitive UI and API. Sign and send documents from your apps in minutes.
Key features for health authorizations
signNow combines document preparation, patient signing, and audit evidence for an authorization that permits a defined protected health information disclosure.
Field preparation
Upload the authorization PDF and use detected or manually placed fields for the patient, recipient, purpose, signature, and date, reducing omissions before the request is sent.
Patient invitations
Send the specific authorization to a patient by email or signing link, allowing the clinic to control who receives the document and when the signing request begins.
Reusable templates
Use reusable templates for recurring release requests while reviewing each recipient, purpose, and information category before sending a new authorization.
Audit trail
Capture timestamps, signer actions, and completion evidence in an audit trail that can accompany the signed authorization during records review.
Mobile signing
Use signNow mobile apps when the patient completes the authorization on an iOS or Android device during a healthcare interaction.
HIPAA controls
HIPAA-compliant signNow workflows require a BAA when applicable, while encryption and access controls help protect the authorization and its health information.



Find and fill out the correct authorization to release or request protected health information
airSlate SignNow helps you fill in and sign documents in minutes, error-free. Choose the correct version of the editable PDF form from the list and get started filling it out.
| Versions | Form popularity | Fillable & printable |
|---|---|---|
| *2014 NC Neurosurgery & Spine Associates Authorization to Release/Request Protected Health Information [2014-01-14] 2014 | 4.7 Satisfied (327 Votes) |
Platform requirements for patient signing
Patients and staff can open this authorization in Chrome, Firefox, Safari, or Edge on Windows and macOS, while signNow mobile apps support iOS and Android signing. Secure browser connections use TLS.
Browsers Chrome, Firefox, Safari, Edge Desktop systems Windows and macOS desktops Mobile systems iOS and Android mobile apps
Healthcare organizations should use managed Windows, macOS, iOS, or Android devices when protected health information appears in the authorization. Configure access, identity controls, API connections, and retention policies through the selected signNow deployment, and confirm that the organization’s HIPAA obligations and BAA requirements are addressed before production use.
Protect authorization and PHI records
HIPAA coverage:
Data encryption:
Transport security:
Security assurance:
Information security:
Audit evidence:
Recommended authorization workflow setup
Configure the authorization workflow around patient identity, limited disclosure, signed-record integrity, and the applicable HIPAA retention rule.
| Setting | Recommendation |
|---|---|
| Authentication method | Email invitation with SMS OTP |
| Signature type | Typed or drawn patient signature |
| Audit trail | Export with completed authorization |
| Document retention | 6 years under HIPAA 45 CFR 164.530(j) |
| Encryption | AES-256 at rest and TLS 1.2/1.3 |
Best practices for signed health records
Use these controls to keep the authorization specific, attributable, reviewable, and aligned with HIPAA recordkeeping responsibilities.
Apply the HIPAA six-year rule
Verify every disclosure field
Archive signed evidence securely
Review each patient authorization
Retention periods for related records
Keep this authorization with the record class it supports, applying the controlling federal rule and any longer state or organizational policy.
HIPAA 6-year retention
Tax records 3-year retention
Tax records 6-year exception
I-9 retention rule
OSHA 5-year retention
Privacy pitfalls in health authorizations
Including an entire medical record when the patient intended to authorize only a defined diagnosis, treatment period, provider, or record category creates unnecessary disclosure exposure. Sending the authorization to the wrong recipient or using an unrestricted link can expose protected health information and undermine the patient’s documented disclosure choice. Omitting the purpose, expiration condition, or patient signature can leave the receiving organization unable to confirm that the authorization covers the requested release. Granting every staff member access to signed authorizations increases privacy risk; role-based permissions and controlled storage should match each employee’s records responsibility.
Troubleshoot this health authorization
Use these targeted checks when a patient authorization, protected health information request, or signed record does not move through the workflow.
Upload the authorization as a PDF or reusable template, then use signNow’s field detection and editor to place the patient’s signature, date, recipient, and disclosure fields. The Business plan includes templates and audit trails; confirm each detected field against the authorization’s intended disclosures before sending.
HIPAA compliance requires a business associate agreement when signNow handles protected health information for a covered entity. signNow identifies HIPAA compliance as available with a BAA; select the applicable agreement and configure access controls before routing this authorization.
A patient can sign through an emailed invitation or a shareable signing link, depending on the workflow. For stronger attribution, signNow Business Premium and Enterprise provide plan-specific capabilities such as kiosk mode or advanced signer authentication; verify the selected plan before deployment.
The authorization should identify the information released, purpose, recipient, patient, and expiration or applicable event. signNow’s fields and audit trail preserve the signed record, but the clinic remains responsible for using language that satisfies HIPAA and applicable state law.
Business includes audit trails and templates at $8 per user per month when billed annually. Subscription plans include 100 signature invites per user per year, with overage fees; the Site License uses $1.50 per signature invite for qualifying high-volume deployments.
Export the completed authorization and its audit trail from signNow, then place both in the designated health-record repository. HIPAA requires covered entities to retain required documentation for six years from creation or last effective date under 45 CFR 164.530(j).
Key performance indicators that demonstrate SignNow's proven track record.
BE READY TO GET MORE
Get this form now!

If you believe that this page should be taken down, please follow our DMCA take-down process.