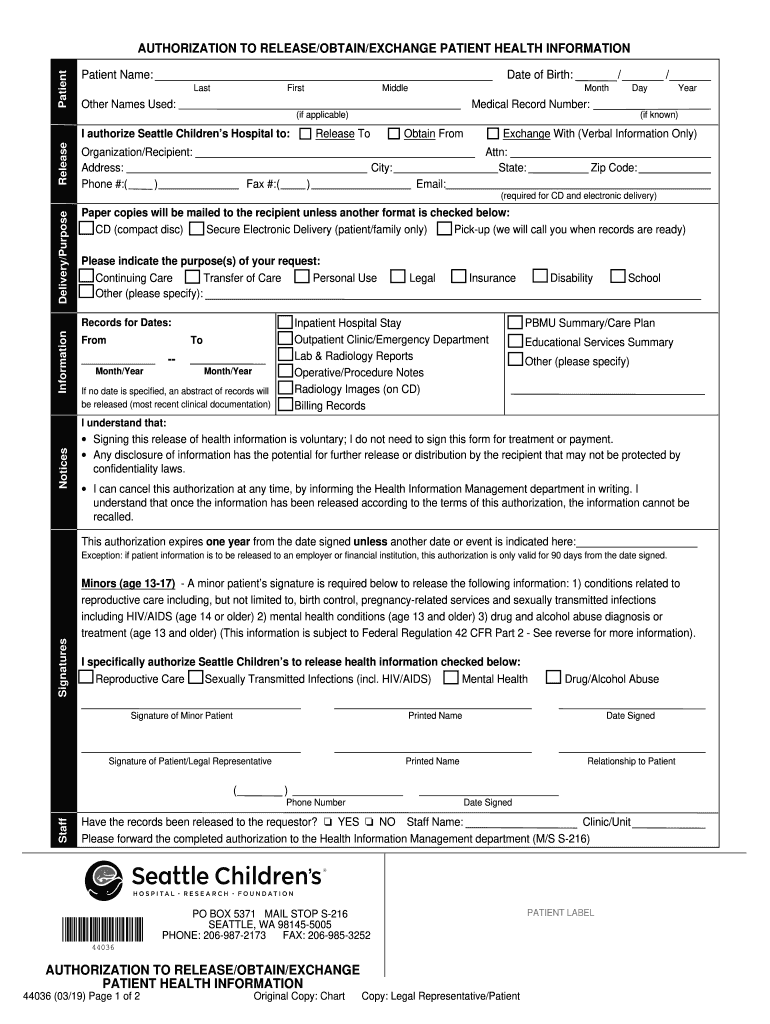
Authorization To Releaseobtainexchange Patient Health
Use a Authorization To ReleaseObtainExchange Patient Health 2019 template to make your document workflow more streamlined.
What this patient authorization does
Authorization To Releaseobtainexchange Patient Health is a written permission for a healthcare provider or other covered entity to disclose specified patient health information to named recipients. The form identifies the patient, information covered, purpose, recipient, expiration or revocation terms, and required signatures. With signNow, the sender uploads the form, places or confirms fillable fields, routes it to the patient and other required signers, and preserves the completed document with an audit trail. HIPAA 45 CFR 164.508 governs authorization content, while HIPAA 45 CFR 164.530(j) addresses six-year documentation retention.
Who uses this health authorization
Healthcare providers
Healthcare providers use the form before releasing defined medical records to another provider, insurer, attorney, caregiver, or organization. The authorization should identify the patient, information categories, recipient, purpose, expiration terms, and signature so the disclosure remains limited to the permission granted.
Patients and representatives
Patients and authorized representatives use the form to direct disclosure of selected health information. They review the recipient, purpose, expiration, revocation instructions, and signature requirements before returning the completed authorization to the covered entity.
Who benefits from patient authorizations
Authorization To Releaseobtainexchange Patient Health is most useful when healthcare organizations must document exactly what information a patient permits another person or organization to receive.
Solo physicians and small clinics use the authorization to obtain patient permission before releasing records to insurers, specialists, attorneys, or designated family members. The signed copy and audit trail help document the patient’s stated scope and recipient. Hospital and behavioral-health teams use reusable templates to route patient authorizations across departments, while applying HIPAA controls and retaining the completed record for six years under 45 CFR 164.530(j). Enterprise healthcare networks use role-based workflows, integrations, and audit trails to manage high-volume authorizations across facilities. Administrators can standardize templates while local teams send forms for patient review and signature.
These tasks are executed by both individual contributors and centralized administrators depending on organizational policy and required controls.
Key features for patient health releases
signNow combines document preparation, signer routing, authentication, and audit evidence for the specific details required by a patient health-information authorization.
Field preparation
Upload the existing authorization and use detected fields to prepare patient, recipient, purpose, scope, expiration, and signature areas without rebuilding the document.
Controlled routing
Route the authorization to the patient and organizational signers in a defined order, reducing email exchanges and keeping each required signature attached to the same record.
Audit evidence
Use signNow’s audit trail to preserve timestamps, signer actions, and completion evidence alongside the signed authorization for later review.
Signer verification
Apply SMS verification or other configured signer authentication to strengthen attribution before a patient signs the health-information release.
Reusable template
Reuse an approved authorization template while allowing the sender to enter the patient’s specific recipient, information scope, purpose, and expiration details.
Mobile access
Access the authorization workflow through signNow mobile apps when healthcare staff must prepare or review records away from a desk.
How the patient authorization process works
This workflow moves a patient health authorization from preparation through electronic signature, verification, and controlled record storage.
Upload the form: Upload the completed authorization form and confirm its healthcare-specific fields. Add recipients: Add the patient, authorized recipient, and requested disclosure details. Request signatures: Send the authorization for review and secure electronic signatures. Archive records: Store the signed authorization with its completion certificate and audit trail.
 Best ROI. Our customers achieve an average 7x ROI within the first six months.
 Scales with your use cases. From SMBs to mid-market, airSlate SignNow delivers results for businesses of all sizes.
 Intuitive UI and API. Sign and send documents from your apps in minutes.
How to complete the authorization
Follow these steps to prepare, sign, and retain Authorization To Releaseobtainexchange Patient Health with signNow.
Upload form:
Upload the Authorization To Releaseobtainexchange Patient Health PDF to signNow. Review fields:
Confirm fields for patient identity, recipient, scope, purpose, and expiration. Add signers:
Add the patient and any required organizational signers. Send request:
Send the authorization and monitor completion in signNow. Store records:
Download the signed form and audit trail for controlled storage.
Recommended authorization workflow setup
Use a controlled configuration that verifies patient signers, records each authorization event, and limits access to approved healthcare personnel.
| Setting | Recommendation |
|---|---|
| Authentication method | SMS verification for patient signers |
| Signature type | Intent-based electronic signature under ESIGN and UETA |
| Audit trail | Capture timestamps, signer actions, and completion certificate |
| Document retention | Six years under HIPAA 45 CFR 164.530(j) |
| Encryption and provisioning | TLS 1.2 or 1.3, AES-256, and controlled user provisioning |
Find and fill out the correct authorization to releaseobtainexchange patient health
airSlate SignNow helps you fill in and sign documents in minutes, error-free. Choose the correct version of the editable PDF form from the list and get started filling it out.
| Versions | Form popularity | Fillable & printable |
|---|---|---|
| *2019 WA Seattle Children’s Hospital 44036 [2019-03] 2020 | 4.8 Satisfied (2180 Votes) | |
| *2019 WA Seattle Children’s Hospital 44036 [2019-03] 2019 | 4.8 Satisfied (3785 Votes) |
Mobile options for patient authorizations
Staff can prepare or review Authorization To Releaseobtainexchange Patient Health through the signNow mobile app on iOS and Android, while browser workflows support desktop preparation and signing. Use encrypted connections and organization-approved devices when handling protected health information.
iOS app iOS 15 or later with the signNow mobile app Android app Android 9 or later with the signNow app Camera capture Camera capture for scanning patient authorization pages
Mobile access does not replace healthcare privacy controls. Configure managed iOS or Android devices, restrict downloaded copies, and confirm that camera-captured pages are uploaded to the approved signNow workflow. Organizations should separately evaluate offline use, API access, SSO provisioning, and retention configuration against their HIPAA policies and business associate agreement.



Security for patient authorizations
Supports protected health information workflows:
Independent security controls report:
Certified information security management:
Encrypts stored document data:
Protects data in transit:
Records signer actions and timestamps:
Authorization record retention schedule
Retain each signed authorization according to the health information, tax, and state-record rules governing the underlying transaction.
Six years from creation or last effective date
Three years from tax filing
Six years for major understatement
Longer period under state law
Policy period after approval
Best practices for retaining authorizations
A reliable record policy connects the signed patient authorization, its audit evidence, and the healthcare organization’s retention and access controls.
Apply the six-year HIPAA retention period
Export the signed record and audit trail
Archive records with restricted access
Validate scope before patient signature
Privacy and disclosure challenges
Listing broad categories instead of specific health information can make the authorization’s disclosure scope unclear and increase review delays before release. Entering the wrong recipient email address can expose protected health information to an unintended person or organization. Omitting an expiration date, purpose, or revocation instruction can require correction before a covered entity honors the authorization. Saving the signed form without its audit trail can weaken evidence of signer identity, consent, timestamps, and document completion.
Troubleshooting patient authorization workflows
Use these answers to resolve field, signing, plan, authentication, and retention questions for Authorization To Releaseobtainexchange Patient Health.
Upload the source PDF, use signNow’s field detection, and review every patient, recipient, purpose, and expiration field manually. Business includes templates and audit trails; HIPAA workflows require the appropriate signNow agreement and organizational controls.
A typed, drawn, or click-to-sign signature can satisfy ESIGN and UETA when intent, consent, attribution, and record retention are demonstrated. For healthcare disclosures, confirm the authorization also contains HIPAA-required elements under 45 CFR 164.508.
Use signNow’s signer authentication options, including SMS verification where configured, and confirm the signer’s identity before release. Authentication supports attribution but does not replace the authorization’s required scope, purpose, recipient, or expiration terms.
The Business plan includes legally binding eSignatures, templates, audit trails, mobile apps, ISO 27001, and SOC 2. HIPAA compliance requires a business associate agreement and appropriate administrative, technical, and physical safeguards.
Business Premium adds bulk send and kiosk mode, while Enterprise adds advanced signer authentication, formula fields, and conditional fields. Choose the plan based on routing volume and controls rather than assuming every feature is included.
Export the completed authorization and audit trail, then retain them under the applicable policy. HIPAA 45 CFR 164.530(j) requires six years from creation or the last effective date for covered-entity documentation.
Key performance indicators that demonstrate SignNow's proven track record.
BE READY TO GET MORE
Get this form now!

If you believe that this page should be taken down, please follow our DMCA take-down process.