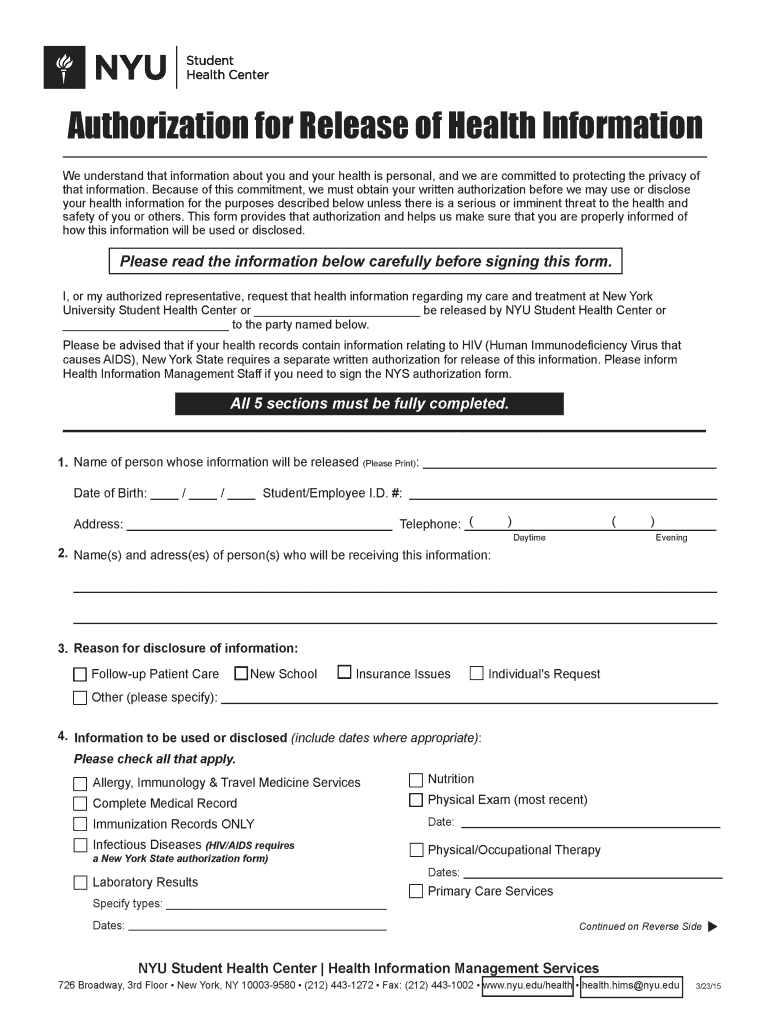
Instructions For Requesting A CO1V Of Vour Health Record Nyu
Use a Instructions For Requesting A Co1v Of Vour Health Record NYU 2015 template to make your document workflow more streamlined.
What this health-record request does
Instructions For Requesting A CO1V Of Vour Health Record Nyu is a written authorization used to ask a healthcare provider or records custodian for a copy of a patient’s health information. The requester identifies the patient, specifies the records or dates sought, names the recipient, and signs the authorization. With signNow, upload the form, review automatically detected fillable fields, add the authorized signer, send it for signature, and preserve the completed request with its audit trail. HIPAA-covered organizations should apply their privacy, disclosure, and retention procedures.
Who benefits from this request form
The form is most useful wherever a patient or authorized representative must approve a defined health-record copy request.
Solo healthcare practitioners can use the request to collect a patient’s authorization, identify the intended recipient, and preserve a signed copy without maintaining a paper-only workflow. Medical-records departments can route requests to patients or authorized representatives, verify completion, and retain the authorization with an audit trail for disclosure documentation. Enterprise healthcare systems can standardize templates, control staff access, and connect signed requests with HIPAA-governed records procedures across multiple clinics or departments.
These tasks are executed by both individual contributors and centralized administrators depending on organizational policy and required controls.
Legal standing for health-record requests
A signed request for a health-record copy can be evidence when intent, consent, signer attribution, and reliable record retention are established under ESIGN and applicable state law. Electronic records do not cover wills, codicils, testamentary trusts, court orders, official court filings, or family-law decrees.

Complete the request in four steps
Use this sequence to prepare, sign, and preserve a request for a copy of a health record with clear authorization evidence.
Upload form:
Upload the health-record request document. Check fields:
Review detected fields and add missing details. Send request:
Send the request to the authorized signer. Archive records:
Store the signed copy and audit trail.
Recommended request workflow settings
Configure the request around patient authorization, signer identity, protected health information, and documented retention obligations.
| Setting | Recommendation |
|---|---|
| Authentication method | Two-factor authentication for authorized requesters |
| Signature type | Intent-based electronic signature under ESIGN |
| Audit trail | Export completion certificate with signed request |
| Document retention | 6 years under HIPAA 45 CFR 164.530(j) |
| Encryption | AES-256 at rest and TLS 1.2/1.3 in transit |
 Best ROI. Our customers achieve an average 7x ROI within the first six months.
 Scales with your use cases. From SMBs to mid-market, airSlate SignNow delivers results for businesses of all sizes.
 Intuitive UI and API. Sign and send documents from your apps in minutes.
What the audit trail records
The audit trail documents the evidence surrounding this health-record authorization rather than replacing the authorization itself.
Authenticate signer:
Capture timestamps:
Protect document:
Record actions:
Export evidence:
Retrieve record:
Authenticate health-record request signers
PKI support:
X.509 certificates:
Two-factor authentication:
SMS OTP:
ID verification:
Signer attribution:
Find and fill out the correct instructions for requesting a co1v of vour health record nyu
airSlate SignNow helps you fill in and sign documents in minutes, error-free. Choose the correct version of the editable PDF form from the list and get started filling it out.
| Versions | Form popularity | Fillable & printable |
|---|---|---|
| *2015 NYU Authorization for Release of Health Information [2015-03-23] 2015 | 4.8 Satisfied (3432 Votes) |
Platform requirements for the request
Prepare Instructions For Requesting A CO1V Of Vour Health Record Nyu in Chrome, Firefox, Safari, or Edge on Windows or macOS. signNow uses TLS-secured connections and provides mobile apps for iOS and Android.
Browser support Chrome, Firefox, Safari, Edge Desktop systems Windows and macOS desktops Mobile systems iOS and Android mobile apps
Healthcare organizations should use managed Windows, macOS, iOS, or Android devices, restrict downloaded copies, and configure access through organizational controls. Teams handling protected health information should confirm a HIPAA-compliant signNow configuration and execute a business associate agreement where required.
Privacy pitfalls in health-record requests
Including unnecessary diagnoses or identifiers exposes protected health information beyond the copy request’s stated purpose. A missing patient authorization or representative relationship can prevent the provider from releasing the requested record. Sending the request to an unverified recipient may disclose health information to the wrong person or organization. Failing to preserve the signed request and audit trail weakens proof of consent, identity, and document integrity.
Best practices for preserving requests
Accurate scope, verified authorization, and controlled storage help demonstrate why the health-record copy was requested and who approved it.
Limit requested information to necessary records
Verify the authorized signer before disclosure
Preserve the audit trail with authorization
Apply the HIPAA six-year retention rule
Risks of incomplete requests
Consent dispute
Identity challenge
Evidence gap
Privacy violation
Health-record request retention schedule
Keep the signed request, authorization evidence, and related HIPAA documentation for the applicable federal period, while checking longer state requirements.
6 years from creation or last effective date
6 years from creation or last effective date
6 years from creation or last effective date
6 years from creation or last effective date
6 years from creation or last effective date
Troubleshooting health-record requests
These answers address field preparation, signer access, HIPAA handling, electronic-signature validity, plan selection, and retention for this specific request.
Upload the health-record request as a PDF or supported document, then inspect signNow’s detected fields manually. Add missing patient, representative, recipient, date-range, purpose, and signature fields before sending, because automatic detection does not determine whether the authorization is legally sufficient.
Business includes legally binding eSignatures, templates, and audit trails at $8/user/month when billed annually. Business Premium adds bulk send at $15/user/month. Select the plan based on document volume and workflow requirements, not merely the number of request forms.
signNow is HIPAA compliant when the required business associate agreement is in place. Configure access, authentication, storage, and disclosure procedures for protected health information; platform compliance does not replace the provider’s HIPAA policies or state-law obligations.
An electronic signature can satisfy ESIGN and UETA when the signer shows intent, consents to electronic records, can be identified, and the record remains reproducible. Consumer-facing disclosures may require paper-record and withdrawal information under 15 U.S.C. §7001(c).
If a patient or representative cannot complete the email flow, use SMS-based authentication or another configured signer-verification method. Confirm authority separately before disclosure; authentication supports identity evidence but does not create authorization by itself.
Preserve the signed request, completion certificate, and audit trail together. HIPAA requires covered-entity documentation retention for six years from creation or the last effective date under 45 CFR 164.530(j), while state law or policy may require longer.
Key performance indicators that demonstrate SignNow's proven track record.
BE READY TO GET MORE
Get this form now!

If you believe that this page should be taken down, please follow our DMCA take-down process.