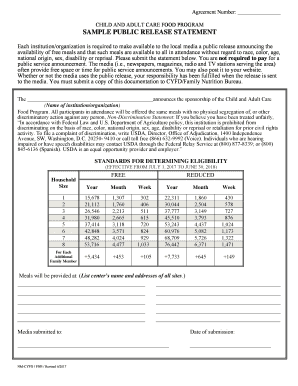
Public Release Statement
Use a Public Release Statement 2017 template to make your document workflow more streamlined.
What a Public Release Statement does
A Public Release Statement records a person’s permission to disclose or use specifically identified information. It should state who releases the information, who may receive it, what information is covered, the purpose, and any expiration or revocation terms. In a U.S. business workflow, the completed statement can be signed electronically when the signer demonstrates intent, consents to electronic records, and the record can be retained and reproduced. ESIGN and applicable state law support electronic execution, but exclusions such as wills and court orders require separate handling.
Business types using release statements
Public Release Statement is most useful when several people must approve, sign, or retrieve the same documented release.
A solo real estate broker can collect a property-related release from a client, preserve the signer’s consent, and keep the completed statement with its audit trail instead of coordinating separate paper exchanges. A healthcare practice can route a patient-facing release statement through a controlled workflow, verify the signer, and retain the signed record alongside its privacy documentation when protected information is involved. A multi-location enterprise can standardize release statements through shared templates, delegated sending, and administrator permissions, giving regional teams consistent fields while preserving centralized oversight of completed records.
These tasks are executed by both individual contributors and centralized administrators depending on organizational policy and required controls.
How this release workflow works
Move the exact statement from source file to signed, retrievable evidence through four controlled signNow actions.
Upload statement: Upload statement Place fields: Place fields Send for signature: Send for signature Store evidence: Store evidence
Inside the Public Release Statement audit trail
The audit trail connects signer identity, document integrity, and every material action into reviewable evidence for this release statement.
Authenticate signer:
Capture timestamps:
Hash document:
Seal record:
Log activity:
Export evidence:
Complete Public Release Statement on mobile
Use signNow on iOS 15 or later and Android 10 or later, with TLS 1.2 or 1.3 protecting connections.
Mobile apps iOS 15+ and Android 10+ support signNow mobile signing Offline signing Offline signing supports saved Public Release Statement documents Camera capture Camera capture imports paper statements into signNow
The signNow iOS and Android apps let authorized users review, complete, and sign Public Release Statement documents away from a desk. Camera capture can digitize paper copies, while offline work supports selected saved documents before synchronization when connectivity returns.
 Best ROI. Our customers achieve an average 7x ROI within the first six months.
 Scales with your use cases. From SMBs to mid-market, airSlate SignNow delivers results for businesses of all sizes.
 Intuitive UI and API. Sign and send documents from your apps in minutes.
Security controls for signed releases
Transport encryption:
Stored encryption:
SOC 2 Type II:
ISO 27001:
HIPAA safeguards:
ESIGN and UETA:
Recommended Public Release Statement setup
Configure the form around signer identity, documented intent, auditability, access control, and the retention policy governing this release.
| Setting | Recommendation |
|---|---|
| Authentication and provisioning | Use email verification with administrator-managed signers |
| Signature type | Use an electronic signature with signer intent |
| Audit trail | Capture timestamps, IP addresses, and action history |
| Document retention | Follow the applicable contract or privacy policy |
| Encryption | Use TLS 1.2 or 1.3 and AES-256 |
Find and fill out the correct public release statement
airSlate SignNow helps you fill in and sign documents in minutes, error-free. Choose the correct version of the editable PDF form from the list and get started filling it out.
| Versions | Form popularity | Fillable & printable |
|---|---|---|
| NM Kids Sample Public Release Statement 2019 | 4.8 Satisfied (1546 Votes) | |
| NM Kids Sample Public Release Statement 2017 | 4.8 Satisfied (3693 Votes) |
When the statement carries legal weight
A Public Release Statement may be admissible when the signer shows intent, consents to electronic records, can be identified, and the record remains reproducible under ESIGN, 15 U.S.C. chapter 96, and applicable UETA or New York ESRA rules. Wills, codicils, testamentary trusts, court orders, and family-law decrees remain excluded.

State rules and document exclusions
State notary rule
Wills and codicils
Court orders
Real-estate deeds
Record-keeping practices for release statements
Preserve the signed statement as evidence of the exact information released, the signer’s intent, and the transaction history supporting completion.
Keep the signed record and audit trail together
Export evidence after every completed statement
Restrict access to sensitive release information
Review scope and signer details before sending
Choose a signing method for this statement
- Use the web app when an administrator prepares the statement, places fields, and sends it from a desktop workflow to named signers.
- Use the mobile app when a signer reviews and completes the release statement from an iOS or Android device away from the office.
- Use kiosk mode for supervised, in-person completion when one organization manages repeated signers on a shared device.
- Use a shareable signing link when the statement must be distributed through an approved channel without preparing a separate email invitation.



Privacy pitfalls in release statements
Including social security numbers, medical details, or account data beyond the release purpose increases exposure if recipients or permissions are misconfigured. A vague recipient description can make the signer’s consent unclear and complicate later proof of what information the statement authorized. Sending the statement before confirming signer identity may attach consent to the wrong person or create an incomplete disclosure record. Leaving revocation, expiration, or effective-date fields blank can produce disputes about whether the release remained valid for a later request.
Public Release Statement troubleshooting
Resolve field, signer, compliance, plan, and retention questions before distributing this release statement to its intended recipients.
Upload the original Public Release Statement as a PDF, then use signNow field placement or automatic field detection to map names, dates, consent text, and signatures. Review every detected field before sending because signNow cannot determine whether the release scope or recipient is legally correct.
Business includes legally binding eSignatures, templates, audit trails, and mobile apps at $8 per user per month with annual billing. It includes 100 signature invites per user per year; overage fees can apply, so confirm volume before sending repeated statements.
Electronic execution can satisfy ESIGN and applicable UETA requirements when the signer shows intent, consents, can be identified, and the record remains reproducible. The form itself must not fall within exclusions such as wills, court orders, or family-law decrees.
If protected health information appears in the release, use a workflow that meets your organization’s HIPAA obligations and obtain the required signNow BAA. HIPAA compliance is listed as available with a BAA; it does not replace reviewing the statement’s authorization requirements.
Use signer authentication appropriate to the information released, such as email verification or SMS-based authentication where configured. For higher-risk disclosures, document the identity-control decision and confirm the signer can access and review the complete statement.
After completion, download the signed PDF and audit trail, then store both under the applicable organizational policy. signNow records timestamps, IP information, and document history, but retention duration depends on the underlying record and governing authority.
Key performance indicators that demonstrate SignNow's proven track record.
BE READY TO GET MORE
Get this form now!

If you believe that this page should be taken down, please follow our DMCA take-down process.