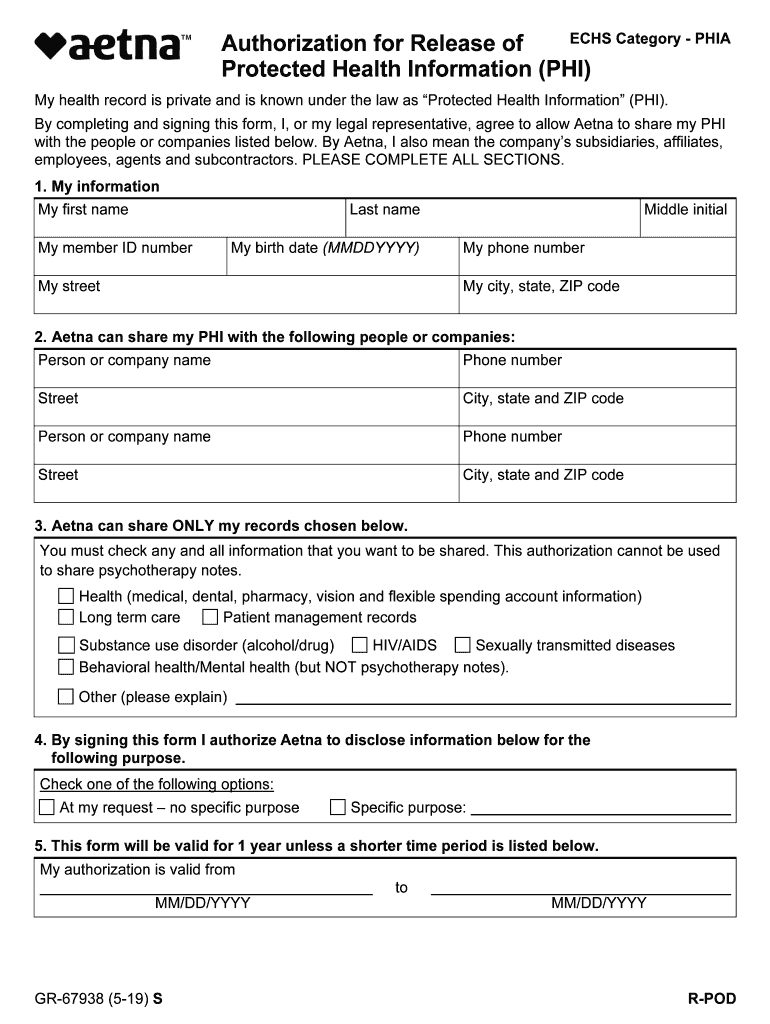
Aetna Authorization For Release Of Protected Health Information Phi
Use a Aetna Authorization For Release Of Protected Health Information PHI 2019 template to make your document workflow more streamlined.
What the Aetna authorization does
The Aetna Authorization For Release Of Protected Health Information Phi lets a patient authorize Aetna or another designated holder of protected health information to disclose specified records to a named recipient. The signer identifies the information, recipient, purpose, expiration or revocation terms, and signature date. A valid release should be completed voluntarily, describe the information and recipient clearly, and comply with HIPAA authorization requirements. signNow can turn the supplied form into a fillable workflow, route it for signature, and preserve the completed record and audit trail.
Who uses this authorization
Patients and representatives
Patients or their authorized representatives complete the release by identifying the records Aetna may disclose, the recipient, the purpose, and any expiration or revocation terms. The signer should review every field before signing and receive a reproducible copy of the completed authorization.
Healthcare and legal teams
Aetna operations teams, providers, attorneys, and designated recipients use the authorization to support a specific disclosure request. Staff should verify the recipient and scope before releasing PHI, then retain the authorization and evidence supporting the disclosure.
Teams that handle the release
Aetna plan administrators and health plan operations teams can use a reusable authorization template, assign recipient and signer roles, and route completed releases without repeatedly rebuilding the document. Administrative permissions help limit who can edit, send, or retrieve PHI-related authorizations within the account workforce workflow. Healthcare legal and privacy teams can review the patient’s release scope, delegate sending to authorized staff, and preserve each signed authorization with its completion evidence. Fertility Centers of Illinois is a real signNow healthcare customer, although its published story does not identify this exact Aetna authorization.
Complete the Aetna authorization online
Use this sequence to prepare the exact Aetna release, obtain the patient’s signature, and preserve evidence of completion.
Upload form:
Upload the Aetna authorization PDF. Add fields:
Place fields over required release sections. Add recipient:
Enter the authorized recipient’s email. Send form:
Send the authorization for signature. Complete fields:
Review and sign each required field. Store evidence:
Export the signed form and audit trail.
What the audit trail records
The audit trail connects the Aetna authorization, signer activity, document integrity, and completion evidence in a retrievable record.
Authenticate signer:
Timestamp actions:
Hash document:
Seal record:
Build audit trail:
Retrieve evidence:
 Best ROI. Our customers achieve an average 7x ROI within the first six months.
 Scales with your use cases. From SMBs to mid-market, airSlate SignNow delivers results for businesses of all sizes.
 Intuitive UI and API. Sign and send documents from your apps in minutes.
Recommended authorization setup
Configure the Aetna release workflow around signer identity, PHI protection, audit evidence, and controlled access.
| Setting | Recommendation |
|---|---|
| Authentication method | Email invitation with SMS OTP |
| Signature type | Intent-based electronic signature |
| Audit trail and retention | Export audit evidence for six years |
| Encryption | TLS 1.2/1.3 and AES-256 |
| User provisioning | Role-based access for authorized staff |
Security for PHI workflows
HIPAA protection:
Transport encryption:
Storage encryption:
Security assurance:
Information security:
Electronic signatures:
Find and fill out the correct aetna authorization for release of protected health information phi
airSlate SignNow helps you fill in and sign documents in minutes, error-free. Choose the correct version of the editable PDF form from the list and get started filling it out.
| Versions | Form popularity | Fillable & printable |
|---|---|---|
| Aetna GR-67938 S 2019 | 4.8 Satisfied (1792 Votes) | |
| Aetna GR-67938 S 2003 | 4.8 Satisfied (153 Votes) |
Devices for completing the form
Patients and staff can open the Aetna authorization through supported desktop browsers or signNow mobile applications on iOS and Android. Use an approved, updated browser and a managed device when the document contains protected health information.
Desktop browsers Chrome and Edge on Windows Apple devices Safari on macOS and iOS Android devices Chrome on Android
Healthcare organizations should pair mobile access with role-based account permissions, approved storage, and an appropriate business associate agreement. Test the exact authorization on the selected device before sending, particularly when the workflow uses SMS authentication or requires a patient to review multiple release fields.



Retain and archive the authorization
Preserve the signed Aetna authorization, supporting evidence, and release history under HIPAA and your organization’s records policy.
Apply the six-year HIPAA retention rule
Export the complete audit package
Restrict access to archived records
Validate every release field
Retention periods for release records
Retain each completed Aetna authorization and related evidence for the applicable HIPAA period, then check state and organizational schedules before destruction.
Six years from creation or effective date
Six years for authorization records
Six years for completion evidence
Longer period under state law
Longest applicable period controls
Privacy pitfalls to avoid
Naming a recipient too broadly can disclose PHI to an unintended person or organization instead of the specific recipient identified by the patient. Selecting vague information categories may prevent Aetna or a provider from confirming exactly which records the authorization covers. Missing signature dates, expiration terms, or patient identifiers can delay processing and require a corrected authorization. Sending the completed form through an unapproved channel can expose PHI beyond the intended healthcare or legal workflow.
Aetna authorization troubleshooting
Resolve field, identity, privacy, retention, and plan questions before releasing protected health information through the completed authorization.
Upload the original PDF to signNow, then use the editor to place fields over the patient name, recipient, purpose, information scope, expiration, signature, and date areas. The Business plan includes templates and audit trails; check the source document visually before sending because automated field detection cannot determine whether the authorization is legally complete.
For PHI workflows, signNow lists HIPAA compliance with a business associate agreement requirement. Confirm that the account configuration and BAA cover the intended use before sending the Aetna authorization, and restrict access through account roles rather than sharing the document broadly.
A patient may sign through an email invitation or supported signing link, depending on the workflow. Add SMS or stronger authentication when identity assurance is required. Business Premium adds quick invite links, while Enterprise adds advanced signer authentication capabilities.
A completed authorization should preserve the signed document and its certificate of completion or audit evidence. signNow records actions such as timestamps and signer activity. Export the package after completion and retain it according to the six-year HIPAA rule in 45 CFR 164.530(j), unless a longer rule applies.
The Business plan is listed at $8 per user per month when billed annually and includes audit trails and templates. Paid plans include 100 signature invites per user per year; additional invite charges may apply, so confirm projected volume before sending repeated releases.
Electronic signing can support the Aetna authorization when the patient consents, intends to sign, can access the record, and the completed record remains reproducible under ESIGN and applicable state law. Consumer-facing electronic records may require the disclosures and access procedures in 15 U.S.C. §7001(c).
Key performance indicators that demonstrate SignNow's proven track record.
BE READY TO GET MORE
Get this form now!

If you believe that this page should be taken down, please follow our DMCA take-down process.