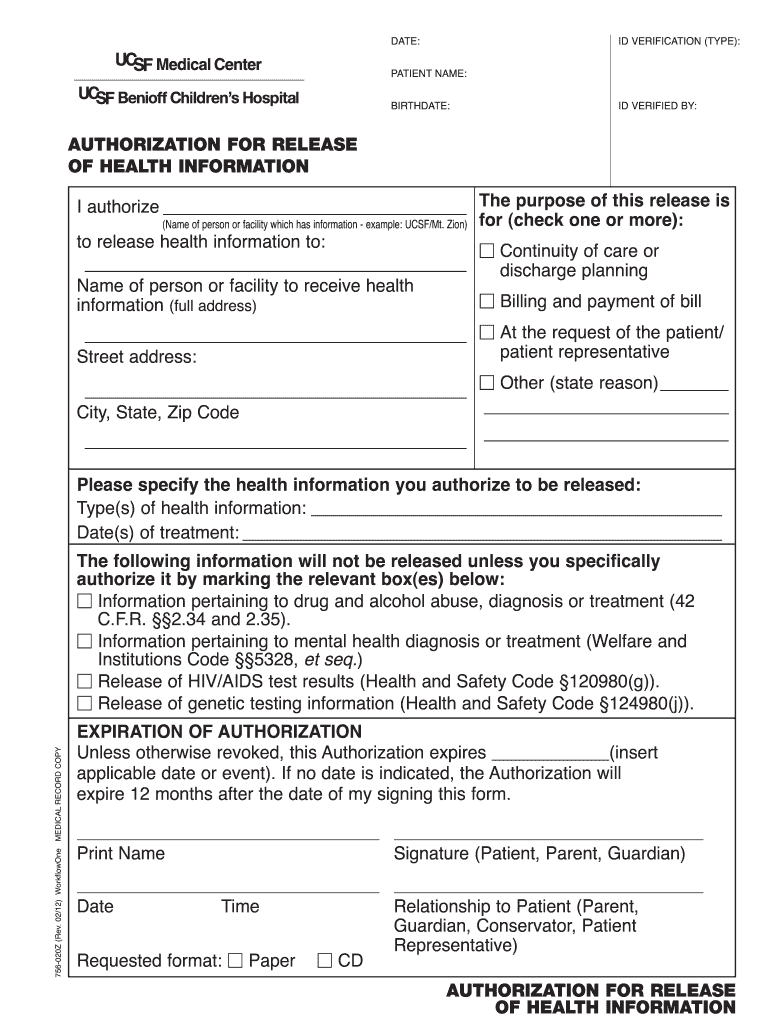
Ucsf Release Of Information
Get the Ucsf Release Of Information 2012 template, fill it out, eSign it, and share it in minutes.
What the Ucsf Release Of Information does
The Ucsf Release Of Information records a patient’s permission to disclose specified health information to an identified recipient. It gives the healthcare organization a documented authorization to review, share, or transmit the records described by the signer. In practice, the form should identify the patient, information covered, recipient, purpose, expiration or revocation terms, and authorized signature. With signNow, the organization uploads the form, places or detects fields, sends it to the appropriate signer, and retains the completed document with its audit trail. HIPAA requirements still govern the underlying disclosure.
Who completes this release form
Healthcare providers
Healthcare providers can use the Ucsf Release Of Information to document a patient’s authorization before sharing specified records with another provider, insurer, attorney, or designated recipient. Staff should identify the patient, requested information, recipient, purpose, expiration terms, and required signatures before sending the form for completion.
Patients and representatives
Patients, authorized representatives, and records departments use the form to define what protected health information may be disclosed and to whom. A completed copy helps recipients understand the authorization’s scope, while the signNow audit trail records the electronic signing events for the organization’s records.
Features for release authorization workflows
signNow brings field preparation, signer routing, audit evidence, mobile access, and protected handling together for the Ucsf Release Of Information workflow.
Field preparation
Upload the Ucsf Release Of Information and prepare its patient, recipient, purpose, and authorization fields without recreating the document manually.
Signer routing
Route the release to a patient or authorized representative by email, helping staff capture the required signature without coordinating a paper handoff.
Audit trail
Maintain a time-stamped record of access, authentication, signing, and document activity connected to the completed authorization.
Mobile signing
Use signNow mobile apps to review and complete the release when approved staff work away from a desktop workstation.
HIPAA workflow
Protect health information with HIPAA compliance and a required business associate agreement for the relevant signNow deployment.
System connections
Connect completed releases with storage or operational systems, reducing manual transfer after the authorization is signed.
Complete the release in signNow
Use this workflow to prepare the Ucsf Release Of Information, capture the required authorization, and preserve evidence of the completed disclosure request.
Upload form:
Upload the Ucsf Release Of Information PDF to signNow. Check fields:
Review detected fields and add patient, recipient, purpose, and signature fields. Assign signer:
Add the patient or authorized representative as the signer. Send request:
Send the authorization through signNow for completion. Store record:
Review the signed release and retain its audit trail.
How the audit trail supports disclosure records
For a Ucsf Release Of Information, the audit trail connects signer activity with the authorization record and supports later review of the disclosure workflow.
Authenticate signer:
Capture timestamps:
Hash document:
Seal record:
Log actions:
Export audit trail:
 Best ROI. Our customers achieve an average 7x ROI within the first six months.
 Scales with your use cases. From SMBs to mid-market, airSlate SignNow delivers results for businesses of all sizes.
 Intuitive UI and API. Sign and send documents from your apps in minutes.
Security controls for health information
HIPAA protection:
Data in transit:
Data at rest:
Security assurance:
Security certification:
Privacy controls:
Platform requirements for release workflows
The Ucsf Release Of Information can be prepared through signNow in Chrome, Firefox, Safari, or Edge on Windows 10 or macOS. SignNow mobile apps support iOS and Android, while TLS 1.2/1.3 protects data in transit during access and signing.
Browsers Chrome, Firefox, Safari, and Edge Operating systems Windows 10, macOS, iOS, Android Secure access TLS 1.2/1.3 and signNow apps
Healthcare organizations should use managed devices, role-based access, and approved signNow accounts when handling protected health information. A HIPAA workflow requires a business associate agreement with signNow, controlled administrator permissions, and documented retention procedures for the completed release and audit trail.
Find and fill out the correct ucsf authorization form
airSlate SignNow helps you fill in and sign documents in minutes, error-free. Choose the correct version of the editable PDF form from the list and get started filling it out.
| Versions | Form popularity | Fillable & printable |
|---|---|---|
| *2012 CA UCSF 756-020Z [2012-02] 2012 | 4.8 Satisfied (2322 Votes) |
Recommended release workflow configuration
Configure the Ucsf Release Of Information workflow around signer identity, authorization evidence, protected transmission, and a documented healthcare retention policy.
| Setting | Recommendation |
|---|---|
| Authentication method | Email authentication with SMS OTP |
| Signature type | Typed or drawn electronic signature |
| Audit trail | Retain completion certificate and activity log |
| Document retention | 6 years (HIPAA 45 CFR 164.530(j)) |
| Encryption | TLS 1.2/1.3 and AES-256 encryption |



Privacy and disclosure pitfalls
Including an entire medical record when the authorization should identify only specific information can create unnecessary disclosure exposure. Leaving the recipient, purpose, expiration date, or revocation instructions unclear can make the authorization difficult to interpret and administer. Sending the form through an account with excessive permissions can expose protected health information to unauthorized staff or recipients. Failing to retain the signed authorization and audit trail can weaken the organization’s ability to demonstrate how consent was captured.
Best practices for signed release records
Use precise authorization language, preserve signing evidence, and align storage practices with HIPAA and the organization’s records policy.
Limit the authorization to necessary information
Preserve the signed release and audit evidence
Apply the HIPAA six-year retention rule
Control access after the signature
Healthcare release workflow examples
Healthcare organizations can adapt signNow’s signing, API, and audit capabilities to the authorization and disclosure controls required for this release form.
Healthcare provider
Fertility Centers of Illinois selected airSlate SignNow for a healthcare signing workflow involving sensitive patient documentation and API-connected processes.
- Healthcare authorization workflow
John Butler, founder of Fertility Centers of Illinois, said the organization valued the SignNow team, API, and responsiveness. The customer story supports using a connected signing workflow for healthcare documents, while each organization must separately configure HIPAA safeguards, access controls, and a business associate agreement where required.
Records department
A healthcare records department can use signNow to route a patient authorization, capture the signature, and preserve the completed release with its activity history.
- Patient disclosure authorization
The workflow reduces paper handling without changing the authorization’s substantive requirements. Staff still need to verify the patient, recipient, purpose, information scope, expiration terms, and signer authority, then store the signed document and audit trail under the organization’s HIPAA records policy.
Troubleshooting the release workflow
Resolve field, signer, compliance, evidence, scope, and retention questions before relying on a completed Ucsf Release Of Information.
Upload the original Ucsf Release Of Information PDF again, then inspect detected fields before sending. signNow’s Business plan includes templates and audit trails, but staff must verify that every patient, recipient, purpose, and signature field matches the source document.
Check the signer’s email address, resend the invitation, or provide an approved signing link. If stronger identity evidence is required, configure available authentication options and document the organization’s decision under its HIPAA workflow.
A signNow Business plan is listed at $8 per user per month with annual billing and includes audit trails. HIPAA use requires a business associate agreement, so confirm the applicable account and contractual setup before transmitting PHI.
Use the completed release together with its signNow audit trail, which records signing activity and timestamps. Under ESIGN and UETA, electronic records can support enforceability when intent, consent, attribution, and retention requirements are satisfied.
Do not use the authorization to disclose information outside its stated scope. Review the patient, recipient, purpose, information category, and expiration terms; then obtain a corrected release when a required element is incomplete or ambiguous.
HIPAA requires covered entities to retain documentation for 6 years from creation or the last effective date under 45 CFR §164.530(j). Apply that rule to relevant release documentation unless a longer state or organizational requirement controls.
Key performance indicators that demonstrate SignNow's proven track record.
BE READY TO GET MORE
Get this form now!

If you believe that this page should be taken down, please follow our DMCA take-down process.