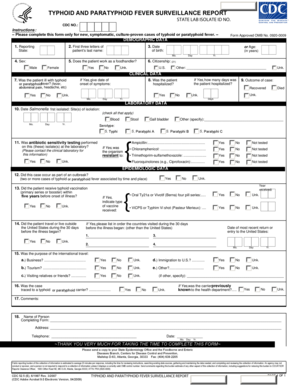
Typhoid Fever Surveillance Report Typhoid Fever Surveillance Report Health Mo
Use a Typhoid Fever Surveillance Report Typhoid Fever Surveillance Report Health Mo 2009 template to make your document workflow more streamlined.
What this typhoid surveillance report does
This Typhoid Fever Surveillance Report is a public-health record used to document and communicate information about a suspected or confirmed typhoid fever case. The supplied form name does not identify a state, issuing agency, field list, or filing deadline, so those details must be confirmed with the responsible health department. In signNow, a sender can upload the report, review detected fillable fields, assign signature or date fields, send it to authorized recipients, and retain the completed document with its audit trail. Do not treat signNow as the filing authority.
Organizations that use this report
The report is most useful where public-health information must move between clinical, laboratory, and administrative teams with accountable review.
County health departments can standardize report preparation, route signatures to authorized officials, and maintain a searchable signed record for outbreak-response files. Clinical laboratories can attach supporting results, send the named report for review, and preserve the completed document without repeatedly exchanging paper copies. Multi-site healthcare systems can use shared templates, delegated sending, and role-based access to coordinate surveillance reporting across facilities while limiting exposure of patient information.
These tasks are executed by both individual contributors and centralized administrators depending on organizational policy and required controls.
How the report workflow works
Use this sequence to prepare the named surveillance report without confusing document completion with official public-health filing.
Upload report: Upload the current Typhoid Fever Surveillance Report PDF to signNow. Prepare fields: Review detected fields and add required signature, date, and text fields. Route securely: Send the report to the authorized reviewer or signer. Store evidence: Download the completed report and audit trail for controlled filing.
Quick steps for this report
Prepare the named surveillance report in signNow, then preserve the signed record separately from the agency’s filing instructions.
Upload report:
Upload the current report PDF. Check fields:
Review detected fields and source data. Add signer:
Assign the authorized signer. Complete record:
Send, sign, and download the audit trail.
What the audit trail records
The audit trail documents evidence around the named report after preparation; it is distinct from completing the report’s substantive health information.
Authenticate signer:
Timestamp actions:
Hash document:
Seal completion:
Log activity:
Export evidence:
 Best ROI. Our customers achieve an average 7x ROI within the first six months.
 Scales with your use cases. From SMBs to mid-market, airSlate SignNow delivers results for businesses of all sizes.
 Intuitive UI and API. Sign and send documents from your apps in minutes.
Features for completing this report
signNow organizes the named surveillance report from upload through signature while keeping completion evidence available for the responsible records process.
Document upload
Upload the current surveillance-report PDF and keep the source file attached to the controlled workflow for review.
Field review
Review automatically detected fields before adding missing patient, reporter, date, or signature fields.
Signer routing
Route the report to an authorized signer without creating uncontrolled email copies.
Audit evidence
Capture signer actions, timestamps, and completion evidence in an audit trail.
PHI safeguards
Protect health information with encryption and a HIPAA arrangement when applicable.
Controlled archive
Download the signed report and completion evidence for agency-directed recordkeeping.
Best practices for this report
Accurate routing, controlled access, and documented retention help preserve this surveillance record without inventing deadlines or agency requirements.
Confirm agency and jurisdiction before sending
Validate identifiers and supporting information carefully
Export evidence and restrict access to authorized reviewers
Apply the governing retention rule to records
Retention rules for related records
Keep the signed report and attachments according to the rule governing the underlying record, because no single retention period is supplied for this form name.
Public-health record period
Six years for PHI
Three years for tax records
Later of two employment dates
State rule may extend
Find and fill out the correct typhoid fever surveillance report typhoid fever surveillance report health mo
airSlate SignNow helps you fill in and sign documents in minutes, error-free. Choose the correct version of the editable PDF form from the list and get started filling it out.
| Versions | Form popularity | Fillable & printable |
|---|---|---|
| HHS CDC 52.5 (E) 2012 | 4.8 Satisfied (1533 Votes) | |
| HHS CDC 52.5 (E) 2009 | 4.8 Satisfied (1226 Votes) |
Privacy and disclosure pitfalls
The report may expose patient identifiers or clinical details when sent to unintended recipients or stored without role-based access controls. A missing consent or signature event can make the submitted surveillance record difficult to authenticate during administrative review. Uploading the wrong patient or laboratory attachment can connect sensitive information to the wrong report. Uncontrolled copies in email, downloads, or shared drives can undermine the report’s confidentiality after signing.
Recommended report workflow setup
Configure the report around controlled access, attributable signatures, and the retention rule governing the underlying public-health record.
| Setting | Recommendation |
|---|---|
| Authentication method | Email link with SMS OTP |
| Signature type | Typed or drawn electronic signature |
| Audit trail | Enable completion certificate and action log |
| Document retention | Six years when HIPAA applies |
| Encryption | TLS 1.2/1.3 and AES-256 |
Security for the surveillance report
Transport encryption:
Storage encryption:
Health information:
Control assurance:
Security standard:
Signing evidence:
Legal standing of the completed report
An electronic signature may be legally effective under the federal ESIGN Act, 15 U.S.C. ch. 96, and applicable state law when intent, consent, attribution, and record reproduction are established. Acceptance, filing method, and any public-health exclusions remain controlled by the responsible agency and state requirements.



Questions about completing this report
These answers separate the signNow workflow from filing rules that must come from the responsible public-health authority.
The form name does not identify the receiving agency or deadline, so signNow cannot determine filing requirements. Confirm the jurisdiction’s instructions, then use signNow to complete and route the document; the platform does not replace submission to a health department.
Upload the current PDF, review signNow’s detected fields, and compare each field with the source record. Detection is an editing aid, not a validation of typhoid-specific requirements, so manually confirm all patient, laboratory, reporter, and jurisdiction information.
Use assigned signature fields and require the responsible official to review before signing. signNow captures signer actions, timestamps, and an audit trail, but the receiving agency may impose additional authentication or wet-signature rules.
If the report contains protected health information, signNow states that HIPAA compliance requires a business associate agreement. Configure the appropriate arrangement before sending, and restrict recipients and document access to authorized personnel.
The Business plan is listed at $8 per user per month when billed annually and includes audit trails and templates. It does not establish the report’s legal deadline or agency acceptance, which remain matters for the responsible authority.
After completion, download the signed report and audit trail, then archive them under the governing public-health, HIPAA, or state rule. HIPAA’s six-year period applies to covered records under 45 CFR 164.530(j), not automatically to every report.
Risks from improper handling
Wrong jurisdiction
Missing required field
Unauthorized recipient
Audit trail omitted
Key performance indicators that demonstrate SignNow's proven track record.
BE READY TO GET MORE
Get this form now!

If you believe that this page should be taken down, please follow our DMCA take-down process.