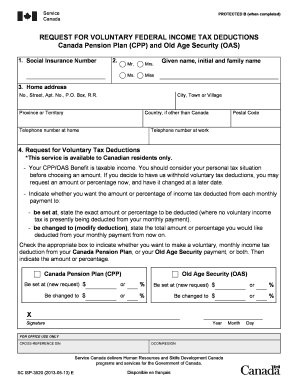
Isp 3520 (2013)
Use a Isp 3520 2013 template to make your document workflow more streamlined.
What Isp 3520 (2013) is
Isp 3520 (2013) is the document identified by that exact title and edition year; its governing instructions and required fields should control how it is completed. signNow can convert the supplied file into an electronic workflow by uploading the document, detecting or adding fillable fields, assigning recipients, collecting signatures, and retaining the signed PDF with an audit trail. Because the available record does not identify an issuing agency, filing deadline, tax treatment, or form-specific statutory rule, confirm those details from the original instructions before submission.
Who completes Isp 3520 (2013)
Business teams
Use Isp 3520 (2013) when your workflow requires the named document to be completed, reviewed, and signed by identified parties. Confirm the form’s instructions before adding supplemental contracts, NDAs, HR forms, invoices, or consent forms.
Authorized filers
Administrative, legal, finance, and operations staff can prepare Isp 3520 (2013) for the parties identified in the document instructions, while preserving the completed record and signing history.
How Isp 3520 (2013) works online
The signNow workflow moves Isp 3520 (2013) from an uploaded file to an assigned, signed, and auditable electronic record.
Upload document: Upload the Isp 3520 (2013) PDF into signNow. Prepare fields: Review detected fields and add signature, date, or text fields. Assign signers: Assign each field to the appropriate Isp 3520 recipient. Complete record: Send, complete, and store the signed document with its audit trail.
Quick steps for Isp 3520 (2013)
Prepare Isp 3520 (2013) in signNow by checking its fields, assigning recipients, collecting signatures, and preserving the completed record.
Upload form:
Upload the completed Isp 3520 file. Check fields:
Review and correct detected fields. Add recipients:
Assign signers and signing order. Send request:
Send the form through signNow. Store evidence:
Download the signed record and audit trail.
 Best ROI. Our customers achieve an average 7x ROI within the first six months.
 Scales with your use cases. From SMBs to mid-market, airSlate SignNow delivers results for businesses of all sizes.
 Intuitive UI and API. Sign and send documents from your apps in minutes.
How the Isp 3520 (2013) audit trail works
The audit trail records who handled Isp 3520 (2013), what they did, and when each signing event occurred.
Authenticate signer:
Capture timestamp:
Hash document:
Seal record:
Log activity:
Export evidence:
Recommended Isp 3520 workflow setup
Configure Isp 3520 (2013) around signer identity, document integrity, audit evidence, and the retention policy applicable to the underlying transaction.
| Setting | Recommendation |
|---|---|
| Authentication method | Email verification with SMS OTP |
| Signature type | Electronic signature with completion certificate |
| Audit trail | Enable detailed audit trail |
| Document retention | Retain signed record by policy |
| Encryption | TLS 1.2/1.3 and AES-256 |
Find and fill out the correct isp 3520 100374965
airSlate SignNow helps you fill in and sign documents in minutes, error-free. Choose the correct version of the editable PDF form from the list and get started filling it out.
| Versions | Form popularity | Fillable & printable |
|---|---|---|
| Canada SC ISP-3520 E 2016 | 4.8 Satisfied (4715 Votes) | |
| Canada SC ISP-3520 E 2013 | 4.8 Satisfied (2525 Votes) | |
| Canada SC ISP-3520 E 2011 | 4.8 Satisfied (1057 Votes) |
Platform requirements for Isp 3520
Use signNow through Chrome, Firefox, Safari, or Edge on Windows or macOS. signNow also provides mobile apps for iOS and Android, allowing authorized users to review and sign Isp 3520 (2013) from supported devices.
Browser support Chrome, Firefox, Safari, and Edge Desktop systems Windows and macOS desktop access Mobile access iOS and Android mobile apps
Organizations should manage access through approved devices, user permissions, and retention policies. Enterprise deployments may also evaluate API access, SSO provisioning, and stronger authentication according to the sensitivity of Isp 3520 (2013) and the organization’s regulatory obligations.
Security for Isp 3520 (2013)
Data in transit:
Data at rest:
Independent controls:
Security management:
Electronic signatures:
Health information:
Legal standing of Isp 3520 (2013)
An electronically signed Isp 3520 (2013) may be admissible when the signer demonstrates intent, consents to electronic records, can be identified, and the record remains reproducible. ESIGN, 15 U.S.C. ch. 96, and applicable UETA provisions support electronic records, but exclusions such as wills and certain court filings still apply.

Risks when Isp 3520 is incomplete
Intent evidence
Incomplete execution
Weak attribution
Record integrity
Challenges when completing Isp 3520
A scanned Isp 3520 (2013) may lack reliable field boundaries, requiring manual placement and recipient assignment before sending. Leaving a required signer, date, or acknowledgment field unassigned can produce an incomplete electronic record. Using an email address without additional verification may provide less identity assurance than the transaction requires. Saving only the signed PDF without its audit trail can weaken evidence about timing, attribution, and completion.
Troubleshooting Isp 3520 (2013)
Use these targeted checks to resolve preparation, signer-authentication, retention, and electronic-consent questions for Isp 3520 (2013).
Upload the original Isp 3520 (2013) file again and use signNow’s field editor to place required fields manually. The Business plan includes templates and audit trails, but automated field recognition may require review when a PDF has unusual formatting.
Check that every required Isp 3520 (2013) field has an assigned recipient and that signer email addresses are accurate. signNow’s role-based routing and completion tracking help identify the unassigned field before sending.
Use signNow’s SMS authentication or another available signer-verification control when identity assurance is needed. ESIGN and UETA focus on intent, consent, attribution, and record retention; the selected authentication method should match your risk assessment.
The Business plan is listed at $8 per user per month with annual billing and includes 100 signature invites per user annually. Review the account’s plan terms and overage rules before sending high-volume Isp 3520 workflows.
A completed Isp 3520 (2013) can be retained with its certificate of completion and audit trail in signNow. Choose a retention period based on the document’s actual legal or business purpose, because no universal Isp-specific period is established here.
For consumer-facing electronic records, provide the ESIGN disclosure, confirm electronic access, and explain withdrawal procedures under 15 U.S.C. §7001(c). signNow can document the signing event, but your organization remains responsible for legally required notices.
Key performance indicators that demonstrate SignNow's proven track record.
BE READY TO GET MORE
Get this form now!

If you believe that this page should be taken down, please follow our DMCA take-down process.