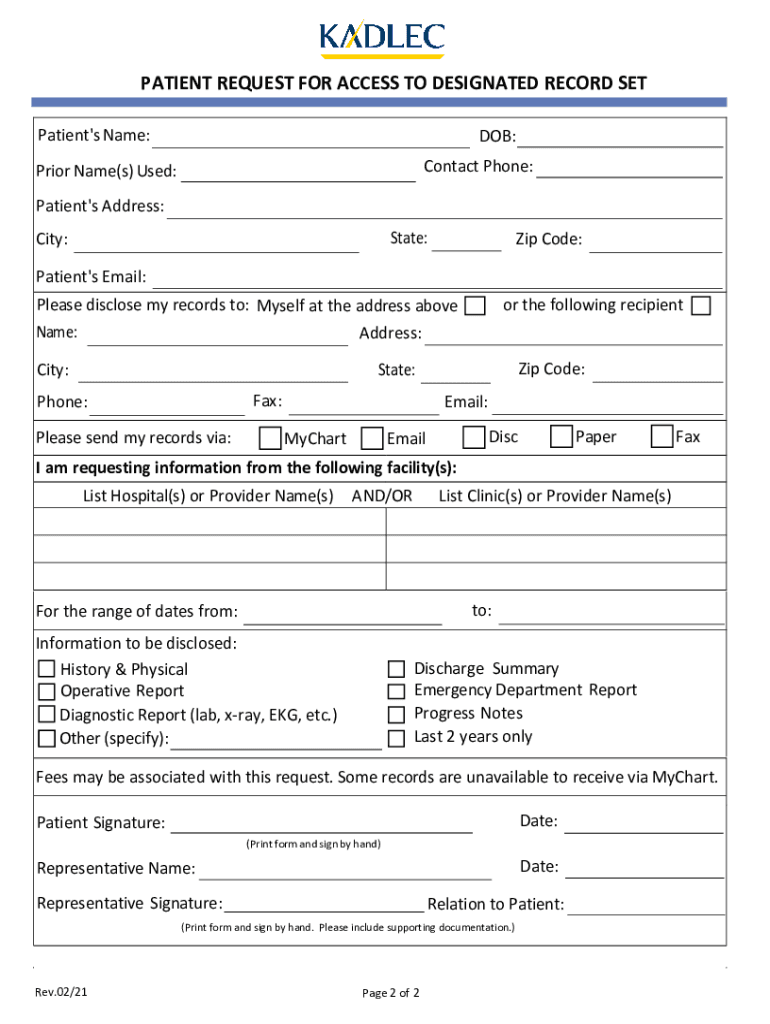
Patient Request For Access To Designated Record Set Kadlec
Use a PATIENT REQUEST FOR ACCESS TO DESIGNATED RECORD SET Kadlec 2021 template to make your document workflow more streamlined.
What the Kadlec patient access request does
The Patient Request For Access To Designated Record Set Kadlec is a healthcare privacy form used to request access to a patient’s designated record set. A patient or authorized representative completes the identifying information, requested-record details, delivery preference, and signature, then Kadlec reviews the request under its health-information process. With signNow, staff can upload the form, auto-detect fillable fields, send it for signature, and retain the completed PDF with an audit trail. HIPAA’s documentation rule generally requires six-year retention under 45 CFR 164.530(j).
Who uses the Kadlec access request
Patients and representatives
Patients use the Kadlec request to ask for access to their designated record set, while authorized personal representatives provide supporting authority when required. The completed form can identify the requested records, delivery preference, patient details, and signature needed for Kadlec’s review.
Kadlec health-information teams
Kadlec health-information staff use the signed request to verify identity, evaluate authorization, locate designated-record-set materials, and document the response. Healthcare administrators can route the request through signNow while preserving the completed form and audit trail for HIPAA recordkeeping.
Organizations that use Kadlec requests
Patient access workflows range from one-person practices to hospital systems, with controls scaled to the request volume and protected health information involved.
A solo healthcare practitioner can send a patient’s Kadlec access request for signature, keep the completed PDF with its audit trail, and coordinate fulfillment without printing or scanning the form. A regional clinic can standardize patient and representative requests through reusable signNow templates, controlled recipients, and role-based review before releasing designated-record-set materials. A hospital enterprise can connect request routing with Microsoft 365, Google Drive, or enterprise workflows while maintaining HIPAA safeguards, documented retention, and administrator oversight.
These tasks are executed by both individual contributors and centralized administrators depending on organizational policy and required controls.
How Kadlec access requests move online
The signNow workflow converts the Kadlec request into a controlled digital record without changing the patient-access purpose of the form.
Upload form: Upload the Kadlec patient access request PDF. Review fields: Auto-detect fillable fields, then confirm patient and representative details. Send request: Send the request to the patient or authorized representative. Store evidence: Collect the signature and store the completed record with its audit trail.
How the audit trail records access requests
signNow records the evidence surrounding this patient request, helping Kadlec review who acted, what changed, and when each event occurred.
Authenticate signer:
Capture timestamps:
Hash document:
Seal evidence:
Bind signer activity:
Export audit trail:
 Best ROI. Our customers achieve an average 7x ROI within the first six months.
 Scales with your use cases. From SMBs to mid-market, airSlate SignNow delivers results for businesses of all sizes.
 Intuitive UI and API. Sign and send documents from your apps in minutes.
Features for Kadlec access requests
signNow combines field preparation, controlled delivery, signer verification, and audit evidence for the specific patient-access request workflow.
Field detection
Upload the Kadlec PDF and confirm detected patient, representative, date, and signature fields before sending it for completion.
Secure routing
Route the request to the patient or authorized representative by email or a controlled signing link, reducing manual handoffs.
Audit trail
Capture signatures, timestamps, signer activity, and completion evidence in one record for health-information staff review.
Signer verification
Use two-factor authentication or SMS OTP when Kadlec policy requires stronger confirmation of the signer’s identity.
Record control
Keep the completed request and audit evidence together, supporting HIPAA documentation and later access-review questions.
Mobile completion
Complete the request from a desktop or mobile device while preserving the same signed-document workflow.
Security controls for patient requests
Compliance framework:
Security reporting:
Information security:
Stored data:
Data in transit:
Healthcare deployment:
Find and fill out the correct patient request for access to designated record set kadlec
airSlate SignNow helps you fill in and sign documents in minutes, error-free. Choose the correct version of the editable PDF form from the list and get started filling it out.
| Versions | Form popularity | Fillable & printable |
|---|---|---|
| Kadlec Patient Request to Access/Disclose a Designated Record Set - Clinic 2021 | 4.8 Satisfied (1959 Votes) | |
| Kadlec Patient Request to Access/Disclose a Designated Record Set - Clinic 2017 | 4.7 Satisfied (343 Votes) |



Recommended Kadlec request setup
Configure the request around patient identity, protected health information, signer evidence, and the applicable HIPAA documentation period.
| Kadlec workflow setting | Recommended configuration |
|---|---|
| Authentication method | Two-factor authentication for PHI |
| Signature type | Intent-based electronic signature |
| Audit trail | Export with completed request |
| Document retention | 6 years under HIPAA 45 CFR 164.530(j) |
| Encryption | AES-256 at rest and TLS 1.2/1.3 |
Patient request record retention periods
Keep the completed request, authorization evidence, access response, and audit history together for the applicable retention period.
6 years from creation or last effective date
6 years for disclosure accounting records
6 years for business associate records
At least six years for patient records
Longer state period when applicable
Record-keeping practices for Kadlec requests
Accurate retention and controlled disclosure matter because this request connects a patient identity to protected health information and access activity.
Keep the request and response together
Export audit evidence after completion
Limit access to protected health information
Document the controlling retention rule
Privacy pitfalls in Kadlec requests
Sending a signed Kadlec request to an incorrect address can expose patient identifiers or requested-record details beyond the intended recipient. A patient representative may sign without attaching or documenting authority, leaving Kadlec unable to confirm the requested disclosure. Using a general template can omit the requested record scope, delivery preference, or signature date required for review. Retaining the signed request without its audit trail can weaken evidence of who signed and when the access workflow occurred.
Rules that can affect this request
Signature validity
Access review delay
Unauthorized disclosure
Longer retention required
Troubleshooting Kadlec access requests
Use these answers to resolve field, authentication, privacy, and plan questions before completing a Kadlec patient access request.
Use signNow’s field editor to confirm every patient, representative, date, and authorization field before sending. Auto-detection accelerates setup, but Kadlec should review placement against the original request because signNow does not determine whether a person legally qualifies for access.
HIPAA compliance requires a business associate agreement when signNow handles protected health information for a covered entity. The signNow compliance record identifies HIPAA compliance as requiring a BAA; confirm the agreement and organizational safeguards before routing this request.
Business includes legally binding eSignatures, audit trails, templates, and mobile apps at $8/user/month billed annually. Its verified plan details do not include bulk send; Business Premium adds bulk send at $15/user/month annually.
Use two-factor authentication or SMS one-time passwords when the request contains protected health information or representative details. Stronger authentication supports attribution, but staff must still verify identity and authority under Kadlec’s access procedure.
Electronic signing can satisfy ESIGN and applicable UETA requirements when intent, consent, attribution, and record reproduction are established. Consumer-facing electronic records may also require the disclosures and access procedures in 15 U.S.C. §7001(c).
Do not send the completed request to an unverified email address. Correct the recipient, review access permissions, and preserve the corrected audit history; HIPAA safeguards remain the responsibility of the covered entity, not the signing platform alone.
Key performance indicators that demonstrate SignNow's proven track record.
BE READY TO GET MORE
Get this form now!

If you believe that this page should be taken down, please follow our DMCA take-down process.