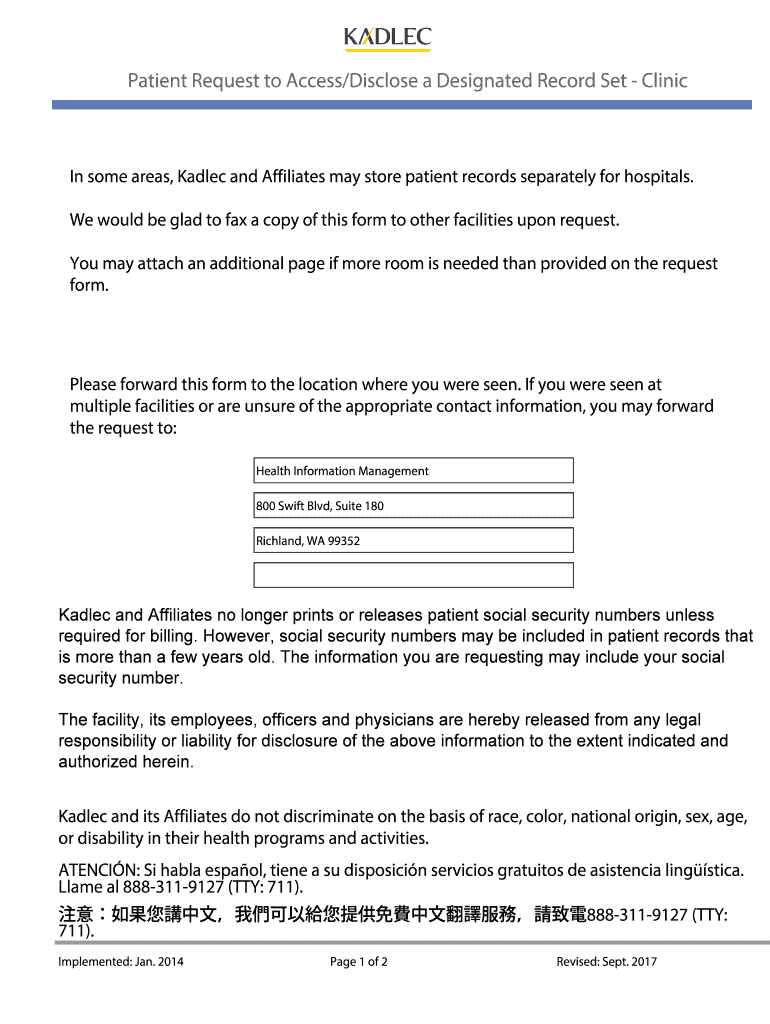
Patient Request To Accessdisclose A Designated Record Set
Use a Patient Request To AccessDisclose A Designated Record Set 2017 template to make your document workflow more streamlined.
What this patient request does
A Patient Request To Accessdisclose A Designated Record Set is a written request for access to, or disclosure of, a patient’s designated record set. The patient or authorized representative identifies the records, recipient, purpose, and preferred delivery method, then signs the request. A covered entity reviews identity, authorization, and applicable HIPAA procedures before responding. signNow can capture the electronic signature, consent, timestamps, and audit trail, but it does not decide whether disclosure is legally permitted or replace the provider’s privacy review.
Who uses this patient request
Patients and representatives
Patients or authorized representatives use the form to identify designated-record-set information, define the requested disclosure, and sign the authorization evidence required by the provider’s HIPAA process.
Healthcare organizations
Medical practices, health plans, and health information departments use the signed request to route review, document authorization, and preserve the final disclosure record with controlled access.
Features for patient request workflows
signNow provides document preparation, signer routing, authentication, audit evidence, and storage controls that can be configured around this patient access and disclosure request.
Field detection
Upload the Patient Request To Accessdisclose A Designated Record Set and review detected fields before sending, reducing manual setup for patient, representative, recipient, and authorization details.
Role-based routing
Assign signing roles to the patient or authorized representative and route the request through a defined sequence before disclosure review begins.
Audit trail
Capture electronic intent, signer actions, timestamps, and completion evidence in an audit trail associated with the signed request.
Signer authentication
Use SMS authentication or other configured controls when the organization requires stronger evidence that the intended person accessed the request.
Secure storage
Preserve the signed request and completion certificate in an approved repository with access restrictions appropriate for protected health information.
System integration
Connect signNow with healthcare-adjacent systems or cloud repositories to reduce rekeying while keeping the completed request available for authorized staff.
How the patient request moves forward
The signNow workflow turns the Patient Request To Accessdisclose A Designated Record Set into a controlled sequence from preparation through signed-record preservation.
Prepare: Upload the patient request and review its detected fields. Assign: Assign patient, representative, or covered-entity signing roles. Deliver: Send the request and capture consent to electronic records. Preserve: Complete the signature and retain the audit trail.
Complete the patient request in signNow
Use this sequence to prepare the request, obtain the required signature, and preserve evidence of the completed Patient Request To Accessdisclose A Designated Record Set.
Upload the form:
Upload the completed Patient Request To Accessdisclose A Designated Record Set. Check the fields:
Review detected fields and add missing patient or authorization fields. Assign the signer:
Add the patient or authorized representative as the signer. Send for signature:
Send the request through signNow for electronic completion. Archive the record:
Store the signed copy and audit trail in the approved repository.
 Best ROI. Our customers achieve an average 7x ROI within the first six months.
 Scales with your use cases. From SMBs to mid-market, airSlate SignNow delivers results for businesses of all sizes.
 Intuitive UI and API. Sign and send documents from your apps in minutes.
Recommended request workflow settings
Configure the request around patient identity, authorization evidence, protected health information, and a reproducible record of every signing action.
| Setting | Recommendation |
|---|---|
| Authentication method | Email verification with SMS OTP |
| Signature type | Intent-based electronic signature |
| Audit trail | Detailed completion certificate and action log |
| Document retention | Six years for HIPAA records (45 CFR 164.530(j)) |
| Encryption | TLS 1.2/1.3 and AES-256 encryption |
How the request audit trail is created
signNow records the evidence surrounding each patient request so an administrator can review identity, timing, document integrity, and completion history.
Signer authentication:
Timestamp capture:
Document association:
Tamper-evident sealing:
Action history:
Audit export:
Find and fill out the correct patient request to accessdisclose a designated record set
airSlate SignNow helps you fill in and sign documents in minutes, error-free. Choose the correct version of the editable PDF form from the list and get started filling it out.
| Versions | Form popularity | Fillable & printable |
|---|---|---|
| Kadlec Patient Request to Access/Disclose a Designated Record Set - Clinic 2021 | 4.8 Satisfied (1959 Votes) | |
| Kadlec Patient Request to Access/Disclose a Designated Record Set - Clinic 2017 | 4.7 Satisfied (343 Votes) |
Security controls for patient records
HIPAA:
TLS 1.2/1.3:
AES-256:
SOC 2 Type II:
ISO 27001:
BAA required:
Privacy pitfalls to address
Sending the request to an unverified email address can expose protected health information or deliver records to the wrong person. An incomplete authorization may omit the requested record scope, recipient, purpose, expiration, or required patient signature. Broad user permissions can allow staff without a treatment, payment, operations, or privacy role to access the signed request. Failing to preserve the audit trail can make it harder to establish consent, signer identity, timing, and document integrity.
Record-keeping practices for patient requests
Accurate retention and controlled archival help demonstrate what the patient requested, what was disclosed, and how the signed record was preserved.
Preserve the complete request record
Export audit evidence with every copy
Archive protected health information securely
Coordinate deletion with legal holds
Retention periods for signed records
Retain the completed request, authorization evidence, and audit trail according to the record category and controlling federal rule.
Six years for HIPAA records
Three years for tax records
Later of three years or one
Three years for payroll records
Five years for OSHA records



Troubleshooting patient request workflows
Use these answers to resolve setup, access, authentication, compliance, and plan questions without bypassing the healthcare organization’s privacy review.
Business includes audit trails, templates, mobile apps, and legally binding eSignatures. If the request requires bulk send, kiosk mode, or advanced authentication, review Business Premium or Enterprise features before assigning the workflow.
signNow is HIPAA compliant, but the product-side ground truth specifies that a business associate agreement is required. Have the covered entity or business associate complete the BAA and confirm permitted uses before processing protected health information.
If the patient cannot access the request, verify the email address, resend the invitation, and check whether the organization requires SMS authentication. Do not send protected health information through an unapproved channel while troubleshooting delivery.
Review the detected fields after upload and add any missing authorization, scope, recipient, purpose, expiration, or signature fields. signNow prepares the document workflow, but the healthcare organization remains responsible for legal completeness.
A completed signature does not itself authorize every disclosure. The covered entity must still apply HIPAA privacy procedures, verify identity and authority, and determine whether the designated record set may be accessed or disclosed.
Business costs $8 per user per month with annual billing, while Business Premium costs $15 and Enterprise costs $30. All paid plans include 100 signature invites per user per year; verify overage terms before high-volume deployment.
Key performance indicators that demonstrate SignNow's proven track record.
BE READY TO GET MORE
Get this form now!

If you believe that this page should be taken down, please follow our DMCA take-down process.