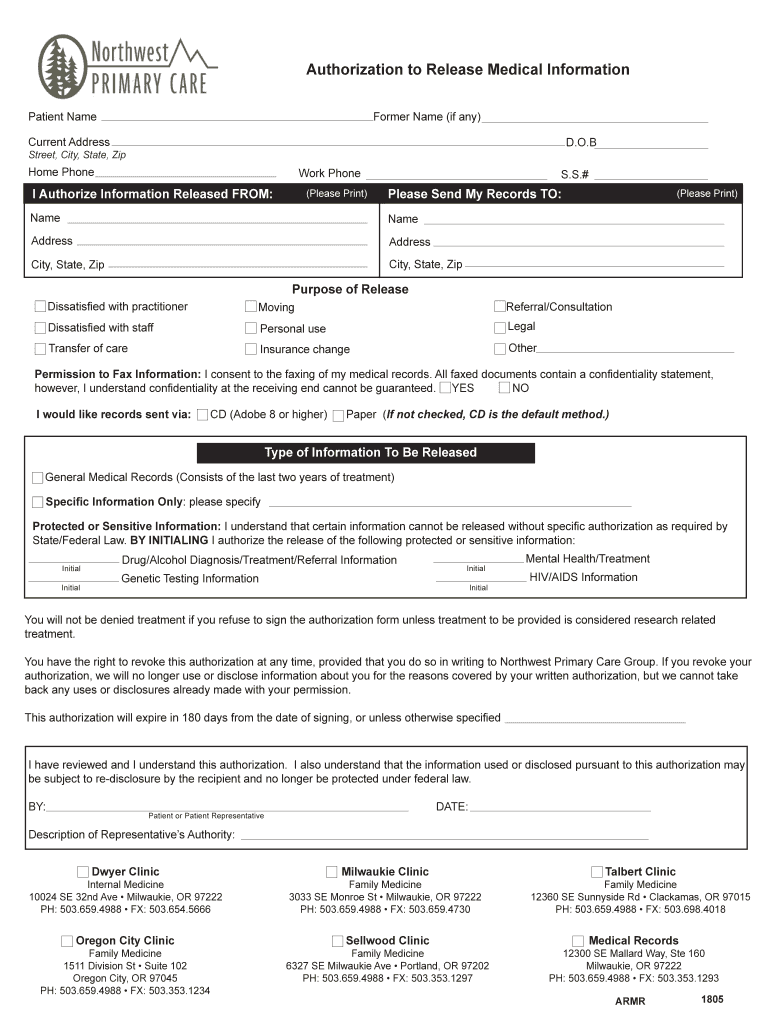
Authorization To Release Medical Record Information Brown
Use a Authorization To Release Medical Record Information Brown 2015 template to make your document workflow more streamlined.
What this medical release authorization does
Authorization To Release Medical Record Information Brown is a written permission form that allows a healthcare provider or records custodian to disclose specified medical information to an identified recipient. The signer generally identifies the patient, records or information covered, recipient, purpose, expiration or revocation terms, and signature date. In signNow, the organization uploads the Brown form, places fields over its existing content, sends it to the authorized signer, and stores the completed copy with an audit trail. HIPAA authorization requirements under 45 CFR 164.508 still govern the disclosure.
Teams that manage the Brown authorization
A health information management administrator can approve the Brown authorization template, control who may send it, and preserve a consistent release workflow across locations. Shared templates reduce unauthorized edits while delegated sending lets approved staff initiate patient-specific requests without changing the underlying form design. A medical practice or hospital privacy team can assign role-based access for staff handling protected health information. signNow user administration, templates, and audit trails help separate template approval, sending, signing, and record-retrieval responsibilities for Authorization To Release Medical Record Information Brown.
Features for medical release authorizations
Authorization To Release Medical Record Information Brown benefits from controlled fields, verified signing, documented consent, and secure handling of the completed authorization.
Field placement
Upload the Brown medical-record authorization, then use signNow’s field tools to place patient, recipient, purpose, date, and signature fields where the document requires completion.
Signer routing
Send the authorization directly to the patient or representative and any required recipient, preserving signing order when multiple parties must review the release.
Consent evidence
Capture consent and signatures electronically while retaining the completed authorization and signing history for healthcare recordkeeping and later review.
Signer verification
Use SMS-based authentication or other available controls when the organization needs stronger assurance that the intended patient or representative accessed the release.
Audit trail
Store the signed authorization with its audit trail so staff can connect the release decision, signer activity, timestamps, and final document in one workflow.
Reusable template
Reuse an approved Brown authorization template after legal or compliance review, reducing rekeying while preserving the form’s defined release scope.
How the Brown form moves through signNow
Use the Brown authorization’s existing release scope as the source of truth, then complete and document each signing event in signNow.
Upload form: Upload the Brown authorization and inspect its existing patient, recipient, scope, and signature areas. Map fields: Place signNow fields over the Brown form without changing its substantive release language. Request signature: Send the authorization to the patient or representative for consent and signature. Preserve evidence: Download or store the signed authorization with its audit trail for disclosure review.
Quick steps for completing the form
Follow the Brown authorization’s release scope, identify each required signer, and retain evidence of consent before disclosure.
Prepare form:
Upload the approved Brown authorization PDF. Add fields:
Place fields over required patient and release sections. Assign signer:
Assign the patient or representative as signer. Complete record:
Review, sign, and retain the completed authorization.
 Best ROI. Our customers achieve an average 7x ROI within the first six months.
 Scales with your use cases. From SMBs to mid-market, airSlate SignNow delivers results for businesses of all sizes.
 Intuitive UI and API. Sign and send documents from your apps in minutes.
Security for protected health information
HIPAA safeguards:
Security certification:
Information security:
Transport encryption:
Storage encryption:
Privacy controls:
Platform requirements for signing
Authorization To Release Medical Record Information Brown can be completed in signNow through Chrome, Firefox, Safari, or Edge on Windows and macOS. signNow also provides mobile apps for iOS and Android, allowing authorized users to review and sign from supported mobile devices.
Desktop browsers Chrome, Firefox, Safari, Edge Operating systems Windows, macOS, iOS, Android Supported devices Desktop and mobile signing
Healthcare organizations should use managed Windows, macOS, iOS, or Android devices with current security updates. Administrators can also evaluate API access, SSO provisioning, and certificate or long-term validation requirements before deploying this medical-record authorization workflow across departments or external recipients.



Find and fill out the correct authorization to release medical record information brown
airSlate SignNow helps you fill in and sign documents in minutes, error-free. Choose the correct version of the editable PDF form from the list and get started filling it out.
| Versions | Form popularity | Fillable & printable |
|---|---|---|
| OR Authorization to Release Medical Information 2021 | 4.8 Satisfied (83 Votes) | |
| OR Authorization to Release Medical Information 2015 | 4.8 Satisfied (116 Votes) |
Privacy pitfalls in medical record releases
Attaching the Brown authorization to an unrestricted email thread can expose patient identifiers and the requested medical-record scope to unintended recipients. Leaving the recipient, purpose, or records description incomplete can make the authorization too vague for a provider to honor under HIPAA. Allowing every employee to edit or send the template can change release terms without documented privacy or compliance approval. Failing to retain the signed authorization and audit trail makes it harder to demonstrate consent before releasing protected health information.
Risks of an incomplete medical release
Unauthorized disclosure
Access dispute
Evidentiary weakness
Release refusal
Recommended setup for the Brown authorization
Configure the workflow around patient identity, documented consent, protected health information, and the applicable retention rule.
| Setting | Recommendation |
|---|---|
| Authentication method | Email verification with SMS when required |
| Signature type | Electronic signature with signer intent |
| Audit trail | Retain completed document and audit trail |
| Document retention | 6 years under HIPAA 45 CFR 164.530(j) |
| Encryption | TLS 1.2/1.3 and AES-256 protection |
What the audit trail records
The audit trail links the Brown authorization to signer activity, document integrity, completion events, and evidence retrieval.
Authenticate signer:
Capture timestamp:
Hash document:
Seal record:
Log events:
Export evidence:
Retention schedule for medical release records
Retain the signed Brown authorization and supporting evidence according to HIPAA, state law, litigation holds, and the organization’s records policy.
Six years — HIPAA authorizations
State-required period — medical records
Until hold ends — litigation records
Policy period — revocation history
Policy period — superseded forms
Recordkeeping practices for the Brown form
Retain Authorization To Release Medical Record Information Brown with its signing evidence, scope decisions, and applicable HIPAA documentation controls.
Apply the six-year HIPAA retention rule
Export the audit trail with the form
Use controlled archival access
Track scope and revocation status
Key performance indicators that demonstrate SignNow's proven track record.
Troubleshooting the Brown authorization workflow
Resolve access, field-mapping, HIPAA, plan, and retention questions before releasing protected health information through Authorization To Release Medical Record Information Brown.
Upload the original Brown authorization, then use signNow’s field placement tools to map fields without deleting its release language. If the source PDF is image-based, review every placed field visually before sending, because automatic detection may not identify every handwritten or printed line.
HIPAA compliance requires an appropriate business associate arrangement when signNow handles protected health information for a covered entity. The signNow compliance configuration identifies HIPAA as compliant with a BAA required; confirm the organization’s agreement and privacy program before using the workflow.
The Business plan is listed at $8/user/month with annual billing and includes legally binding eSignatures, templates, and audit trails. The product ground truth also states that paid plans include 100 signature invites per user per year, with overage fees.
If the patient or representative cannot access the email, verify the recipient address, resend the invitation, or use an approved signing link. For sensitive records, add stronger signer authentication where the organization’s policy requires it rather than forwarding the document through personal email.
A signed release does not authorize disclosures beyond the scope written in the Brown form. Check the named recipient, information categories, purpose, expiration, and any revocation before releasing records; HIPAA authorization requirements are addressed in 45 CFR 164.508.
Export the completed document and audit trail from signNow and store them under the organization’s medical-record retention policy. HIPAA documentation requirements generally use six years from creation or the last effective date under 45 CFR 164.530(j).
BE READY TO GET MORE
Get this form now!

If you believe that this page should be taken down, please follow our DMCA take-down process.