Does A Physician Need A Patient's Written Authorization To
Use a Does A Physician Need A Patient's Written Authorization To 2021 template to make your document workflow more streamlined.
What physician authorization covers
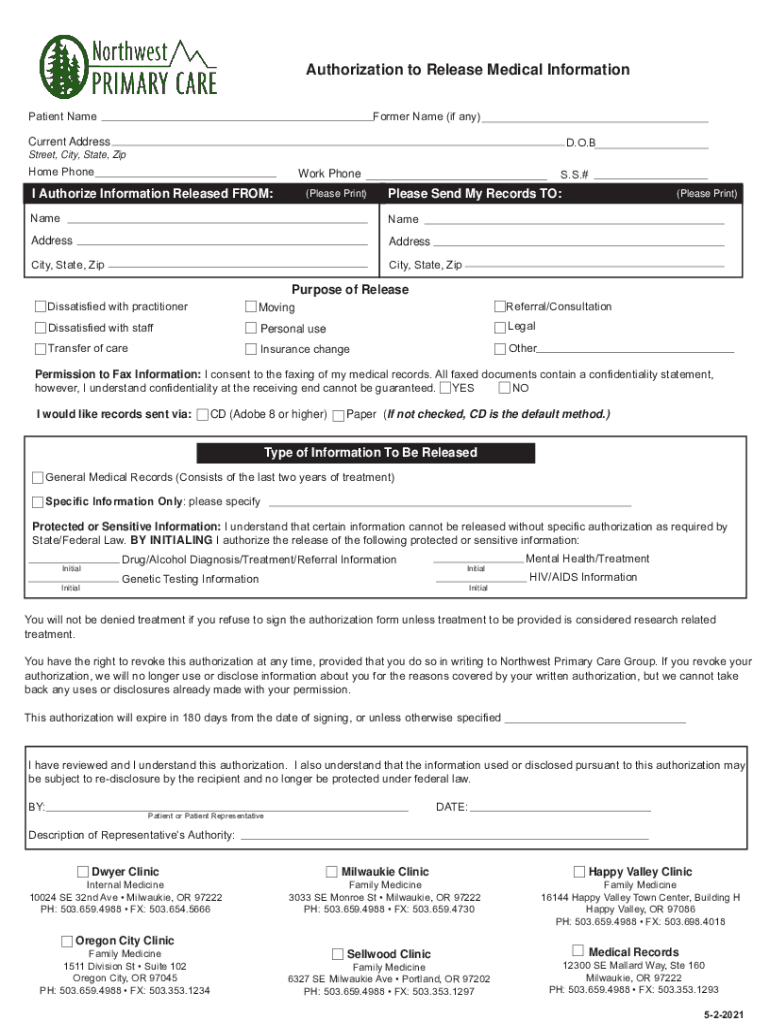
Yes, a physician generally needs a patient’s written authorization to disclose protected health information when HIPAA does not otherwise permit the disclosure. The authorization names the information released, the person or organization receiving it, the purpose, and an expiration date or event. A patient’s treatment consent is not automatically a disclosure authorization. Under 45 CFR 164.508, the authorization must be specific and signed, and the patient may revoke it in writing. Electronic signing can support the record when ESIGN, UETA, and HIPAA requirements are satisfied.
Complete the authorization in signNow
Use this workflow to prepare the physician’s written authorization, route it to the correct parties, and preserve evidence of consent.
Upload document:
Upload the physician’s authorization document. Check fields:
Review detected patient and signature fields. Assign signers:
Assign the patient and physician roles. Send request:
Send the authorization for secure signing. Archive record:
Store the signed record and audit trail.
Recommended authorization workflow setup
Configure the workflow around patient identity, documented consent, restricted access, and retention requirements for protected health information.
| Setting | Recommendation |
|---|---|
| Authentication method | Email verification with admin-managed users |
| Signature type | Electronic signature with documented intent |
| Audit trail | Enabled for every authorization event |
| Document retention | Six years for HIPAA records |
| Encryption | TLS 1.2/1.3 and AES-256 protection |
When written authorization matters
A physician generally needs a patient’s written authorization before disclosing protected health information for purposes outside treatment, payment, or health care operations, subject to HIPAA exceptions. The authorization should identify the information, recipient, purpose, and expiration, and remain separate from treatment consent.

 Best ROI. Our customers achieve an average 7x ROI within the first six months.
 Scales with your use cases. From SMBs to mid-market, airSlate SignNow delivers results for businesses of all sizes.
 Intuitive UI and API. Sign and send documents from your apps in minutes.
Security for patient authorizations
Healthcare privacy:
Security reporting:
Security certification:
Transport encryption:
Storage encryption:
Signer authentication:
How the authorization audit trail works
The audit trail records who handled the patient authorization, what happened, and when, creating a reviewable history for healthcare records.
Authenticate signer:
Capture timestamp:
Hash document:
Seal record:
Track activity:
Retrieve evidence:
Find and fill out the correct does a physician need a patients written authorization to
airSlate SignNow helps you fill in and sign documents in minutes, error-free. Choose the correct version of the editable PDF form from the list and get started filling it out.
| Versions | Form popularity | Fillable & printable |
|---|---|---|
| OR Authorization to Release Medical Information 2021 | 4.8 Satisfied (83 Votes) | |
| OR Authorization to Release Medical Information 2015 | 4.8 Satisfied (116 Votes) |
Mobile options for physician authorizations
Physicians and patients can review Does A Physician Need A Patient's Written Authorization To through signNow mobile apps or supported browsers. iOS 15 or later and Android 10 or later support mobile signing, while Safari, Chrome, and Edge provide browser access.
Mobile apps iOS 15 or later and Android 10 or later Browser access Safari, Chrome, and Edge on iOS and Android Document capture Camera capture for paper authorization documents
Healthcare organizations should apply managed-device controls when authorization records contain protected health information. Confirm access policies, SSO provisioning, API requirements, and retention configuration before connecting signNow with practice systems or storing completed authorizations in a regulated repository.



Privacy pitfalls in physician authorizations
Combining treatment consent with a separate HIPAA authorization can leave the disclosure purpose and recipient unclear. Listing broad categories instead of specific protected health information may make the authorization insufficiently definite. Sending the completed authorization to an unintended recipient can expose protected health information. Allowing unrestricted staff access can conflict with minimum-necessary privacy controls and internal role policies.
Authorization risks and exclusions
Missing authorization
HIPAA violation
Incomplete scope
Notarization demand
Key performance indicators that demonstrate SignNow's proven track record.
Troubleshooting physician authorization workflows
These answers address patient consent, HIPAA disclosure requirements, signNow plan limits, and record-handling questions for physician authorizations.
If the patient cannot complete the request, confirm the recipient email, resend the invitation, or provide a supported browser or signNow mobile app. The Business plan includes legally binding eSignatures and audit trails; stronger authentication options may require an appropriate higher-tier configuration.
A physician’s treatment consent does not automatically authorize disclosure to another person or organization. Under HIPAA 45 CFR 164.508, identify the information, recipient, purpose, and expiration in a separate authorization before routing it through signNow.
For protected health information, signNow states that HIPAA compliance requires a BAA. Confirm the organization has the required BAA and configure access, authentication, retention, and audit controls before sending patient authorizations.
The Business plan is listed at $8 per user per month with annual billing and includes audit trails and templates. It includes 100 signature invites per user per year; higher usage can create overage fees, so review plan terms.
A patient can electronically sign when intent, consent to electronic records, signer attribution, and record retention are established. ESIGN and UETA support electronic signatures, while consumer-facing records may require an ESIGN disclosure and paper-access procedures.
If the authorization includes an expiration date or event, preserve that information in the signed document and audit trail. HIPAA records generally require six years from creation or the last effective date under 45 CFR 164.530(j).
BE READY TO GET MORE
Get this form now!

If you believe that this page should be taken down, please follow our DMCA take-down process.