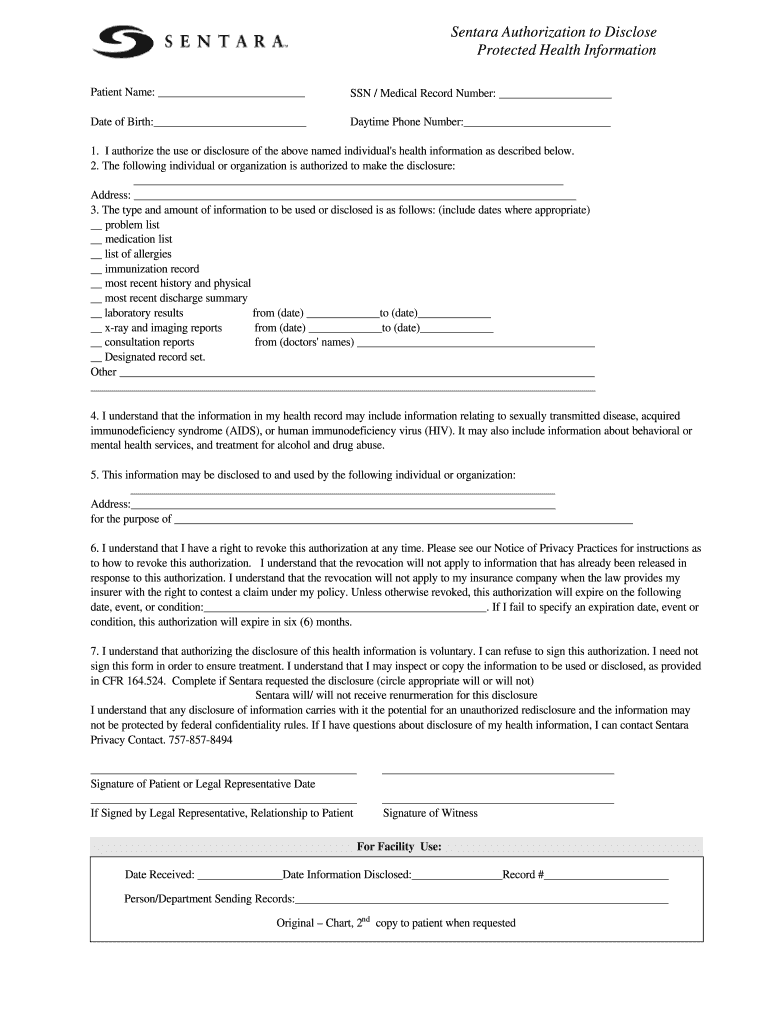
Sentara Authorization To Disclose Form
Use a Sentara Authorization To Disclose Form 0 template to make your document workflow more streamlined.
What the Sentara authorization form does
The Sentara Authorization To Disclose Form gives a patient or authorized person a documented way to permit Sentara to release specified health information to identified recipients. The signer reviews the requested records, recipient, purpose, scope, and authorization terms before signing. With signNow, a sender uploads the form, places or confirms fillable fields, sends it to the signer, and stores the completed document with its audit trail. HIPAA privacy requirements still govern the disclosure, and the authorization should match Sentara’s current instructions and applicable law.
Who benefits from this workflow
Patients, healthcare offices, and enterprise records teams use the form for different disclosure responsibilities.
A patient or personal representative can complete the form to authorize release of defined Sentara records to a named recipient, such as another provider, insurer, attorney, or family member. A healthcare office can send the authorization through signNow, verify the completed fields, and retain the signed record and audit trail with its disclosure-management documentation. A larger health system can standardize templates, assign sending permissions, and connect completed authorizations to controlled records workflows while maintaining HIPAA safeguards and a required BAA.
These tasks are executed by both individual contributors and centralized administrators depending on organizational policy and required controls.
Features for Sentara authorization workflows
Each feature addresses a specific step in preparing, signing, safeguarding, or documenting the Sentara Authorization To Disclose Form.
Field completion
Upload the Sentara authorization and place fields for names, recipient details, disclosure scope, purpose, dates, and signatures without rebuilding the document from paper.
Secure delivery
Send the authorization to a designated signer by email or signing link, reducing manual handoffs while preserving the form’s original disclosure terms.
Audit trail
Capture timestamps, signer actions, and completion history so the organization can review how consent was obtained for the requested Sentara records.
Access controls
Use role-based access and controlled templates to limit who prepares, sends, or downloads patient authorization documents within the organization.
Record storage
Keep completed authorizations with associated audit evidence, supporting internal review of disclosure decisions and record-management procedures.
HIPAA workflow
Use signNow’s HIPAA-compliant configuration with a BAA when the workflow handles protected health information and the organization’s requirements call for it.
How this Sentara form works
The signNow workflow keeps the Sentara authorization connected to its signer, recipient, disclosure purpose, and completion record.
Upload form: Upload the current Sentara form. Check fields: Confirm fields for patient and recipient details. Send securely: Send the authorization to the designated signer. Archive record: Store the signed form and audit trail.
 Best ROI. Our customers achieve an average 7x ROI within the first six months.
 Scales with your use cases. From SMBs to mid-market, airSlate SignNow delivers results for businesses of all sizes.
 Intuitive UI and API. Sign and send documents from your apps in minutes.
Recommended workflow setup
Configure the Sentara authorization workflow around signer identity, consent evidence, protected information, and controlled record access.
| Setting | Recommendation |
|---|---|
| Authentication method | Email verification with SMS OTP |
| Signature type | Electronic signature with signer intent |
| Audit trail | Capture timestamps and signer actions |
| Document retention | Six years for HIPAA documentation |
| Encryption and provisioning | AES-256, TLS, and role-based access |
How the Sentara audit trail works
For this authorization form, signNow records identity, document integrity, signing events, and retrieval details in sequence.
Signer authentication:
Timestamp capture:
Document hashing:
Tamper-evident seal:
Action history:
Trail retrieval:
Find and fill out the correct sentara authorization to disclose form
airSlate SignNow helps you fill in and sign documents in minutes, error-free. Choose the correct version of the editable PDF form from the list and get started filling it out.
| Versions | Form popularity | Fillable & printable |
|---|---|---|
| Sentara HIMROI001 2020 | 4.8 Satisfied (1142 Votes) | |
| Sentara HIMROI001 2017 | 4.8 Satisfied (2209 Votes) |
Signer authentication and certificates
PKI support:
X.509 certificates:
Two-factor authentication:
SMS OTP:
ID verification:
Evidence records:
Platform requirements for Sentara forms
Complete the Sentara Authorization To Disclose Form through a current Chrome, Firefox, Safari, or Edge browser on Windows 10, macOS, iOS, or Android. signNow protects data in transit with TLS 1.2/1.3, and its mobile apps support document review and signing.
Browsers Chrome, Firefox, Safari, Edge Operating systems Windows 10, macOS, iOS, Android Connection security TLS 1.2/1.3 supports secure access
Healthcare organizations should use managed Windows, macOS, iOS, or Android devices when authorization records contain protected health information. Administrators may also evaluate API access, SSO provisioning, and certificate or long-term-validation requirements before deploying the workflow across Sentara-related teams.
Privacy and disclosure pitfalls
Listing a recipient vaguely can make the intended disclosure unclear and complicate HIPAA authorization review. Leaving the records or purpose incomplete may prevent Sentara from determining whether the authorization is sufficiently specific. Sending protected health information to the wrong address creates an access-control and privacy incident. Failing to preserve the signed authorization and audit trail weakens evidence of the signer’s consent.
Retention periods for authorization records
Retention depends on the record’s role and the rule governing it. Apply the specific HIPAA, tax, employment, state, and organizational requirements that actually govern the Sentara disclosure.
Six years for HIPAA records
Six years from effective date
Three years for tax records
Later of three or one year
Longer state requirements
Record-keeping practices for Sentara forms
Preserve the authorization, audit evidence, and retention rationale together so disclosure decisions remain reviewable.
Export the complete evidence package
Apply the correct retention period
Archive protected records securely
Verify disclosure details before release
Sentara authorization troubleshooting
Resolve field, consent, HIPAA, authentication, audit-trail, and plan questions before releasing Sentara records.
Upload the current Sentara Authorization To Disclose Form, then use signNow’s field tools to confirm that patient, recipient, purpose, scope, date, and signature areas are mapped correctly. Do not rely on automatic detection without reviewing every field against the source document.
The signNow Business plan includes legally binding eSignatures, templates, audit trails, and mobile apps at $8 per user per month when billed annually. Business Premium is $15 per user per month annually and adds bulk send and kiosk mode.
When the form contains protected health information, signNow states that HIPAA compliance requires a business associate agreement. Confirm that the organization has the required BAA and configure access, retention, and sharing controls before sending the form.
ESIGN and UETA generally recognize electronic signatures when intent, consent, attribution, and record reproduction are established. For a healthcare authorization, also confirm that the form includes the required disclosure details and satisfies Sentara’s current process.
Use signNow’s audit trail to review signer authentication, timestamps, actions, and completion history. Export the signed authorization and audit evidence together, then store them under the organization’s approved health-record policy.
A subscription plan includes 100 signature invites per user per year, with overage fees after that allowance. Business Premium adds bulk send, while Site License pricing is $1.50 per signature invite for qualifying high-volume use.
Key performance indicators that demonstrate SignNow's proven track record.
BE READY TO GET MORE
Get this form now!

If you believe that this page should be taken down, please follow our DMCA take-down process.